 English.Elpais
Tensions Rise Between Mexico and US Over Drug Trafficking Dispute
Article Content

- •U.S. Ambassador Ronald Johnson criticized Mexican President Claudia Sheinbaum's stance on drug trafficking.
- •Sheinbaum emphasized that ambassadors should respect the internal political affairs of their host countries.
- •Tensions escalated after CIA involvement in a drug lab raid in Chihuahua and U.S. charges against Mexican officials.
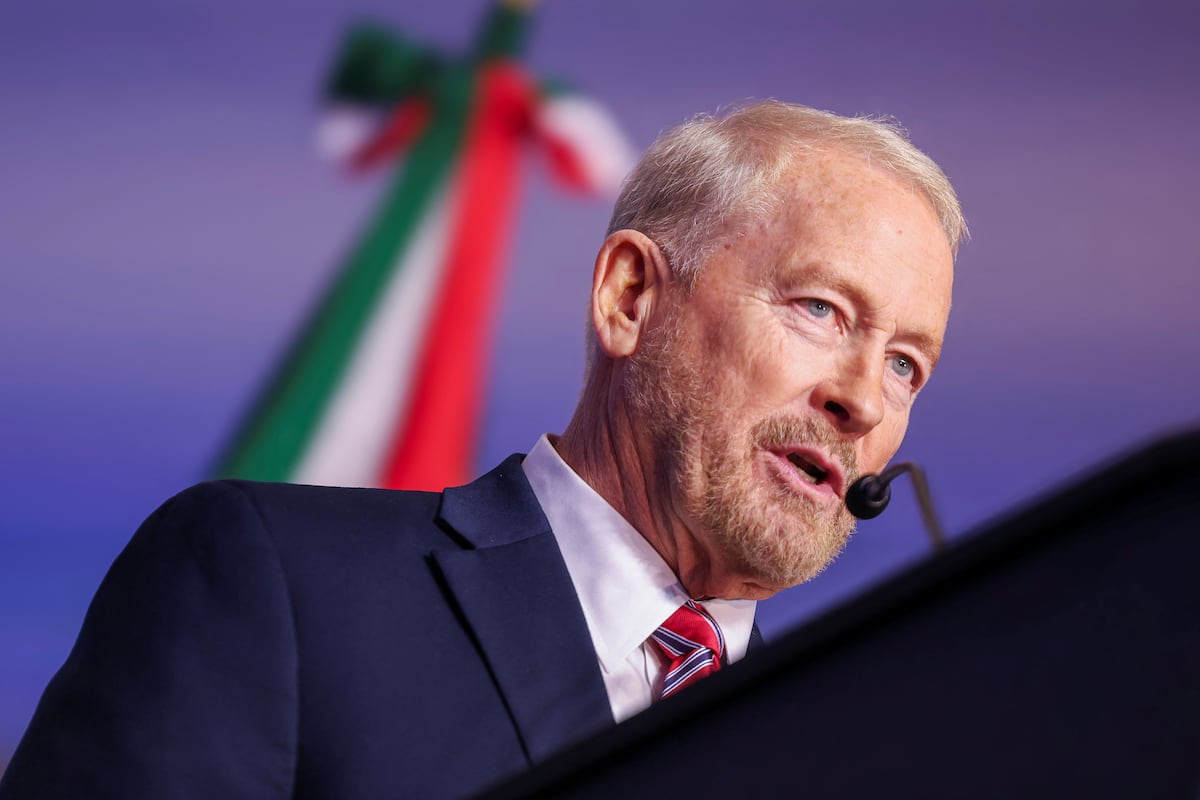
The diplomatic relationship between Mexico and the U.S. has become strained following remarks by U.S. Ambassador Ronald Johnson, who criticized President Claudia Sheinbaum's handling of drug trafficking issues. Sheinbaum rebuked Johnson for interfering in Mexican politics, emphasizing that ambassadors should respect the internal affairs of their host countries. This exchange comes amid heightened tensions over U.S. drug trafficking charges against Mexican officials, including Sinaloa Governor Rubén Rocha. The situation escalated after revelations of CIA involvement in a drug lab raid in Chihuahua without Mexican government approval. Sheinbaum's government has responded by amending the constitution to address foreign interference in elections. The ongoing dispute reflects broader concerns about U.S. influence in Mexico and the fight against drug cartels. The current status remains tense, with both nations navigating a complex security landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…