 Foxnews
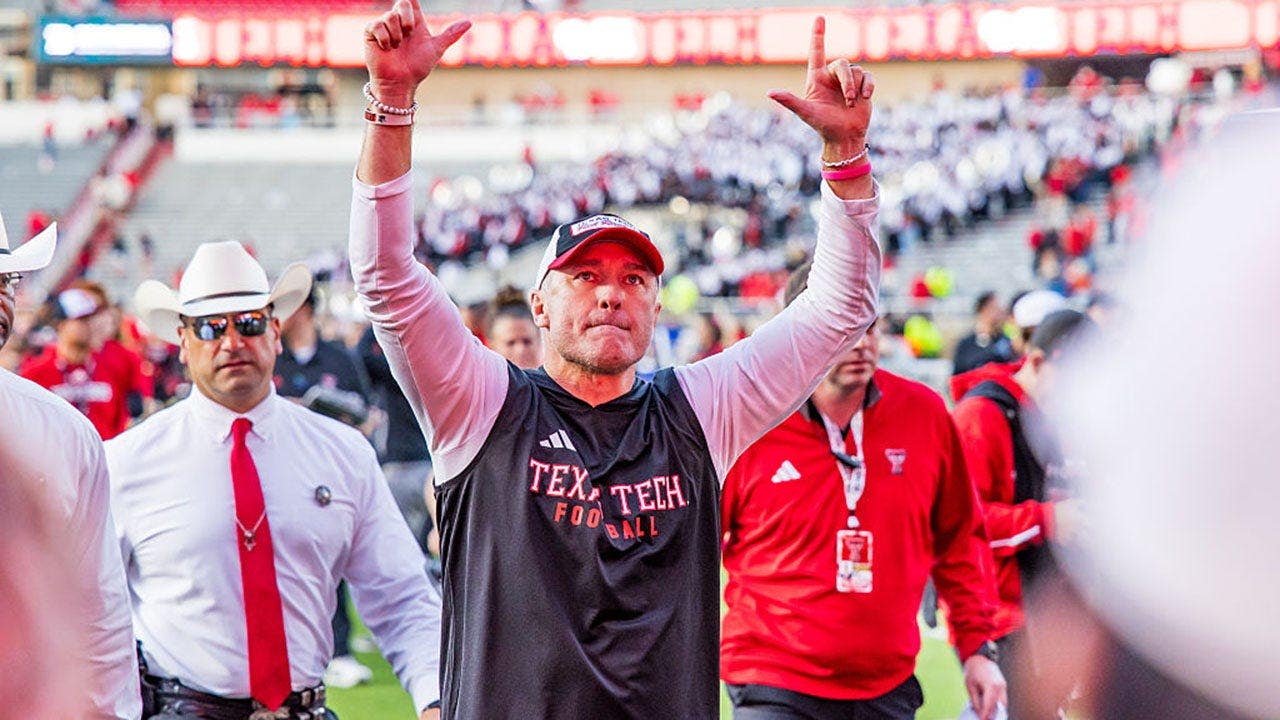
Texas Tech Faces Legal Threats Over Sorsby Betting Controversy
Article Content

- •Brendan Sorsby received a temporary injunction allowing him to play despite a betting scandal.
- •Texas Tech threatens legal action against schools that refuse to schedule games with them.
- •Concerns about antitrust violations are central to Texas Tech's defense against potential sanctions.
Texas Tech quarterback Brendan Sorsby received a temporary injunction allowing him to play despite admitting to betting on college sports. In response, Texas Tech's Board of Regents chair Cody Campbell threatened legal action against any schools or conferences that refuse to schedule games against Texas Tech. The Big Ten and other schools, including Georgia and Nebraska, have already indicated they may not play Texas Tech, citing concerns over Sorsby's eligibility. Campbell argues that such actions constitute collusion and violate antitrust laws. The situation has escalated tensions within college athletics, with Campbell asserting that the backlash is rooted in competition fears against Texas Tech's rising performance. The Big 12 is exploring its legal options regarding potential sanctions against Texas Tech. The current status remains uncertain as discussions continue among conference leaders.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…