 Bleepingcomputer
Threat Actors Compromise NGINX Servers to Redirect Web Traffic
Article Content
Browse articles 
A campaign has been identified where threat actors are compromising NGINX servers to redirect web traffic to malicious sites. The attackers are specifically targeting configurations using the Baota management panel, which is prevalent in Asia. This method involves modifying server settings rather than deploying traditional malware.
Ask AI about this cluster
Answers cite the sources they use
Updated 213d ago How this analysis works
More articles in this cluster (6)
Following this threat?
Track React2Shell and CVE-2025-55182 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Novo Nordisk Data Breach Exploits Hardcoded GitHub Tokens Novo Nordisk suffered a data breach linked to the cyber extortion group FulcrumSec, which exploited hardcoded credentials found in client-side JavaScript across two subdomains. The attackers accessed over 1 terabyte of sensitive data, including experimental drug data and customer records, after gaining entry in June…
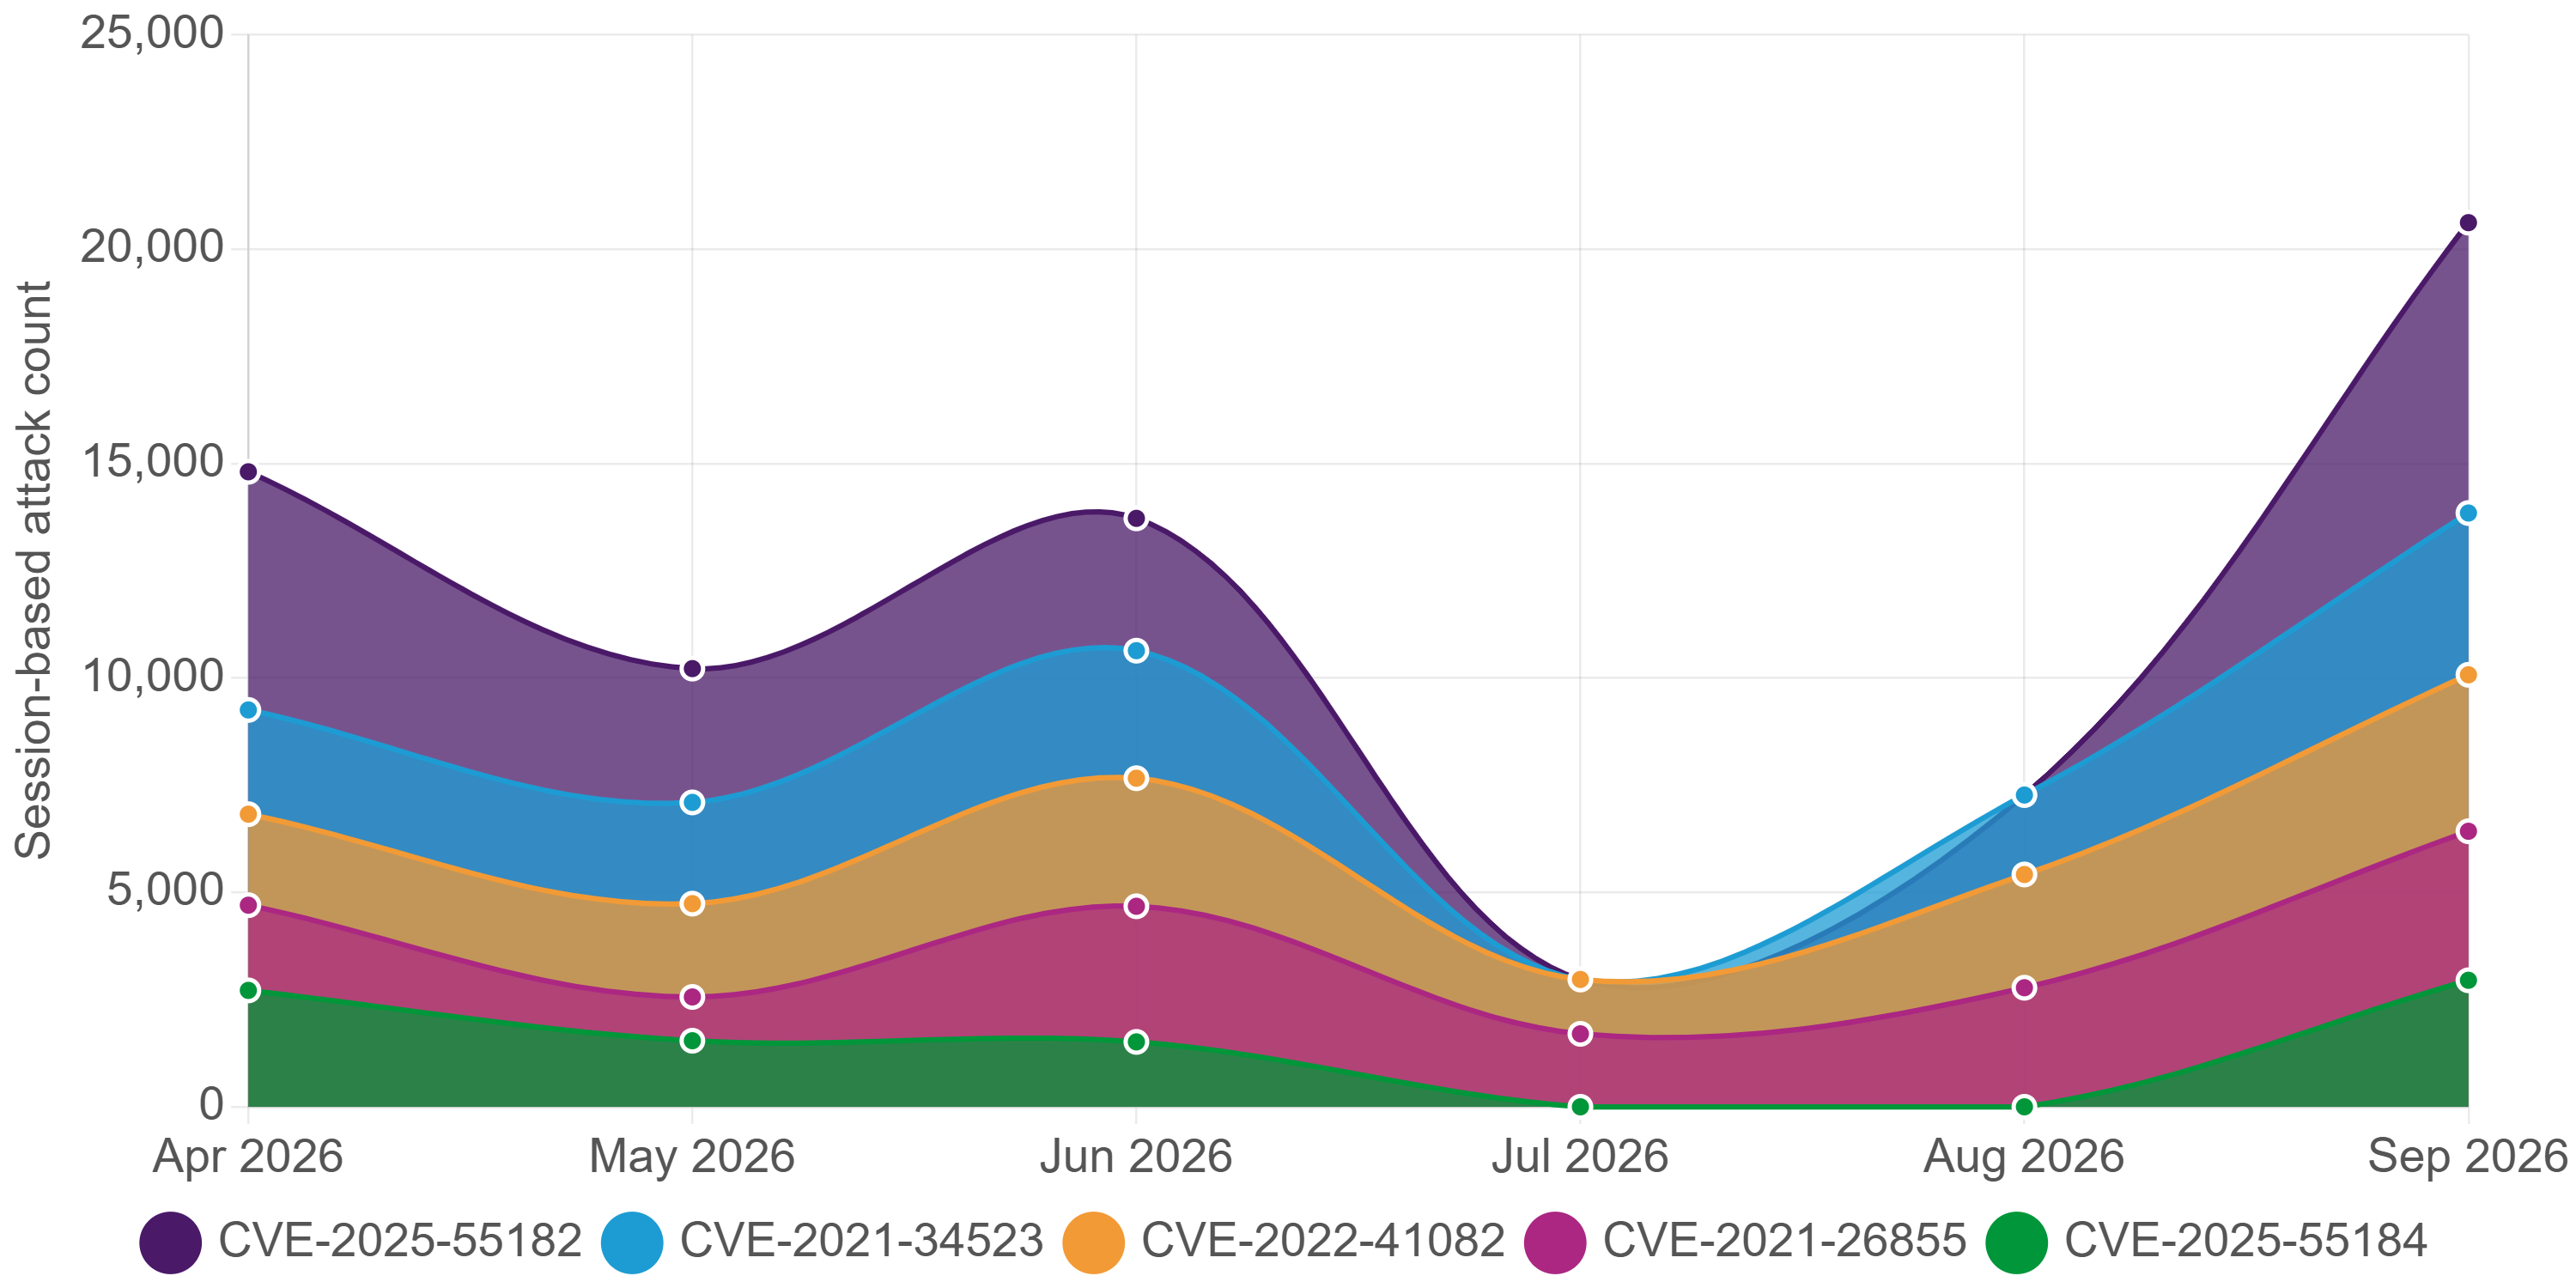 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…