 Thecyberexpress
Three Charged in $170M Nvidia GPU Smuggling Scheme to China
Article Content

- •Three individuals charged for attempting to smuggle $170 million worth of Nvidia GPUs to China.
- •The scheme involved false representations and targeted export-controlled technology.
- •Arrests were made following a lengthy investigation that began in May 2023.
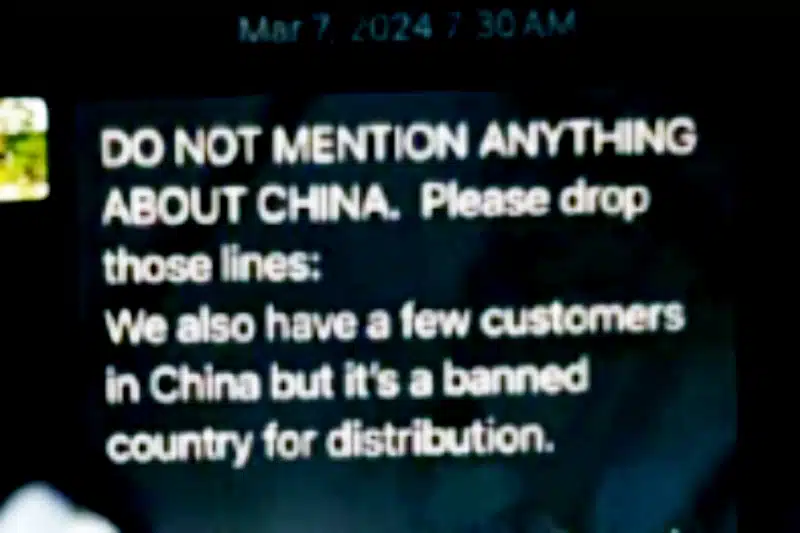
Stanley Yi Zheng, Matthew Kelly, and Tommy Shad English have been charged with conspiracy to commit smuggling and export control violations related to an attempt to illegally export $170 million worth of advanced Nvidia GPUs from a California-based hardware company to China via Thailand. The defendants allegedly sought to acquire 750 servers, 600 of which contained export-controlled chips, by falsely representing themselves as a Thailand-based company. The scheme began in May 2023 and unraveled in January 2024 when the hardware manufacturer raised concerns about the legitimacy of the order. Zheng was arrested on March 22, 2026, while Kelly and English surrendered to authorities on March 25, 2026. The case highlights ongoing efforts to protect U.S. technology from foreign adversaries, particularly in the field of artificial intelligence.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Company-1 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…