 Gbhackers
TimbreStealer Malware Campaign Targets Mexican Companies with Advanced Evasion Techniques
Article Content

- •TimbreStealer malware targets Mexican companies using advanced evasion techniques.
- •Phishing emails deliver ZIP files containing malicious DLLs masquerading as legitimate updaters.
- •The malware employs heavy anti-analysis measures and collects sensitive user data.
A new campaign linked to the TimbreStealer malware targets companies in Mexico, employing advanced evasion techniques. Researchers Euler Neto and Cristóbal Tárraga report that the malware uses DLL side-loading with malicious DLLs sized between 45 and 50 MB, masquerading as legitimate updater files. The initial attack vector is phishing emails delivering ZIP files hosted on DigitalOcean IPs, with filenames referencing Mexican fiscal documents to increase click rates. The malware contains heavy anti-analysis measures, including 27 sections with zeroed content and custom API resolution to avoid detection. It performs extensive data collection from browsers and user data stores, particularly targeting Google Chrome and Microsoft Edge. The campaign echoes tactics observed in a 2024 Cisco Talos report, indicating a sophisticated approach to evade detection. Current status indicates ongoing threats to Mexican companies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track ClickFix and DigitalOcean in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
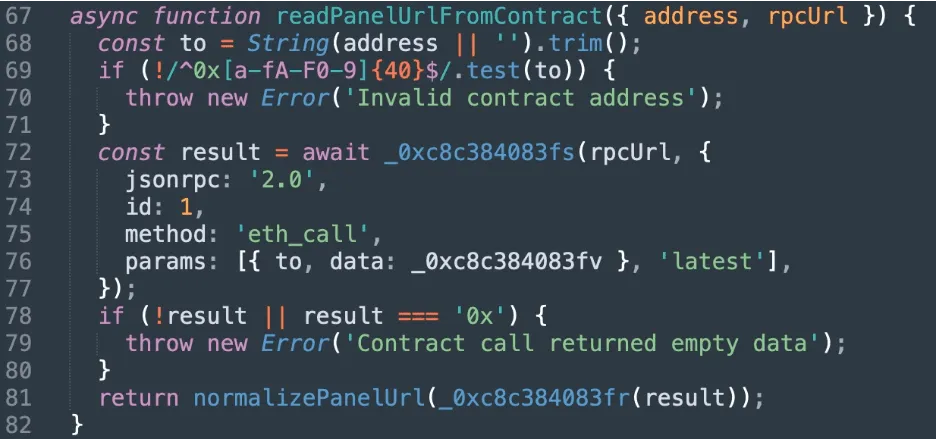 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…