 www.theguardian.com
Trump Administration Moves to Dismantle Ocean Monitoring System
Article Content

- •The Ocean Observatories Initiative is set to be dismantled, affecting over 900 monitoring instruments.
- •The loss of data from the OOI will hinder understanding of critical ocean currents like the AMOC.
- •Democratic lawmakers are mobilizing to oppose the dismantling of this vital climate monitoring system.
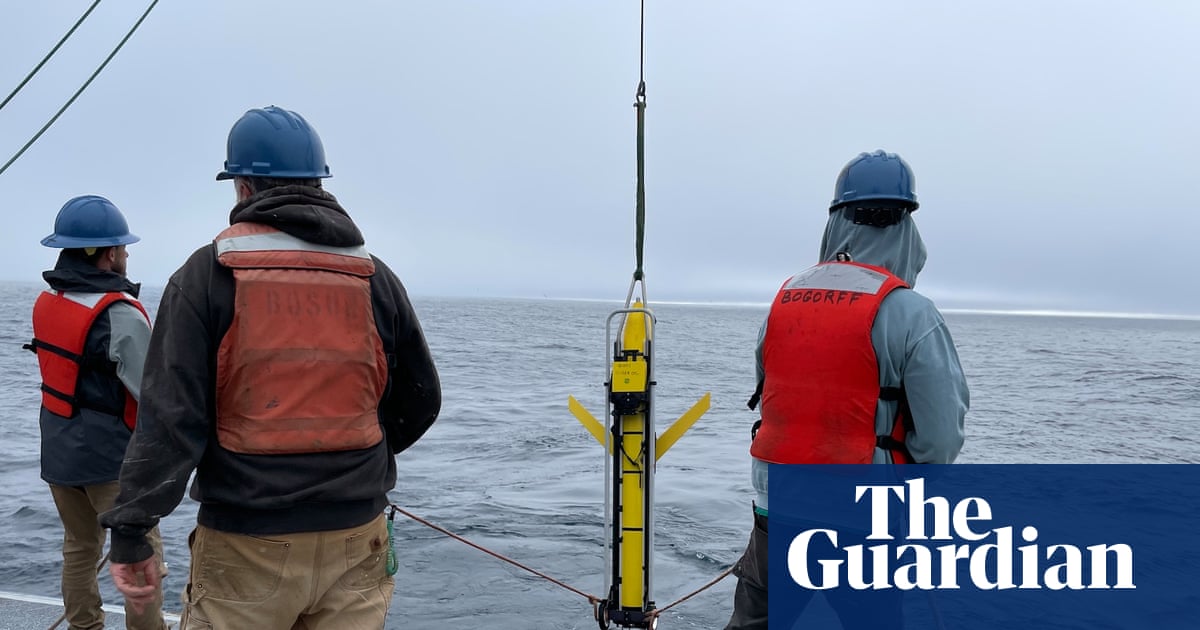
The Trump administration announced plans to dismantle the Ocean Observatories Initiative (OOI), a $368 million network of over 900 instruments that has provided crucial data on ocean health and climate change since 2016. This decision follows the firing of the independent board overseeing the National Science Foundation (NSF) and involves the removal of all in-water infrastructure from various sites along the U.S. coasts and the Irminger Sea. The phased recovery process is expected to take 15 months, resulting in the loss of vital data on ocean currents, including the Atlantic Meridional Overturning Circulation (AMOC), which is critical for climate stability. Scientists and lawmakers have expressed significant concern over the implications of losing this monitoring capability, particularly as the AMOC approaches a potential tipping point. The dismantling reflects a broader rollback of scientific and climate initiatives under the Trump administration.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…