 Kyivpost
Ukraine Calls for UN to Exclude Russia from Peacekeeping Missions Over War Crimes
Article Content

- •Ukraine's UN envoy demands Russia's removal from peacekeeping missions due to war crimes.
- •310 cases of conflict-related sexual violence by Russian forces have been documented by the UN.
- •Melnyk suggests Russia should leave the UN if it rejects findings on its war crimes.
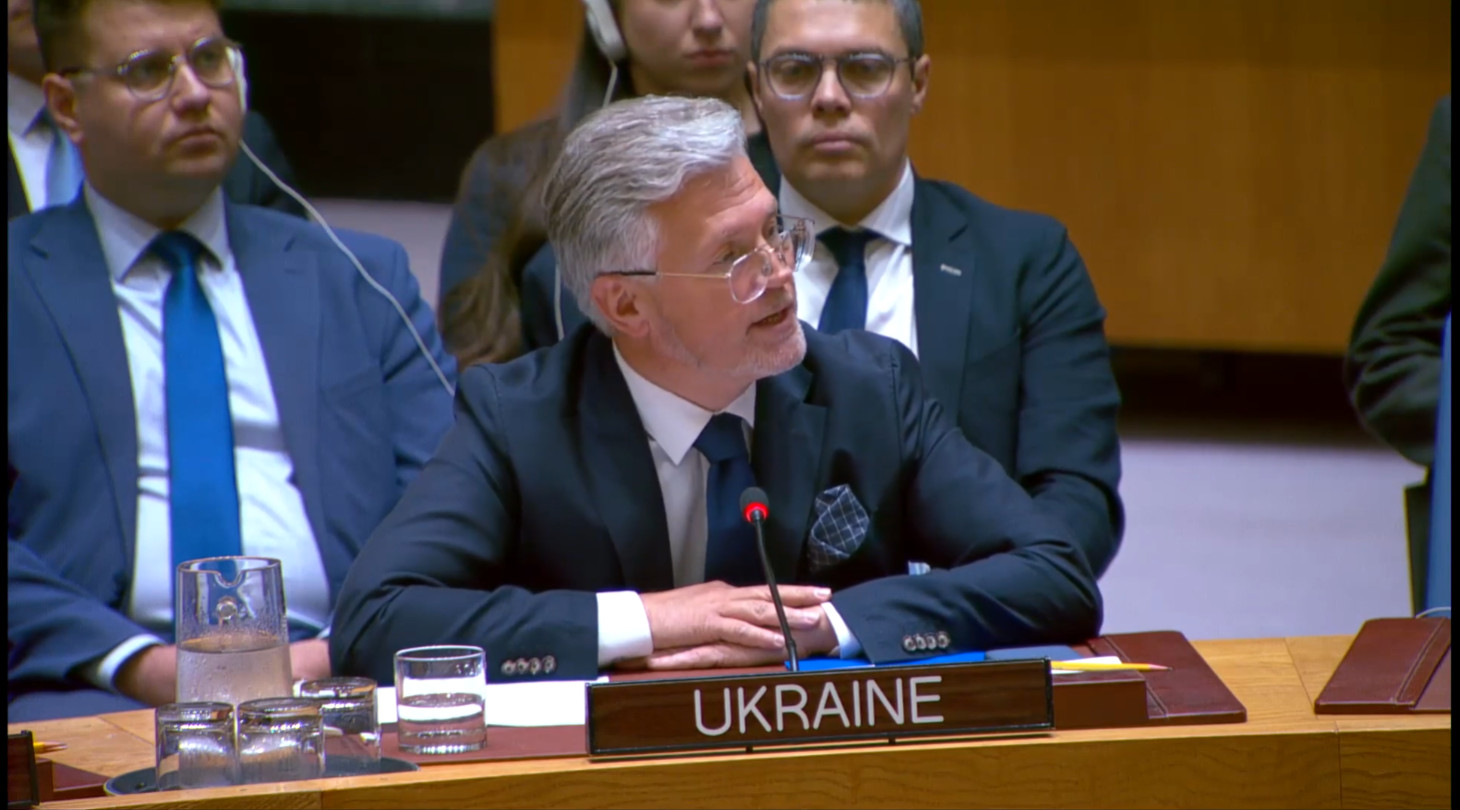
At a UN Security Council meeting, Ukraine’s UN envoy Andriy Melnyk urged the suspension of Russian personnel from peacekeeping missions due to documented cases of conflict-related sexual violence. The UN Secretary-General's report confirmed 310 incidents of such violence attributed to Russian military and security forces since 2014. Melnyk highlighted the systematic nature of these crimes, which include rape and genital mutilation, affecting 280 men, 26 women, and 4 girls. He criticized Russia for rejecting UN findings on its war crimes and suggested that if Russia is uncomfortable with UN resolutions, it should consider leaving the organization. Melnyk emphasized that the documented crimes have been verified by the UN and called for real consequences for Russia's actions. He also mentioned ongoing Russian attacks on Ukrainian cities, including a strike on a nuclear fuel storage facility.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…