 Kyivpost
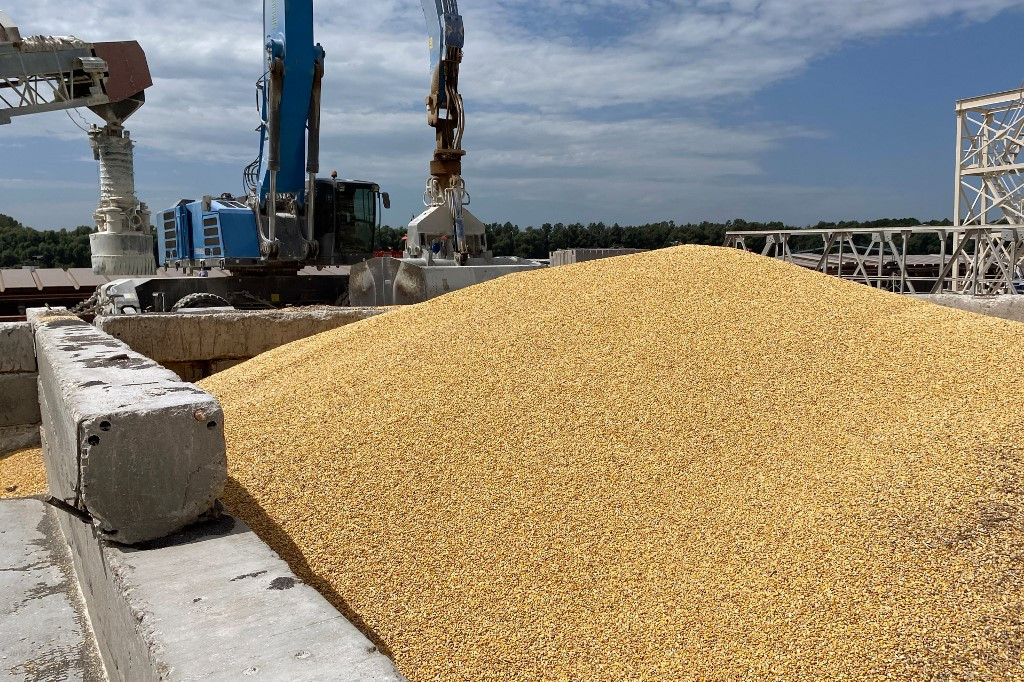
Ukraine Reports 850,000 Tons of Stolen Grain Exported by Russia in 2026
Article Content

- •Ukraine estimates 850,000 tons of stolen grain exported from occupied territories in 2026.
- •Mariupol's port has been repurposed for military logistics and grain theft by Russian forces.
- •International efforts are underway to track and penalize vessels transporting looted grain.
In 2026, Ukraine reported that approximately 850,000 tons of stolen grain have been exported from Russian-occupied territories, with significant shipments originating from the Crimean port of Sevastopol and the Sea of Azov ports of Mariupol and Berdiansk. The Mariupol City Council indicated that nearly 60,000 tons of this grain were exported from Mariupol alone since January 2026, using eight cargo ships. The Kremlin is reportedly developing a long-term strategy to enhance the port's capacity, aiming to solidify its role in military logistics. Ukrainian President Volodymyr Zelensky has initiated a framework to track and penalize vessels involved in transporting looted agricultural products, aligning with US and EU sanctions. Recent diplomatic efforts have led to the rejection of a vessel carrying stolen grain in Israel. The ongoing situation highlights the extensive scale of grain theft and the geopolitical implications of Russia's actions in Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…