 Kyivindependent
Ukraine Strikes Russian Weapons Facility with Flamingo Missiles
Article Content

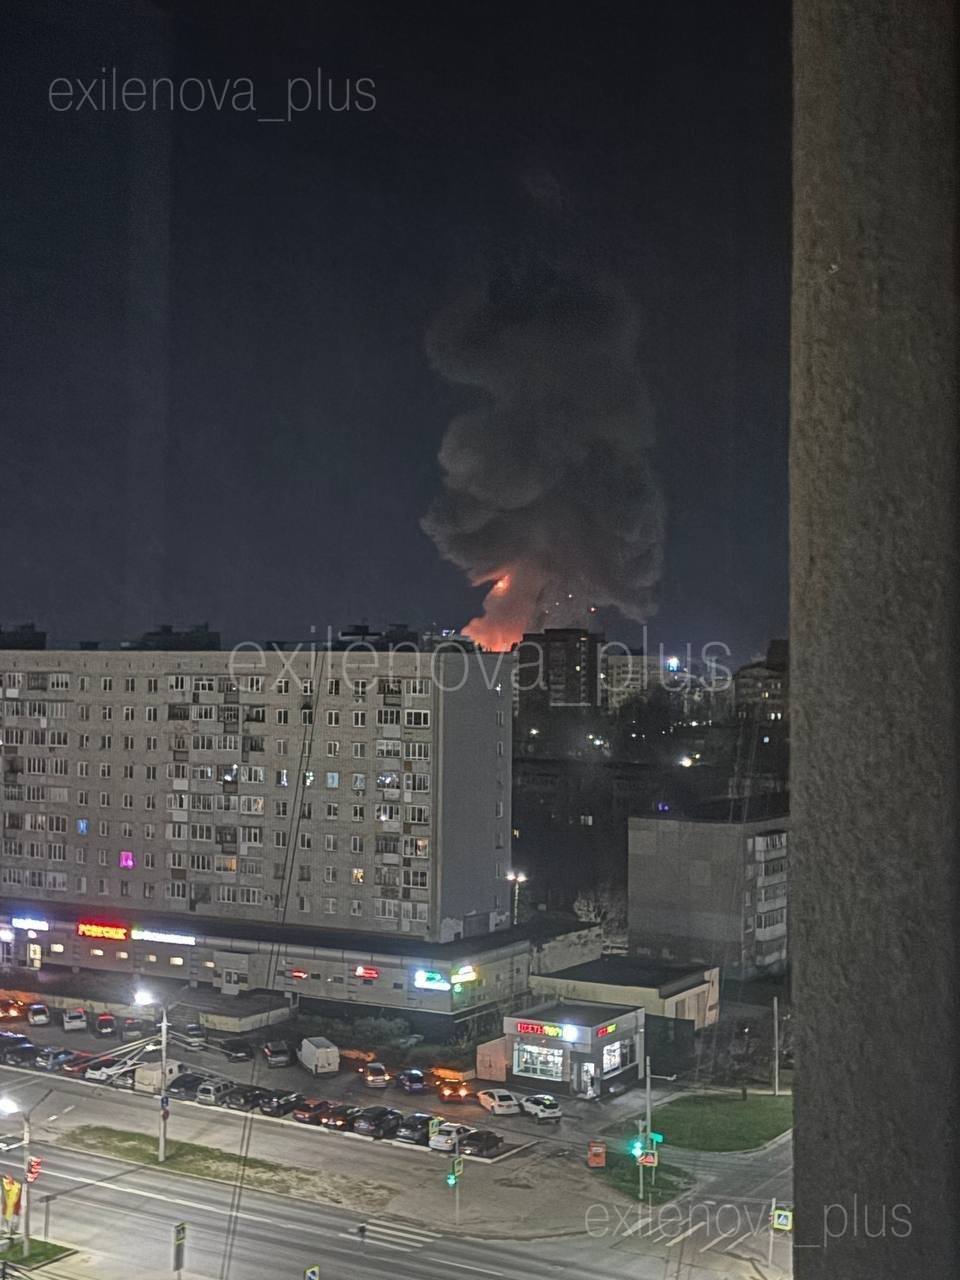
- •Ukrainian Flamingo missiles struck a military facility in Cheboksary on May 5, 2026.
- •The attack resulted in two deaths and 32 injuries, according to Russian state media.
- •This operation demonstrates the operational capability of the FP-5 Flamingo missiles.
On May 5, 2026, Ukrainian forces launched Flamingo cruise missiles targeting a Russian military production facility in Cheboksary, reportedly causing significant damage and casualties. President Zelensky confirmed the strike, stating the missiles covered over 1,500 kilometers. The facility, known for producing components for high-precision weapons, was also targeted alongside one of Russia's largest oil refineries in Kirishi. Local reports indicated that the attack resulted in two fatalities and 32 injuries. Satellite imagery and social media posts corroborate the occurrence of large fires at the site. The strikes are part of a broader military campaign by Ukraine to disrupt Russian military capabilities. This event marks a significant operational use of the FP-5 Flamingo missiles, which have been previously scrutinized for their effectiveness. The situation remains fluid as further attacks are reported.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track JSC VNIIR-Progress in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…