 Jns
U.S. Sanctions Target Iran's Shadow Banking Network Amid Ongoing Tensions
Article Content

- •U.S. sanctions target 35 entities linked to Iran's shadow banking network.
- •Sanctions aim to disrupt financial channels supporting Iran's military and terrorism.
- •Treasury warns financial institutions of severe consequences for engaging with these networks.
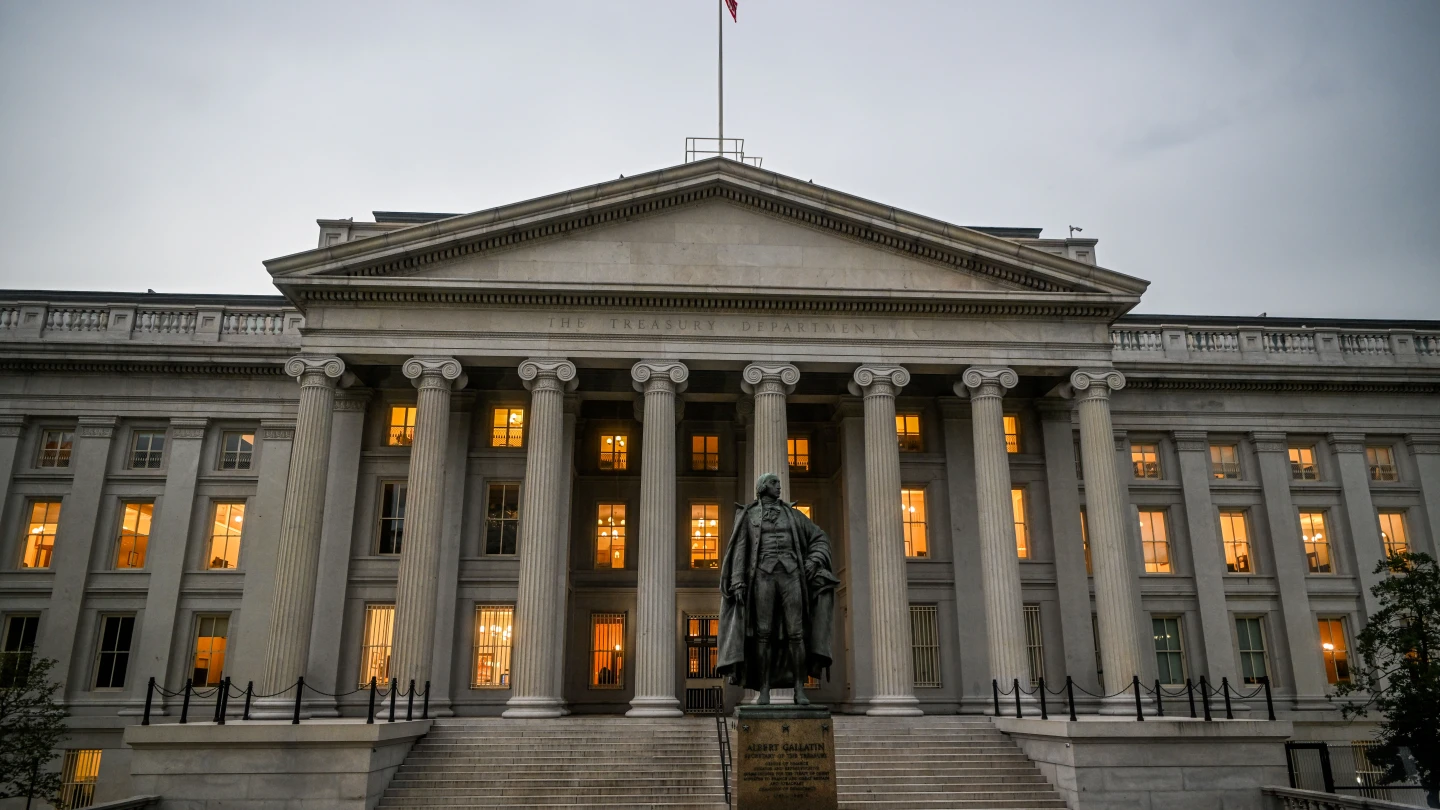
On April 29, 2026, the U.S. Treasury Department sanctioned 35 entities and individuals linked to Iran's shadow banking system as part of the 'Economic Wrath' campaign. These sanctions aim to disrupt financial networks that facilitate tens of billions of dollars in sanctions evasion and support for terrorism. Treasury Secretary Scott Bessent emphasized that these networks are critical for Iran's armed forces, enabling activities that threaten global trade and security. The sanctions specifically target companies like Farab Soroush Afagh Qeshm Company, which aids in Iranian oil sales, and other front companies associated with Iranian banks. This action is part of the broader 'Maximum Pressure' policy against Iran, which has intensified since 2025, affecting numerous individuals and entities involved in Iran's financial operations. The U.S. government warns that financial institutions engaging with these networks face severe consequences. The sanctions reflect ongoing geopolitical tensions and the U.S. commitment to countering Iran's military capabilities and terrorism sponsorship.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (44)
Following this threat?
Track Farab Soroush Afagh Qeshm Company in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…