 Securityarsenal
Version Control Systems Targeted in Supply Chain Attacks
Article Content

- •Version Control Systems are increasingly targeted in supply chain attacks.
- •Organizations often lack sufficient telemetry from VCS, relying heavily on endpoint data.
- •Pre-incident log streaming configurations are crucial for real-time detection of compromises.
Recent cybersecurity incidents have highlighted the vulnerabilities of Version Control Systems (VCS) like GitHub, GitLab, Bitbucket, and Azure DevOps. Attackers are exploiting these platforms as both targets and delivery mechanisms for supply chain intrusions, as seen in campaigns like tj-actions GitHub Actions compromise and Salesloft Drift OAuth token theft. The Wiz CIRT has released a DFIR cheatsheet to assist organizations in understanding telemetry and configurations necessary for effective incident response. Many organizations lack adequate logging from VCS, relying instead on endpoint telemetry, which leaves significant blind spots. The articles emphasize the need for pre-incident log streaming configurations to detect compromises in real time. Attackers often use compromised tokens to access repositories quietly, making detection challenging. The scope of impact includes potential unauthorized access to sensitive source code and secrets stored in repositories. Security teams are urged to enhance their monitoring capabilities and prepare for incidents involving VCS.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track TeamPCP and Shai-hulud in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
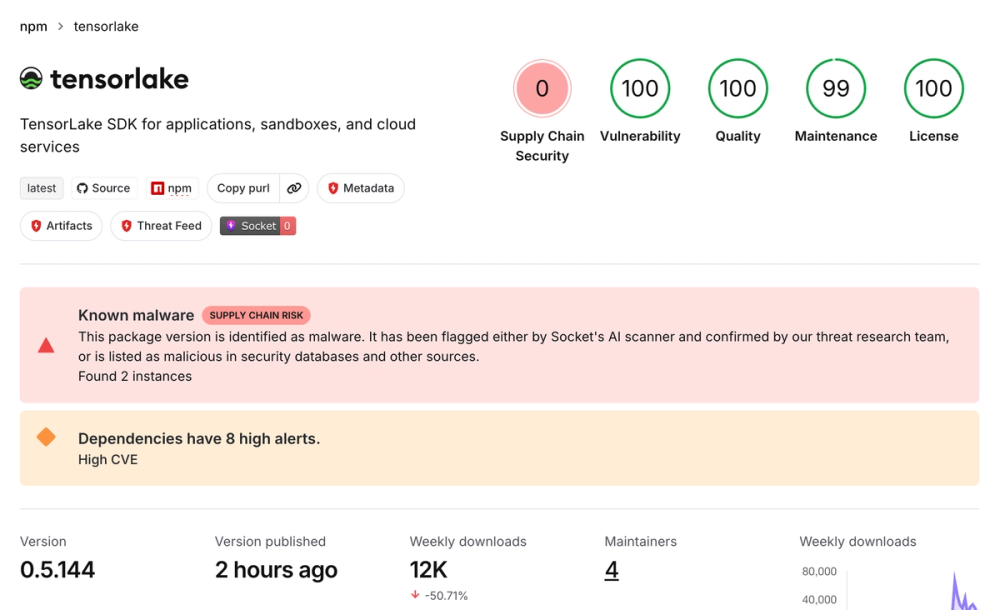 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…