 Gbhackers
Warden Stealer Malware Targets AI Agents for Data Theft
Article Content

- •Warden Stealer targets AI agents and developer credentials.
- •Version 1.9 supports explicit theft of AI coding agent tokens.
- •The malware employs advanced evasion techniques to avoid detection.
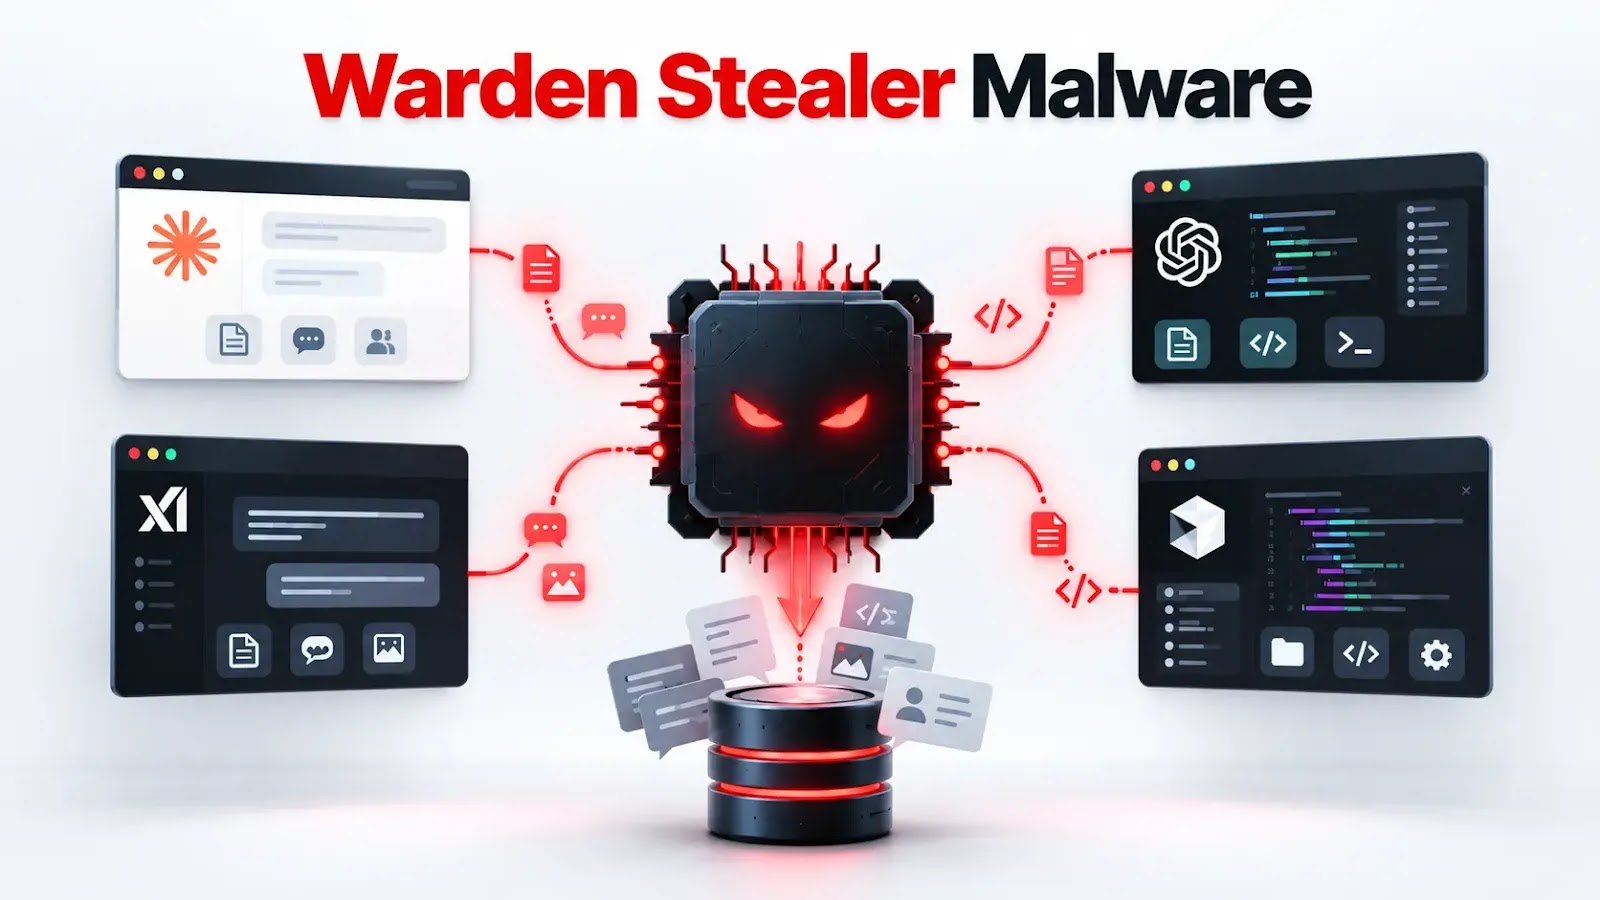
Warden Stealer, a sophisticated malware-as-a-service, is actively targeting AI agents like Claude, Codex, Grok, and Cursor to steal sensitive developer data. This Rust-based infostealer collects configuration files, tokens, and conversation histories, posing a significant threat to organizations using AI tools. The malware, which has been gaining traction on dark web forums, employs advanced evasion techniques and a proprietary binary transfer protocol to bypass detection. Version 1.9, released on September 29, explicitly supports the theft of AI coding agent tokens, enabling attackers to gain direct access to premium AI models and organizational workspaces. Researchers have linked Warden to CallbackBeaver due to technical similarities. The malware's capabilities extend to over 360 applications, including messaging apps and password managers, making it a versatile threat. The campaign highlights a shift in focus from traditional infostealers to targeting AI tools, which are increasingly seen as valuable sources of sensitive information.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CallbackBeaver in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What AI agents are affected?
How does Warden evade detection?
What data can Warden steal?
Continue Reading
 Sauron Loader Malware Targets German Organizations via DLL Side-Loading Sauron Loader, a new malware loader, has been identified in attacks against German organizations. It operates as a final stage in intrusion chains initiated through social engineering and ClickFix campaigns. The malware is distributed via malicious MSI packages and is designed to gather telemetry from host systems and…
 Cisco Talos Reports ClickFix Attacks Targeting Cryptocurrency Traders Cisco Talos has identified two ClickFix attack campaigns that exploit trusted services to deceive victims into executing malicious code. The first campaign, active since October 2025, targets cryptocurrency traders with fake security reports, leading them to paste JavaScript into their browsers, which then retrieves…