Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
CISA has added two vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog due to evidence of active exploitation. CVE-2026-102489, a session fixation vulnerability in Zammad, and CVE-2026-102490, an improper privilege management vulnerability in Zammad, were added on 2026-10-02. Additi...
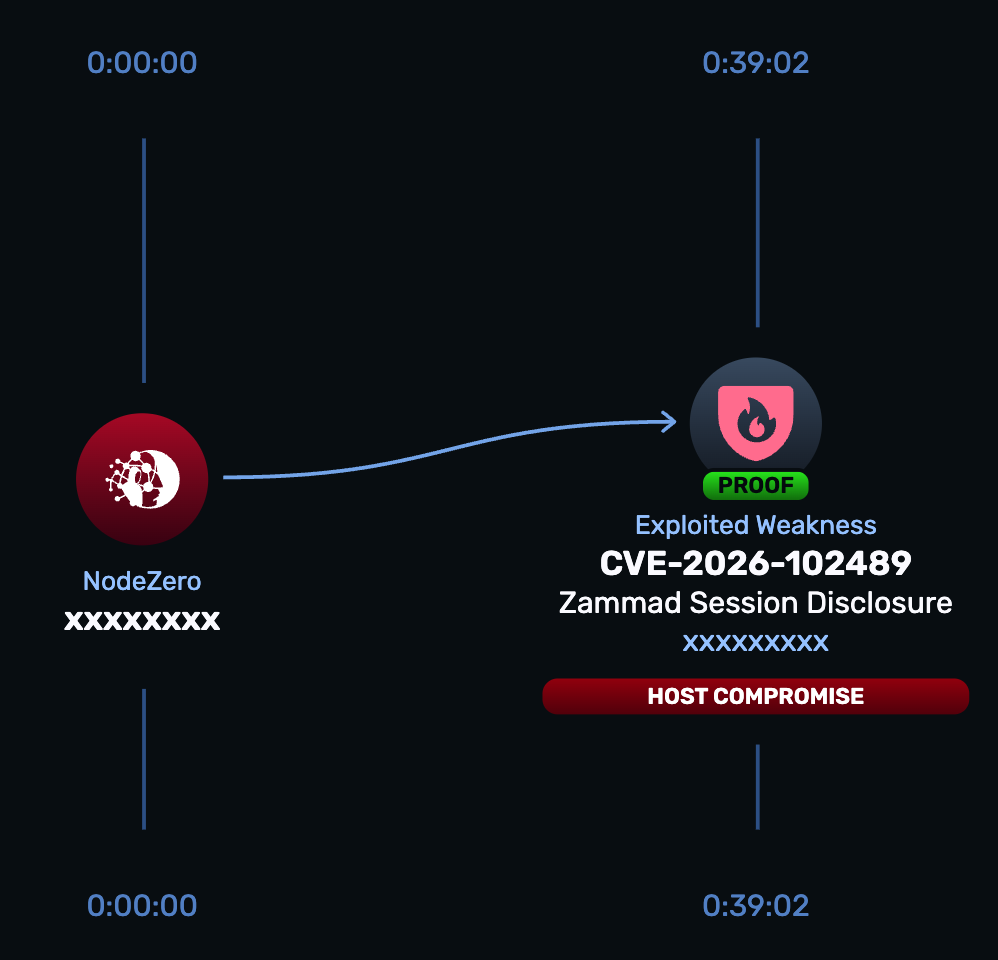
Two vulnerabilities (CVE-2026-102489 and CVE-2026-102490) have been identified in the Zammad ticketing system, affecting all versions up to 7.1.3. CVE-2026-102489 allows session hijacking leading to remote code execution in versions 6.3.0 to 6.5.4, while CVE-2026-102490 enables local privilege escal...
Arista Networks has patched a critical SQL injection vulnerability, CVE-2026-114625, in its VeloCloud Orchestrator (VCO) that allows authenticated users to escalate privileges to superuser status. The flaw, rated 9.9 on the CVSS scale, has been actively exploited in the wild, affecting on-premises d...
A proof-of-concept (PoC) exploit for CVE-2026-102489, a vulnerability in Zammad, has been released, allowing unauthenticated attackers to steal session cookies and execute remote code. This flaw was exploited in a September breach at the Dutch Institute for Vulnerability Disclosure (DIVD), where att...