Skip to content
Product
Use it
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Recipes
Runnable examples for the free key.
Free feeds
RSS, ransomware feed, IOC blocklist, MISP — no key.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
The data
Incident records
900 articles a day become ~70 scored incidents.
Dark web
First-party leak-site collection: victims, groups, markets.
Validated IOCs
Indicators with a false-positive gate; STIX, MISP, CSV.
Vulnerabilities
CVEs with EPSS, KEV and exploit status.
Entity graph
Actors, malware, CVEs, companies — pivotable.
For teams
For service providers
Per-client feeds, alerts and branded digests.
Use cases
How teams and builders use the corpus.
About ThreatCluster
What it is and how it is built.
Pricing
Docs
Reference
OpenAPI (Swagger)
Every endpoint, parameter and response model.
ReDoc
The same reference, long-form.
Examples on GitHub
curl, Python and Node quickstarts; daily spec snapshot.
Guides
Quickstart & plans
Key, scopes, budgets, tiers.
Integrations
Splunk, Sentinel, Elastic, agents and terminals, step by step
Export formats
STIX 2.1, MISP, CSV, text.
CLI setup
Install, log in, wire an agent.
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Recipes
Free feeds
CLI & agents
The data
Incident records
Dark web
Validated IOCs
Vulnerabilities
Entity graph
For teams
For service providers
Use cases
About ThreatCluster
Docs
OpenAPI (Swagger)
ReDoc
Examples on GitHub
Quickstart & plans
Integrations
Export formats
CLI setup
Pricing
Contact
Get a free key
Sign in
Back
CWE-639 - Authorization Bypass Through User-Controlled Key (IDOR)
CWE Weakness
Threat entity extracted from intelligence sources
Oct 20: 0 mentions
Oct 21: 0 mentions
Oct 22: 2 mentions
Oct 23: 0 mentions
Oct 24: 1 mention
Oct 25: 0 mentions
Oct 26: 0 mentions
Oct 20
Oct 23
Oct 26
Entities
›
cwe
›
CWE-639 - Authorization Bypass Through User-Controlled Key (IDOR)
Frequency
16
occurrences
First Seen
May 29, 2026
Last Seen
October 24, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Malware
Anubis
Sphinx
Tools
Burp Suite
GitHub Actions
GitHub Agentic Workflows
Gitleaks
Semantic Kernel
Semgrep
TruffleHog
CVEs
CVE-2026-101329
CVE-2026-101331
CVE-2026-102404
CVE-2026-102406
CVE-2026-102413
CVE-2026-103008
CVE-2026-103009
CVE-2026-103360
Regions
China
Germany
Iran
North Korea
Russia
Sectors
Critical Manufacturing
Energy
Financial Services
Government Services And Facilities
Healthcare
Healthcare And Public Health
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
1
IA
Initial Access
T1566.001 - Spearphishing Attachment
3
EX
Execution
T1059 - Command and Scripting Interpreter
T1047 - Windows Management Instrumentation
T1053 - Scheduled Task/Job
4
PE
Persistence
T1505.003 - Web Shell
T1543.003 - Windows Service
T1547 - Boot Or Logon Autostart Execution
T1574 - Hijack Execution Flow
1
PE
Priv Esc
T1055 - Process Injection
-
DE
Defense Evasion
No techniques detected
1
CA
Cred Access
T1003 - OS Credential Dumping
-
DI
Discovery
No techniques detected
1
LM
Lateral Mov
T1021 - Remote Services
-
CO
Collection
No techniques detected
1
C2
C2
T1071 - Application Layer Protocol
2
EX
Exfil
T1041 - Exfiltration Over C2 Channel
T1567.002 - Exfiltration to Cloud Storage
1
IM
Impact
T1486 - Data Encrypted for Impact
17
techniques detected across
9
tactics
Related Clusters (6)
Multiple Critical Vulnerabilities Exploited in SonicWall and SharePoint Systems
Jul 28
·
1 sources
75
Elastic Addresses 14 Security Flaws, High-Severity Kibana Vulnerability Disclosed
Oct 8
·
2 sources
61
LingGuo-Drama Vulnerability Enables Full Account Takeover
Oct 17
·
0 sources
57
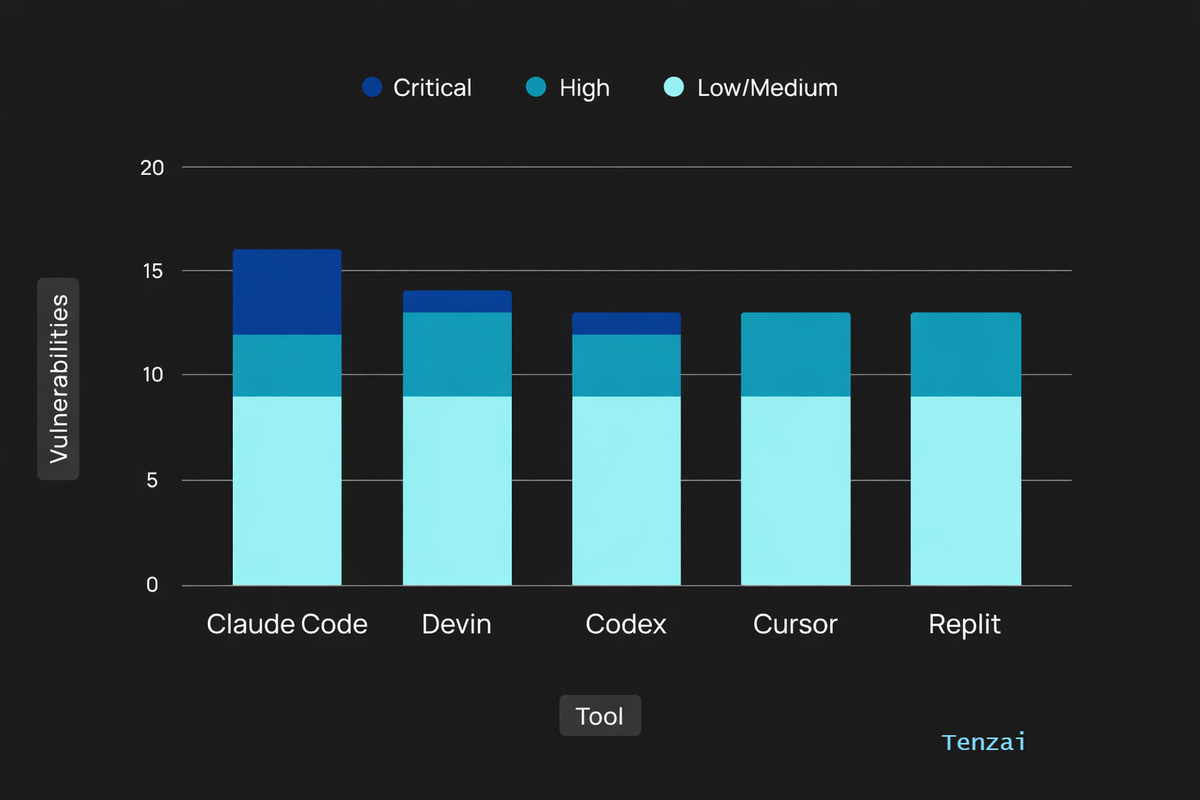
Vulnerabilities in Vibe-Coded Applications Highlighted
Jun 1
·
1 sources
52
N8n Vulnerabilities Lead to Credential Disclosure and Tampering Risks
Oct 1
·
0 sources
46
Multiple Vulnerabilities in Trigger.dev Versions Prior to 4.5.6 and 4.6.2
4d ago
·
0 sources
45
Prev
1 / 2
Next
Related Articles (16)
CVE-2026-115546
trust.okta.com
·
2d ago
Siemens RUGGEDCOM CROSSBOW
Cisa
·
4d ago
Trigger Dev Before 4.5.6 Cross Organization Schedule Deletion Via Unscoped Friendlyid Lookup
www.vulncheck.com
·
4d ago
Apipark Through 1.9.7 Beta Cross Team Authorization Bypass Via Team Query Parameter
www.vulncheck.com
·
Oct 17
Lingguo Drama Broken Access Control
hackmd.io
·
Oct 17
Apipark Cross Team Service App Authz Bypass
hackmd.io
·
Oct 17
Crmeb Gift Order Idor Takeover
hackmd.io
·
Oct 16
IBM Security Bulletin, Langflow OSS multiple vulnerabilities
www.ibm.com
·
Oct 14
Elastic Patches 14 Security Flaws, Including One Enabling Cross
Gbhackers
·
Oct 7
N8n Before 2.39.6 And 2.40 X Before 2.40.1 Credential Disclosure Via Node Tool Introspection
www.vulncheck.com
·
Oct 1
115
github.com
·
Sep 7
>> Read this brief on krypteiasec.com
krypteiasec.com
·
Jul 29
CVE-2026-44207 CVE Vulnerability Disclosures / 1d Frappe is a full-stack web application framework. Prior to versions 15.107.0 and 16.17.0, an IDOR vulnerability allows authenticated users to access other users' email configuration details. This issue has been patched in versions 15.107.0 and 16.17.0.
cve.report
·
Jun 13
CVE-2026-7787 - Unauthenticated Session History Access via Public Flow Execution
Cvefeed
·
Jun 11
CVE-2026-7201 TheHackerWire / 6h Attack Vector How the vulnerability can be exploited Network Successful exploitation requires knowledge of values that are not generally exposed to low-privileged users.
www.thehackerwire.com
·
Jun 3
5 Vulnerabilities in Every Vibe-Coded App
Strobes.Co
·
May 29
Prev
1 / 4
Next
Related Entities
Data Breach
Zero-day Exploit
DDoS
Denial of Service
Improper Authentication
Prompt Injection
Ransomware
Sql Injection
Langflow
Noma Labs
Nutanix
Okta