 Securityaffairs
900 Sangoma FreePBX Instances Compromised by CVE-2025-64328 Exploitation
Article Content
Browse articles 
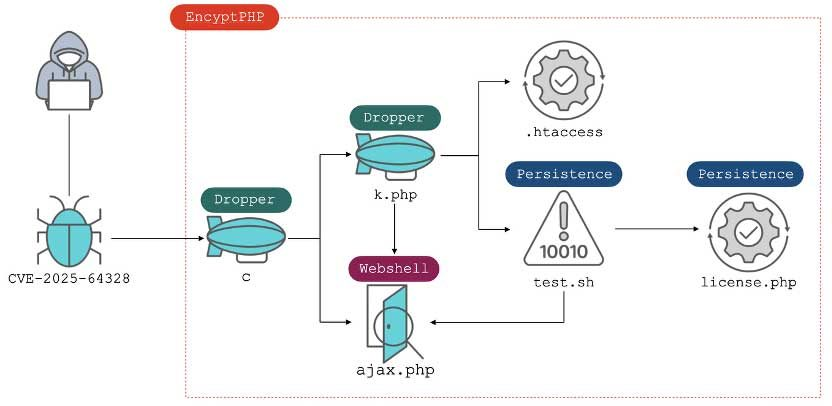
Attackers exploited CVE-2025-64328, a command injection vulnerability, affecting 900 Sangoma FreePBX systems. The exploitation resulted in the installation of web shells, with hundreds of instances remaining compromised since attacks began in December 2025.
Ask AI about this cluster
Answers cite the sources they use
Updated 211d ago How this analysis works
Timeline
2025-11-07
CVE-2025-64328 published
2025-11-16
First public PoC released
2025-12-01
Attacks on Sangoma FreePBX instances began
2026-02-03
CVE-2025-64328 added to CISA KEV for active exploitation
2026-03-01
900 Sangoma FreePBX systems reported infected
More articles in this cluster (5)
Following this threat?
Track APT41, EncystPHP and Sangoma in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Chinese TA419 Group Targets AI Policy Experts with Phishing Campaigns The Chinese cyberespionage group TA419 has been targeting U.S. AI policy experts through credential phishing campaigns. These attacks, documented by Proofpoint, involved impersonating a former White House OSTP official and prominent economists to gain access to sensitive accounts. The phishing tactics employed…
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…