 trufflesecurity.com
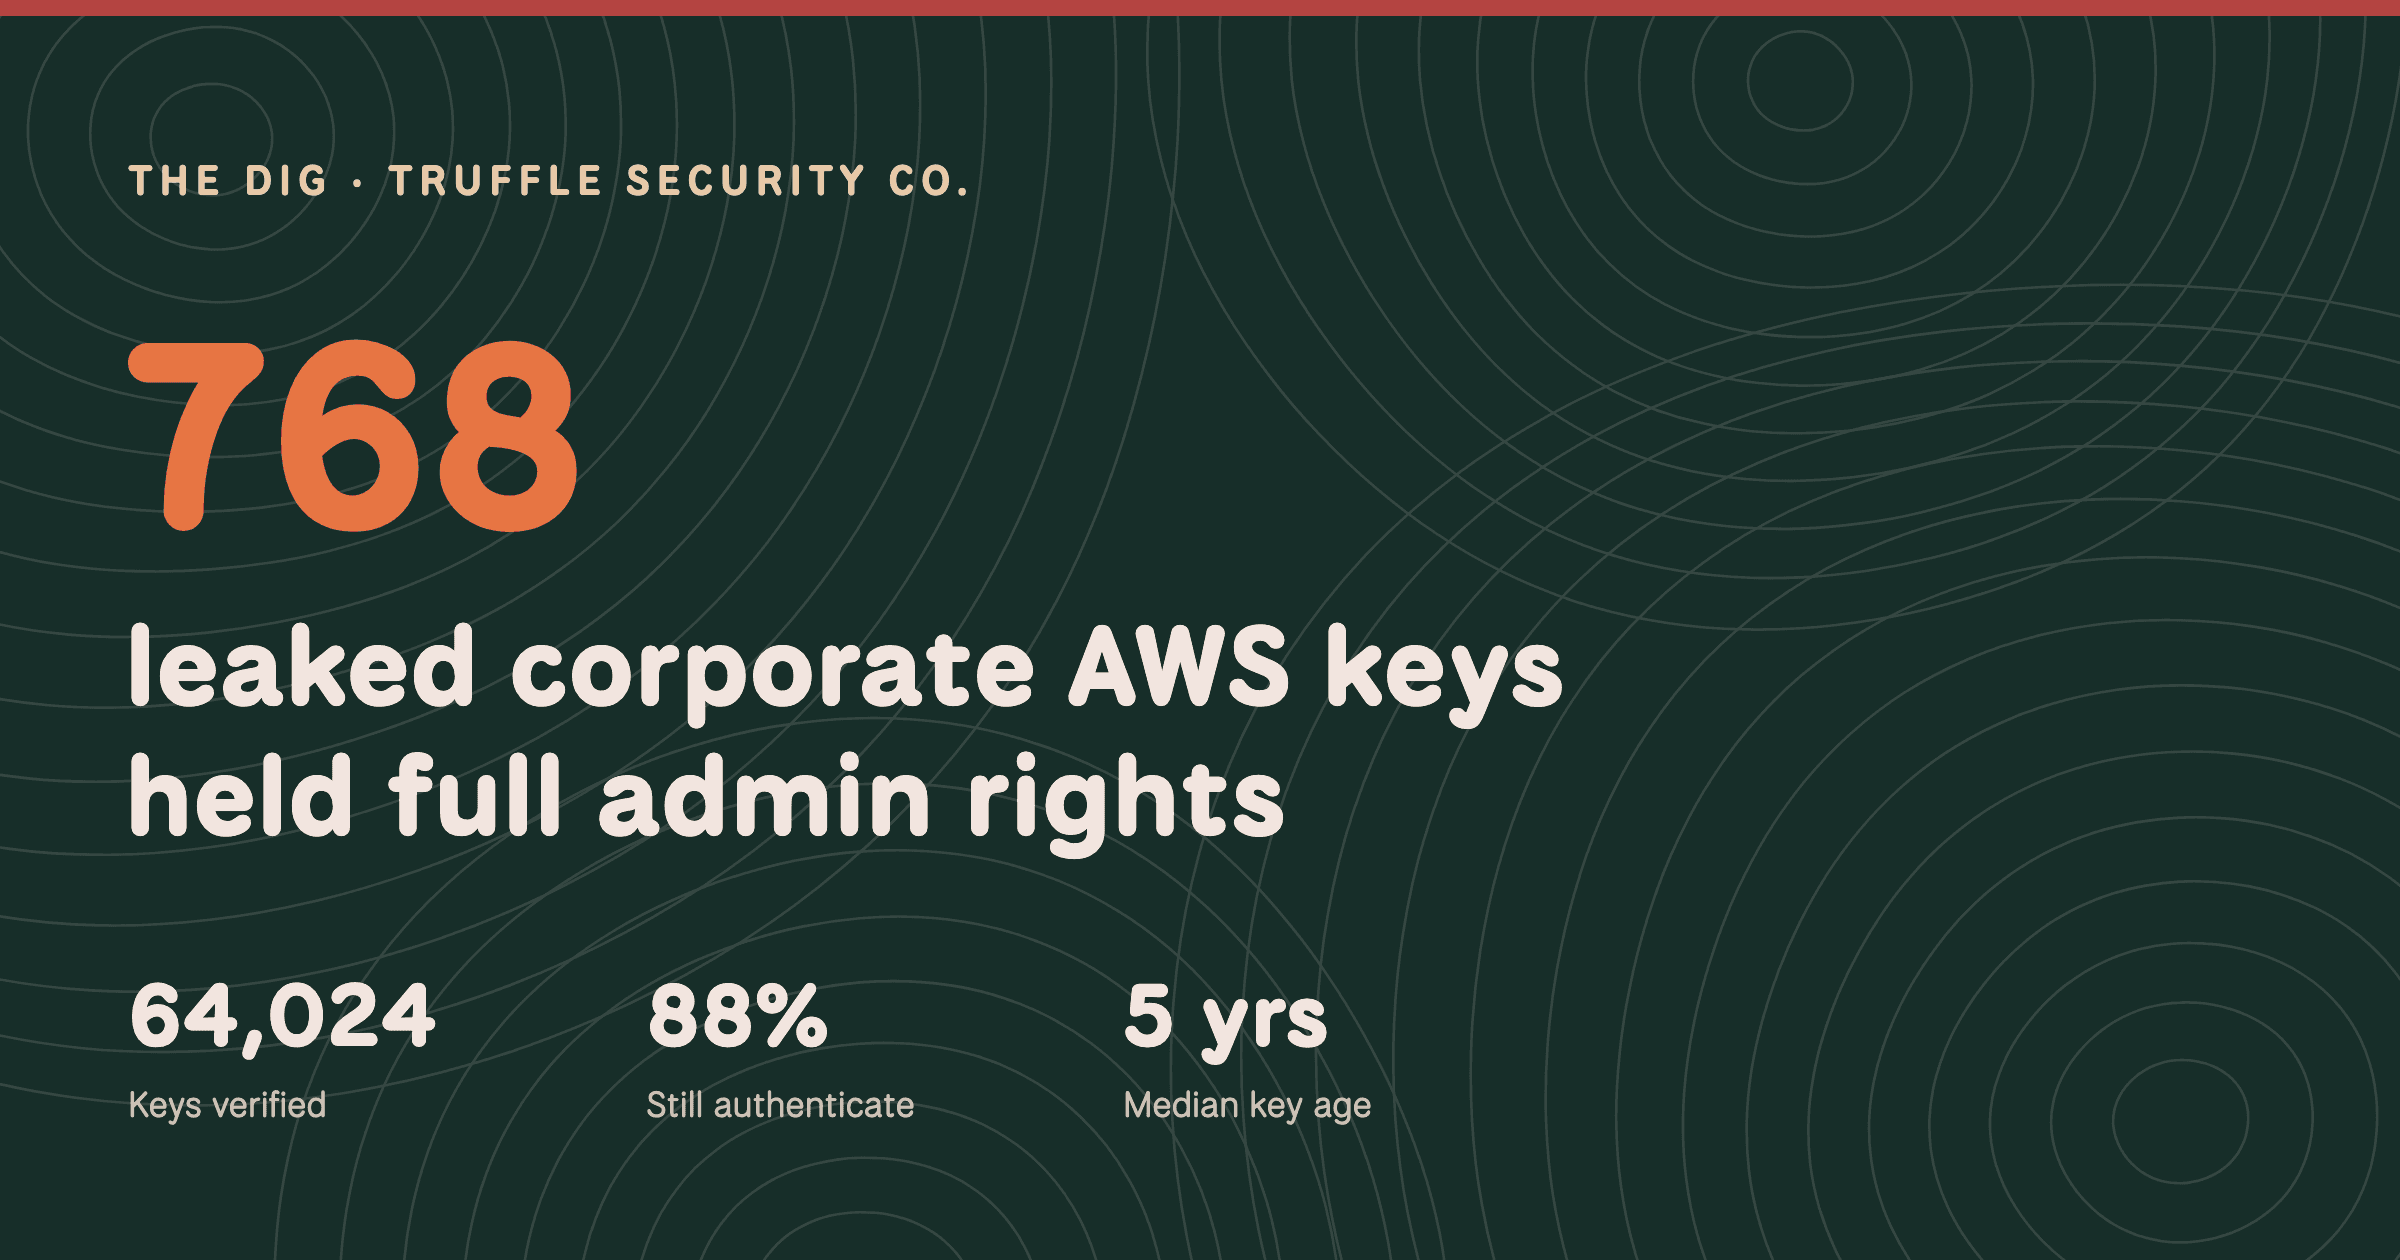
768 Leaked AWS Keys Grant Full Admin Access to Corporate Accounts
Article Content

- •768 AWS keys, including 526 root keys, are still active and grant full admin access.
- •88% of the leaked keys were verified as still authenticating as of August 10, 2026.
- •Most compromised accounts lack budget alerts, increasing the risk of financial abuse.
A recent investigation by Truffle Security revealed that 768 AWS access keys, including 526 root keys, remain active and grant full administrative privileges to corporate accounts. These keys were publicly exposed between August 2022 and August 2026, with 88% still authenticating as of August 10, 2026. The keys were found across various sources, including GitHub repositories and datasets, with Hugging Face being the largest contributor. The potential impact includes unauthorized access to sensitive data, infrastructure abuse, and significant financial charges due to misuse. Only a small fraction of the compromised accounts had budget alerts set up, highlighting a lack of proactive security measures. Truffle Security has notified identifiable owners of the exposed credentials and recommends immediate action to rotate or revoke the compromised keys.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track Truffle Security in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…