 Bastillepost
AI-Generated Anti-China Disinformation Sparks Concerns in Japan
Article Content

- •AI tools are being used to mass-produce anti-China disinformation videos in Japan.
- •Tokyo residents are worried about the potential for misinformation to escalate political tensions.
- •The trend reflects a structural issue in the attention economy, where negative content generates more revenue.
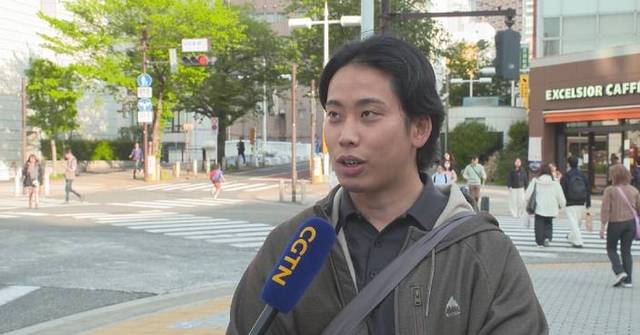
A recent report by Asahi Shimbun revealed that a network in Japan is using artificial intelligence to create and disseminate anti-China disinformation videos. These videos, produced by bloggers and creators on platforms like CrowdWorks, depict fictional scenarios involving Chinese individuals engaging in disruptive behavior. The recruitment for these videos explicitly seeks individuals with an 'antipathy toward China.' Residents in Tokyo have expressed alarm over the potential for such content to escalate political tensions and misinform the public. The phenomenon reflects a broader trend of utilizing AI to manipulate perceptions and generate revenue through sensationalist content. Experts warn that the attention economy incentivizes the creation of negative narratives, which can lead to real-world consequences. The issue is compounded by Japan's political climate, which has seen a rightward shift and increased anti-China sentiment. The current status highlights a growing concern among citizens about the impact of AI on social discourse and international relations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…