 Blog.Talosintelligence
EvilTokens Phishing Kit Exploits Microsoft 365 with AI-Driven BEC Tactics
Article Content

- •EvilTokens allows bypassing MFA to compromise Microsoft 365 accounts.
- •The platform has seen a 1,380% increase in phishing attacks in 2026.
- •ARToken enhances EvilTokens with AI-driven BEC capabilities and targeted lures.
In March 2026, the EvilTokens phishing kit emerged as a significant threat, allowing cybercriminals to bypass multi-factor authentication (MFA) and compromise Microsoft 365 accounts. This Phishing-as-a-Service (PhaaS) platform utilizes Microsoft's OAuth 2.0 Device Authorization Grant to capture victim tokens, enabling Business Email Compromise (BEC) attacks. The platform has rapidly gained traction, with Microsoft reporting hundreds of organizations compromised daily. Cisco Talos identified an affiliate panel named ARToken, which enhances EvilTokens' capabilities by incorporating AI for personalized lures and automated post-compromise actions. The phishing campaigns have increased by 1,380% compared to the previous year, with targeted emails leveraging real vendor relationships to deceive victims. The attack method involves sending emails that appear legitimate but redirect to attacker-controlled Microsoft 365 workspaces. Current assessments indicate that EvilTokens and its affiliates are continuously evolving their tactics, posing a serious threat to organizations using Microsoft 365.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (44)
Following this threat?
Track Icarus, ClickFix and Education in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russia's AI-Driven Cyber Espionage Targets Ukraine and Europe A Russian-linked hacking group, identified as GTG-20006, has utilized Anthropic's Claude AI to automate cyber espionage against over 20 organizations, primarily in Ukraine and Europe. The group targeted Ukrainian government officials, military personnel, and drone manufacturers through sophisticated phishing and…
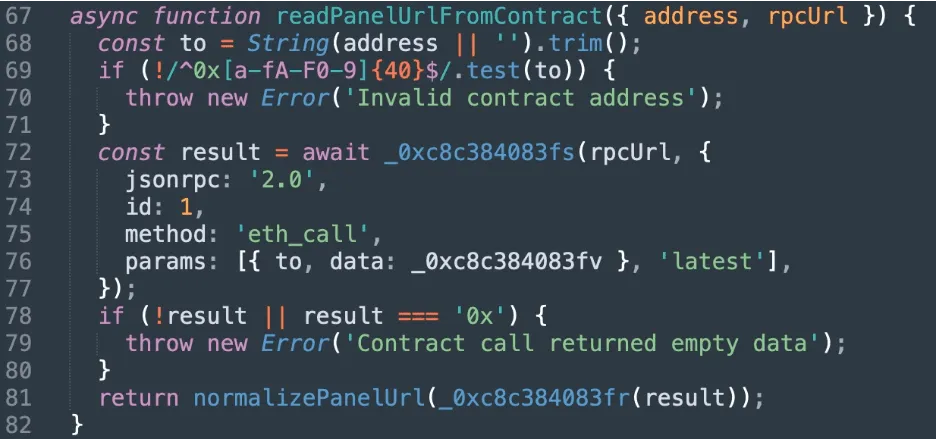 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…