 www.forcepoint.com
AsyncRAT Malware Campaign Exploits Trusted Services for Stealthy Attacks
Article Content

- •AsyncRAT malware leverages TryCloudflare tunnels and Dropbox for stealthy delivery.
- •The campaign targets organizations by exploiting trusted services to evade detection.
- •Security professionals are advised to strengthen defenses against this ongoing threat.
The AsyncRAT malware has resurfaced, utilizing TryCloudflare tunnels and Dropbox links for delivery, which allows it to bypass traditional security measures. This campaign targets various organizations, enabling attackers to maintain control over infected systems, exfiltrate data, and execute commands without detection. The use of these trusted services complicates defensive efforts, as they are rarely blocked by security tools. The current status of the campaign indicates ongoing exploitation, with security professionals urged to enhance their defenses against this sophisticated threat. Specific details on the scale of the impact and the number of affected systems remain unclear.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track AsyncRAT in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 AsyncRAT and SideCopy Campaigns Target Users with Multi-Stage Attacks Recent cybersecurity reports detail two significant malware campaigns involving AsyncRAT and SideCopy. The AsyncRAT campaign employs a five-stage infection chain utilizing a socially engineered batch file and the AutoIt interpreter, culminating in a .NET payload that steals information. Meanwhile, the SideCopy group…
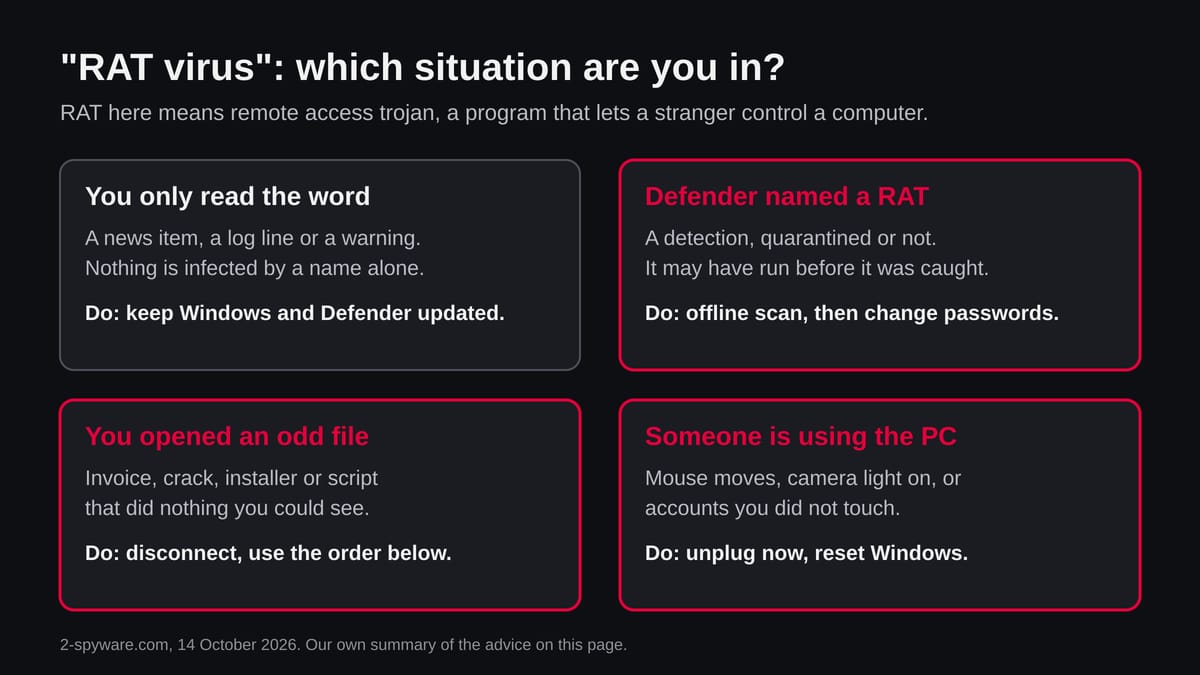 KGB RAT: New Remote Access Trojan Threatens Windows Users The KGB RAT, a Windows Remote Access Trojan, has emerged as a significant threat, offering attackers extensive control over infected systems. Priced as low as $150 per month, it provides features like webcam access, password theft, and psychological harassment tools. First identified in late 2025, KGB RAT is marketed…