 Securityaffairs.Co
AI-Generated PowerShell Script Used for Active Directory Reconnaissance
Article Content

- •An AI-generated PowerShell script was used for Active Directory reconnaissance.
- •The attacker gained access using stolen credentials via Remote Desktop Protocol.
- •The incident was discovered during an investigation by Huntress on June 3, 2026.
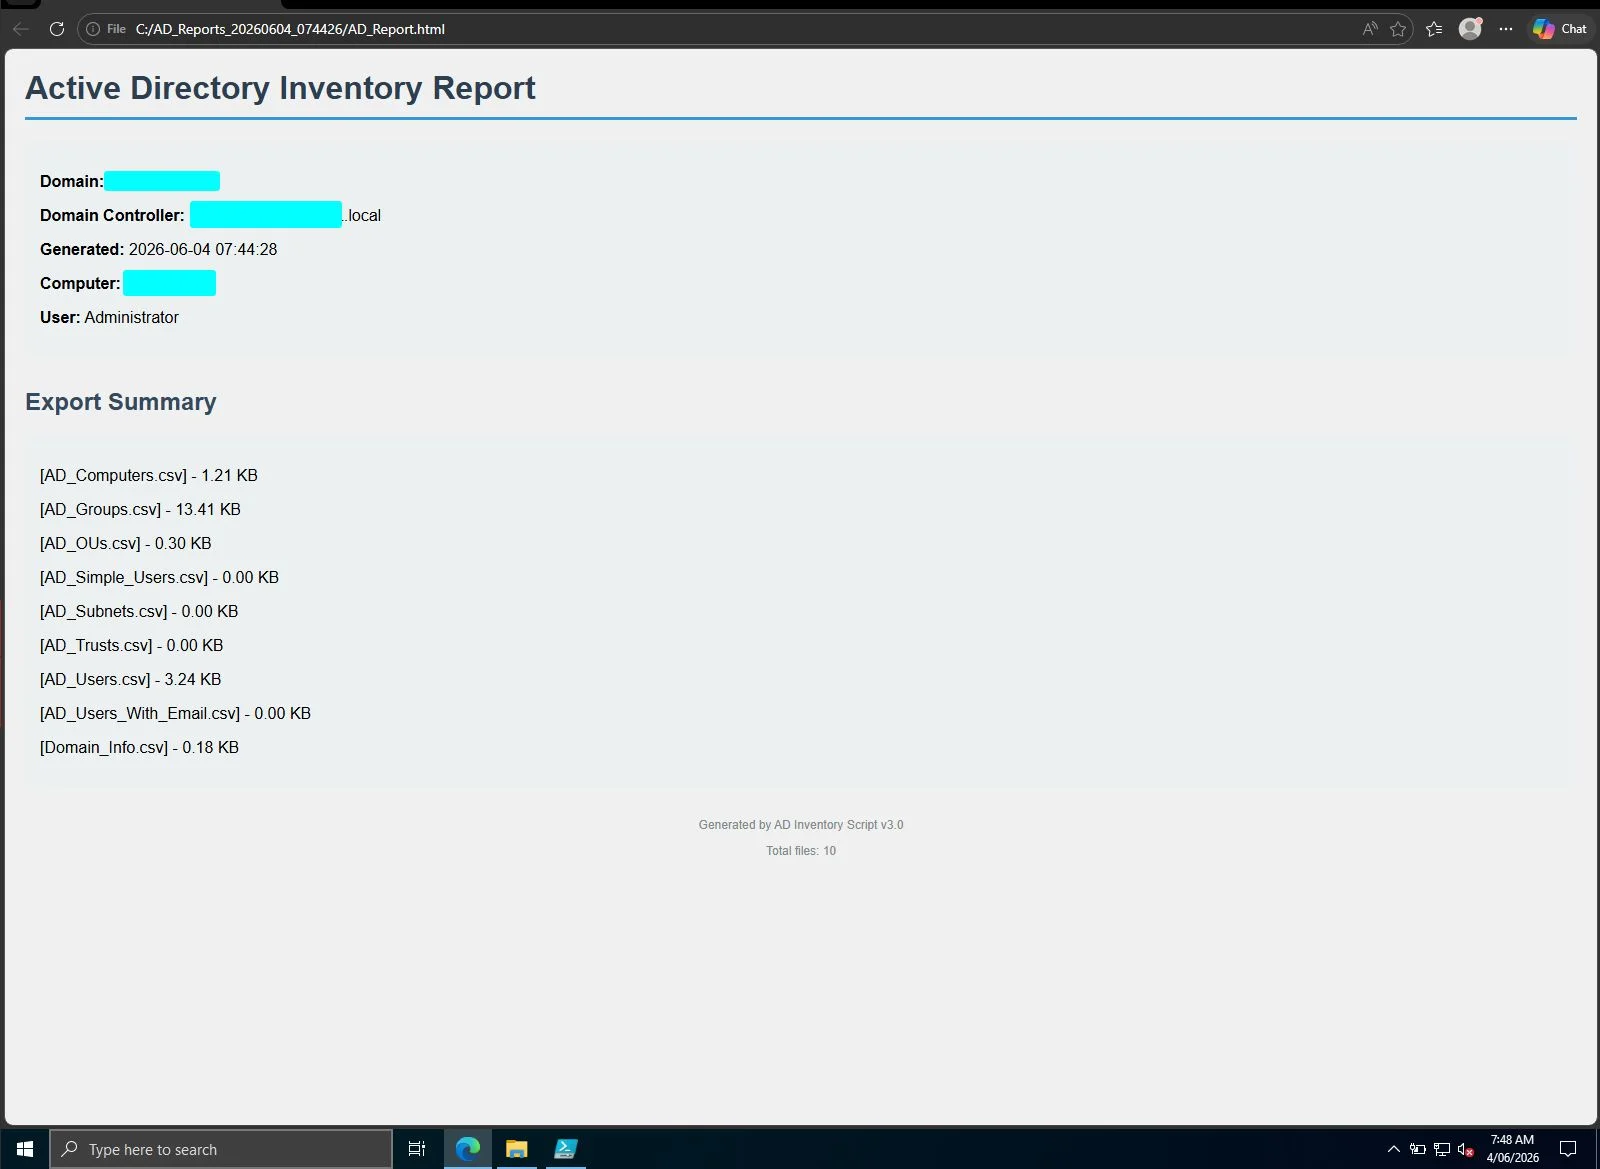
A threat actor employed an AI-generated PowerShell script to conduct reconnaissance in a compromised Active Directory environment. The attack began with unauthorized access to a domain-joined Windows Server via Remote Desktop Protocol using stolen credentials. The intruder staged tools in the ProgramData directory and executed a script to map users, groups, and domain controllers. The incident was identified during an investigation by Huntress on June 3, 2026. This highlights the increasing use of AI in creating custom, evasive malware. The specific impact on the victim organization remains unclear, but the use of AI tools indicates a sophisticated approach to cyber intrusions. The situation is ongoing as security teams respond to the incident.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…