 Vietnam.Vn
Cambodia Freezes $300 Million in Online Fraud Crackdown Amid Rising Cyber Threats
Article Content

- •Cambodia froze over $300 million linked to online fraud networks.
- •SparkRAT malware is being spread through phishing emails disguised as government documents.
- •Despite crackdowns, the online scam industry remains resilient and continues to evolve.
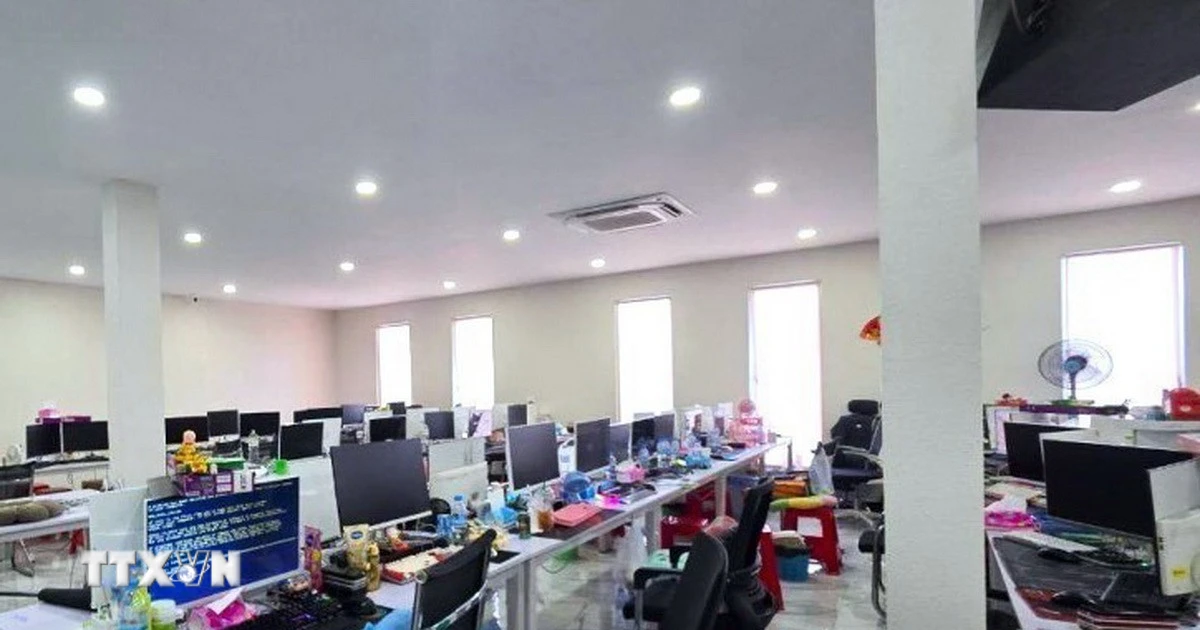
Cambodia has frozen over $300 million in bank accounts linked to online fraud networks as part of a national campaign against technology-based scams. The crackdown, which has referred 446 cases involving 3,927 suspects to the courts, highlights the scale of cybercrime in the country. The Cambodian Special Committee on Combating Online Fraud (CCOS) reported that operations from July 2025 to August 31, 2026, led to the shutdown of 86 large-scale fraud operations. Additionally, the Cambodian Ministry of Interior warned about cybercriminals using forged government documents to distribute SparkRAT malware, which can control infected devices and steal sensitive data. Recent analysis confirmed a hacking campaign targeting organizations in Cambodia, with malicious files disguised as public health notices and real estate documents. The ongoing crackdown has not fully dismantled the underlying networks, as recruitment and construction related to scams continue in various regions. The situation reflects a significant transformation of local economies and social structures due to the pervasive influence of the online scam industry.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track SparkRAT in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 AI-Discovered Vulnerabilities Surge, Increasing RCE Threats Google's Threat Intelligence Group (GTIG) reports that software vulnerability disclosures doubled from 5,045 in January 2026 to 10,740 in August 2026, largely influenced by AI-assisted discovery. Notably, 50% of AI-discovered vulnerabilities enable remote code execution (RCE), compared to 26% of non-AI…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…