 Securityaffairs.Co
Chinese Hackers Weaponize AI Tools in Cyber Espionage Campaign
Article Content

- •Chinese hackers are using AI tools Claude Code and DeepSeek in cyber espionage.
- •The campaign targets Taiwanese government and financial sectors.
- •TencShell C2 infrastructure is linked to the ongoing attacks.
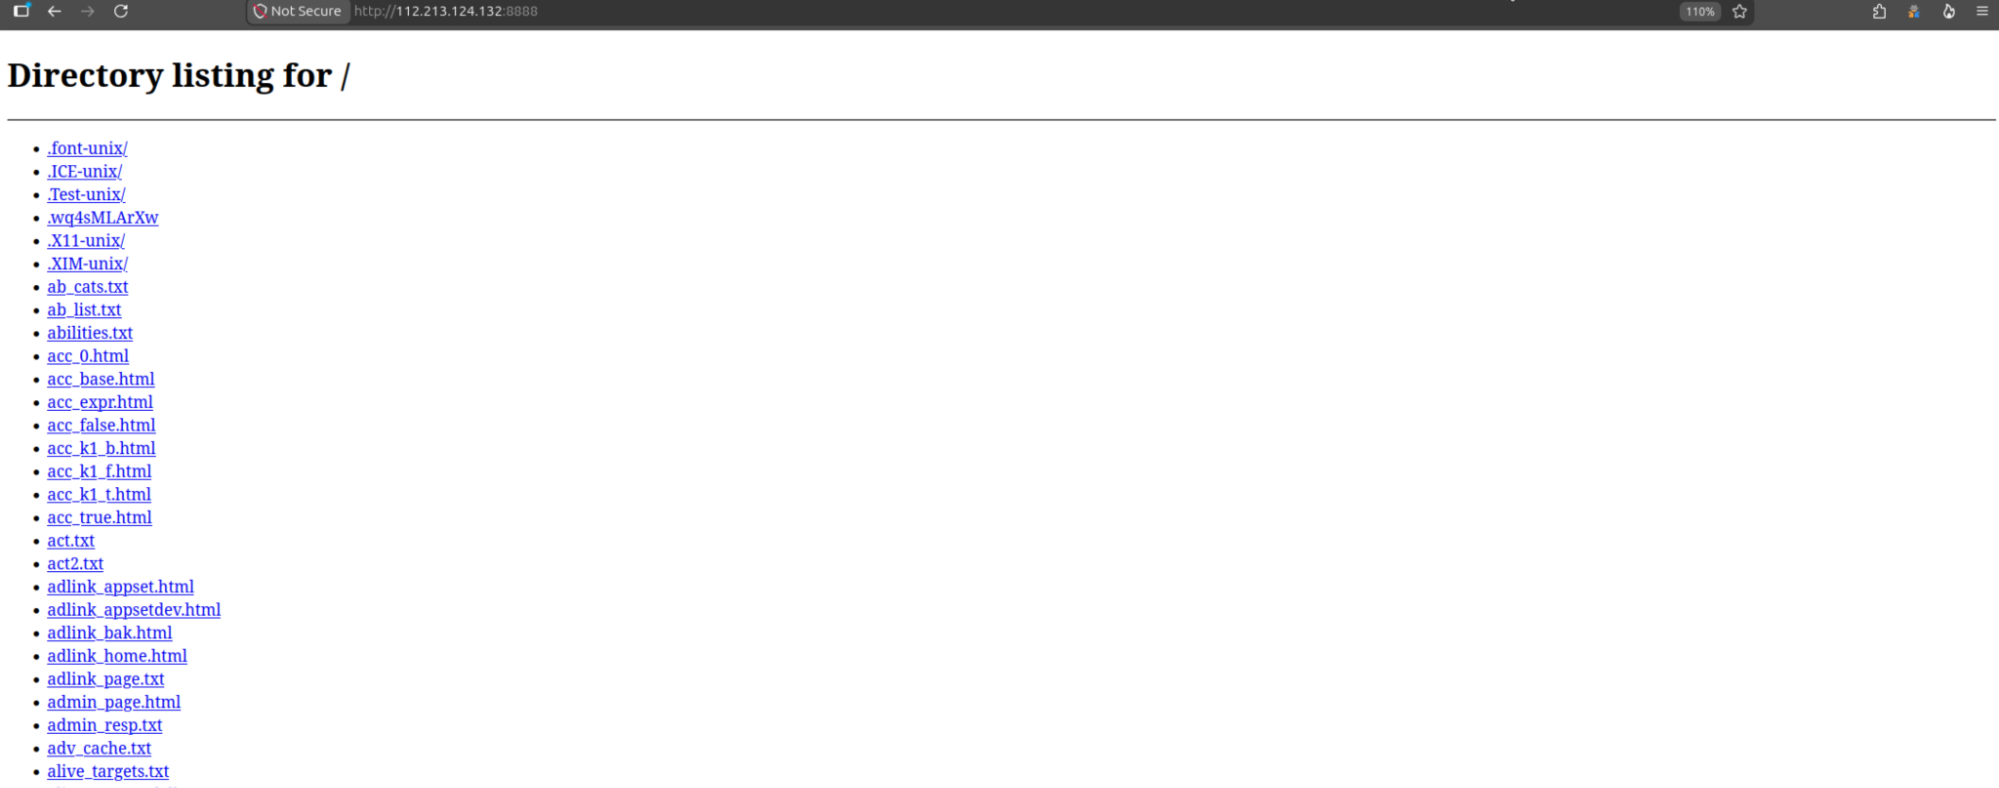
Chinese-linked threat actors have integrated Anthropic's Claude Code and DeepSeek-v4-pro into a cyber espionage campaign targeting government entities and financial organizations in Taiwan. The operation utilizes TencShell command-and-control infrastructure, which was previously documented by Cato CTRL in May 2026. Researchers from Hunt have confirmed that these AI tools are embedded within the core execution flows of the attacks, indicating a sophisticated level of integration. The campaign is currently active, posing significant risks to the targeted sectors. The specific vulnerabilities exploited and the number of affected organizations remain unspecified, but the implications for national security and economic stability are considerable.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track TencShell in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…