 Oodaloop
ConsentFix and ClickFix: Rapid Hijacking of Microsoft 365 Accounts
Article Content

- •ConsentFix and ClickFix attacks can hijack Microsoft 365 accounts in seconds.
- •Attackers exploit user habits by inserting fake prompts into normal workflows.
- •The techniques have evolved, requiring minimal technical skill to execute.
Cybercriminals are exploiting two attack methods, ConsentFix and ClickFix, to hijack Microsoft 365 accounts in as little as three seconds. These attacks leverage users' habitual online behaviors, such as dragging links into browsers and completing OAuth consent flows without scrutiny. The ClickFix method involves fake prompts that execute attacker commands through keyboard shortcuts, while ConsentFix targets OAuth consent screens, tricking users into surrendering OAuth tokens. Victims unknowingly grant session access to their accounts without entering credentials. The attacks have surged since 2025, with attackers utilizing free services for phishing lures and profiling targets before launching their attacks. Awareness and training remain critical, as these techniques exploit familiar workflows.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
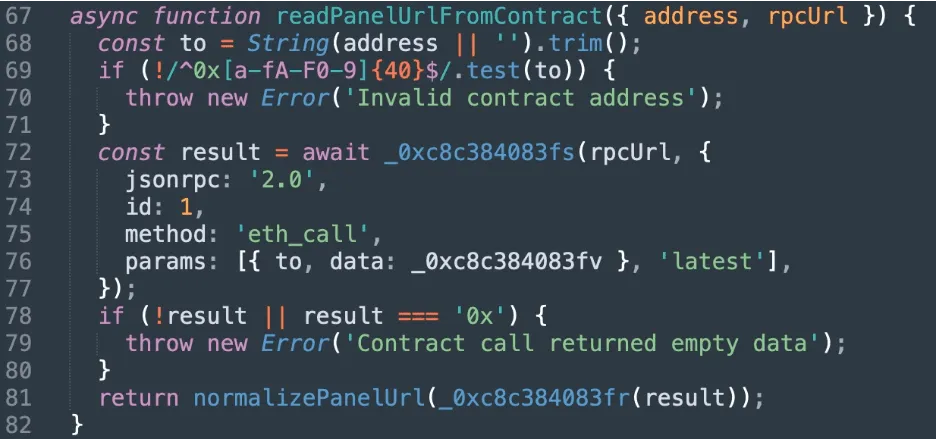 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…