 Infosecurity-Magazine
Cyber Incident Disrupts Services at UT San Antonio Ahead of New Term
Article Content

- •UTSA detected unauthorized activity and took systems offline to prevent a breach.
- •No data was confirmed to be accessed or stolen during the incident.
- •Disruptions affected student registration and tuition payments ahead of classes.
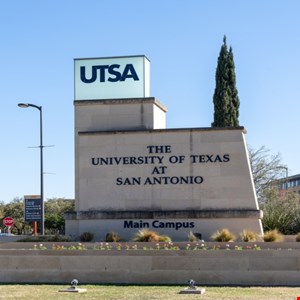
The University of Texas at San Antonio (UTSA) experienced a cyber incident that led to the shutdown of several IT systems just days before the start of the academic term on August 19, 2026. Unauthorized activity was detected over the weekend, prompting immediate action to take systems offline and prevent any potential breach of core systems. UTSA confirmed that no data was accessed or stolen during the incident. The university acknowledged the disruption to student services, including online registration and tuition payments, and has granted extensions for these processes. Phone systems were also affected but were expected to be restored shortly. The university is working with expert partners to evaluate its systems and enhance security measures. Educational institutions have increasingly become targets for cyberattacks during peak registration periods, making this incident particularly concerning.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Following this threat?
Track The University Of Texas At San Antonio in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…