 Whdh
Cybersecurity Incident Disrupts Operations at Brockton Hospital
Article Content

- •Brockton Hospital reverted to paper records due to a cybersecurity incident detected on April 6.
- •Ambulance services were diverted, and outpatient chemotherapy treatments were canceled.
- •Signature Healthcare is working with cybersecurity experts and law enforcement to investigate the breach.
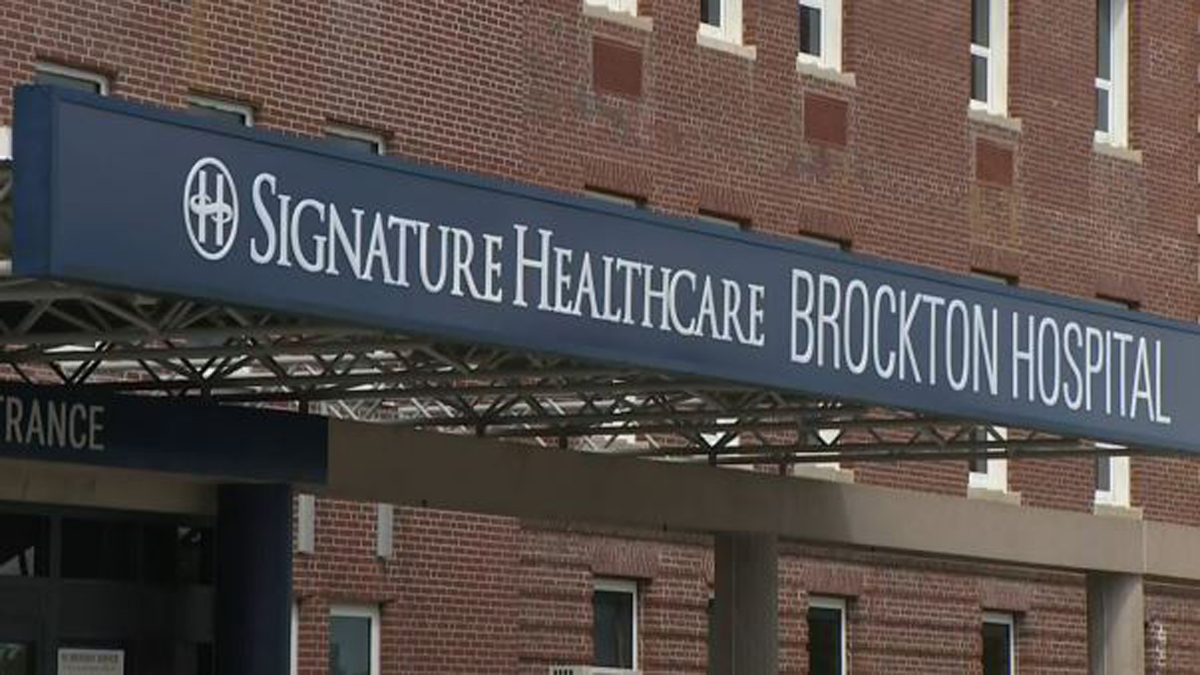
On April 6, 2026, Brockton Hospital experienced a cybersecurity incident that forced the facility to shut down key computer systems. This incident was triggered by suspicious activity detected within the hospital's network, leading to the activation of incident response protocols. As a result, the hospital reverted to paper records and manual documentation methods, affecting outpatient visits and pharmacy services. Ambulances were diverted to other facilities, although inpatient and emergency services remained operational. Chemotherapy treatments were canceled, and retail pharmacies were closed. Signature Healthcare, the hospital's operator, is collaborating with cybersecurity experts and law enforcement to investigate the breach. The nature of the attack, including whether it involved ransomware, has not been confirmed, and there is currently no timeline for restoring full services. The incident highlights the increasing frequency of cyberattacks targeting healthcare facilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (12)
Following this threat?
Track Brockton Hospital in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…