 Pakistantoday.Pk
Drama Bhanwar Highlights AI Deepfake Threats in Journalism
Article Content

- •The drama 'Bhanwar' showcases the risks of AI deepfakes in journalism.
- •Adeel Azam, the protagonist, faces a fabricated apology video created using AI.
- •The storyline reflects growing concerns over AI regulation and digital rights in Pakistan.
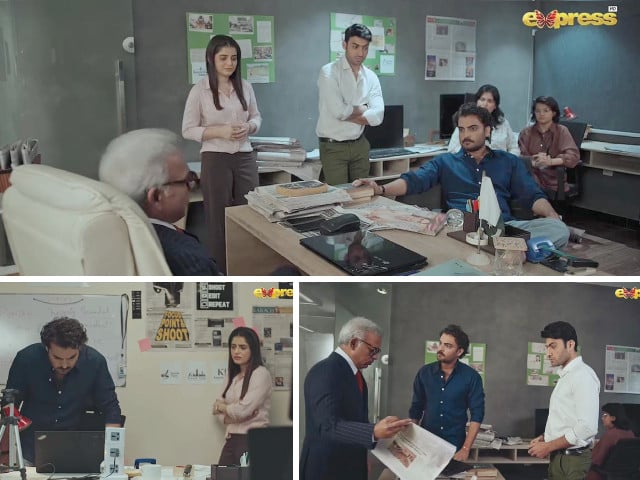
The Pakistani drama 'Bhanwar' portrays the dangers of AI-generated deepfake videos, focusing on a journalist named Adeel Azam who faces character assassination through a fabricated apology video. The show illustrates how AI can distort reality, damage reputations, and suppress dissent, reflecting broader concerns about misinformation in Pakistan. Adeel's media organization initially resists publishing his investigative report on a pharmaceutical company due to internal pressures. After he refuses to issue a public apology, an AI-generated video falsely shows him apologizing. This incident raises significant ethical questions about the misuse of AI in media and the potential for organizations to exploit such technology against employees. The narrative also aligns with ongoing discussions in Pakistan regarding AI regulation and digital likeness protections, highlighted by the proposed Punjab Performers' Digital Identity and Artificial Intelligence Protection Act 2026.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…