 Theregister
Fake Codex Installer Delivers Suspected AMOS Infostealer via Google Sites
Article Content

- •Fake Codex download pages are used to deliver malware to macOS users.
- •The attack employs ClickFix techniques to obfuscate malicious content within trusted domains.
- •The final payload is suspected to be the Atomic macOS Stealer (AMOS), targeting both Intel and Apple Silicon Macs.
A malicious campaign has emerged, using fake Codex installation pages to deliver malware targeting macOS users. The attackers utilize Google Sites to host a fraudulent download portal that appears legitimate, tricking users into executing a command that initiates a multi-stage malware infection. The command, disguised as a legitimate installation process, retrieves a shell script that ultimately downloads a Mach-O binary suspected to be the Atomic macOS Stealer (AMOS). Cato Networks identified multiple infrastructure sets and obfuscation techniques used in this campaign, including path-aware content serving to evade detection. The malware is designed to run on both Intel and Apple Silicon Macs, with significant similarities to known AMOS campaigns. The campaign is ongoing, with researchers advising caution to users searching for AI coding tools.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
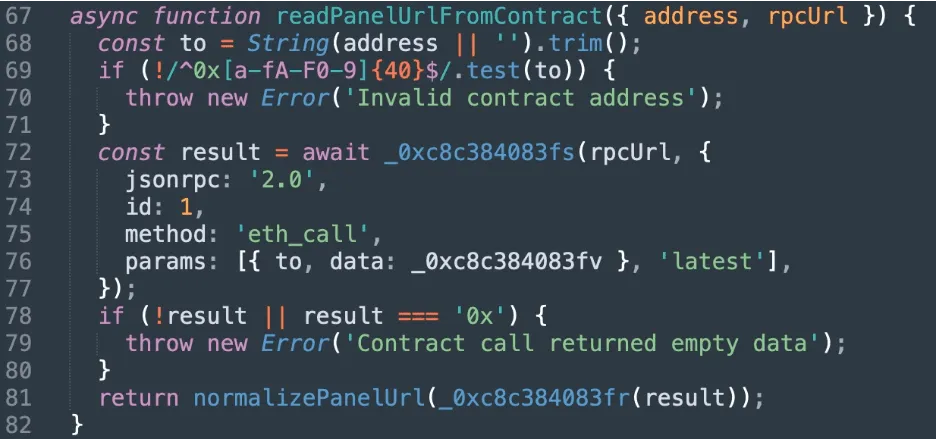 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…