 Scworld
Gentlemen Ransomware Targets Global Industries Amid LLM Integration
Article Content
Browse articles 
The Gentlemen ransomware operation has affected at least 17 countries across the Americas, Asia-Pacific, and the Middle East, targeting sectors such as manufacturing, healthcare, construction, and insurance. This operation employs a double extortion model and utilizes various evasion techniques, including the deactivation of Windows Defender. Concurrently, the integration of Large Language Models into ransomware operations is facilitating the creation of Ransomware-as-a-Service, lowering entry barriers for cybercriminals.
Ask AI about this cluster
Answers cite the sources they use
Updated 227d ago How this analysis works
More articles in this cluster (26)
Following this threat?
Track Gentlemen and CVE-2025-55182 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical RCE Vulnerability in Meta React Server Components Discovered CVE-2025-55182 is a critical remote code execution vulnerability in Meta React Server Components, with a CVSS score of 10.0. It allows unauthenticated attackers to execute arbitrary commands on the server by sending crafted JSON payloads. This vulnerability was added to CISA's Known Exploited Vulnerabilities catalog…
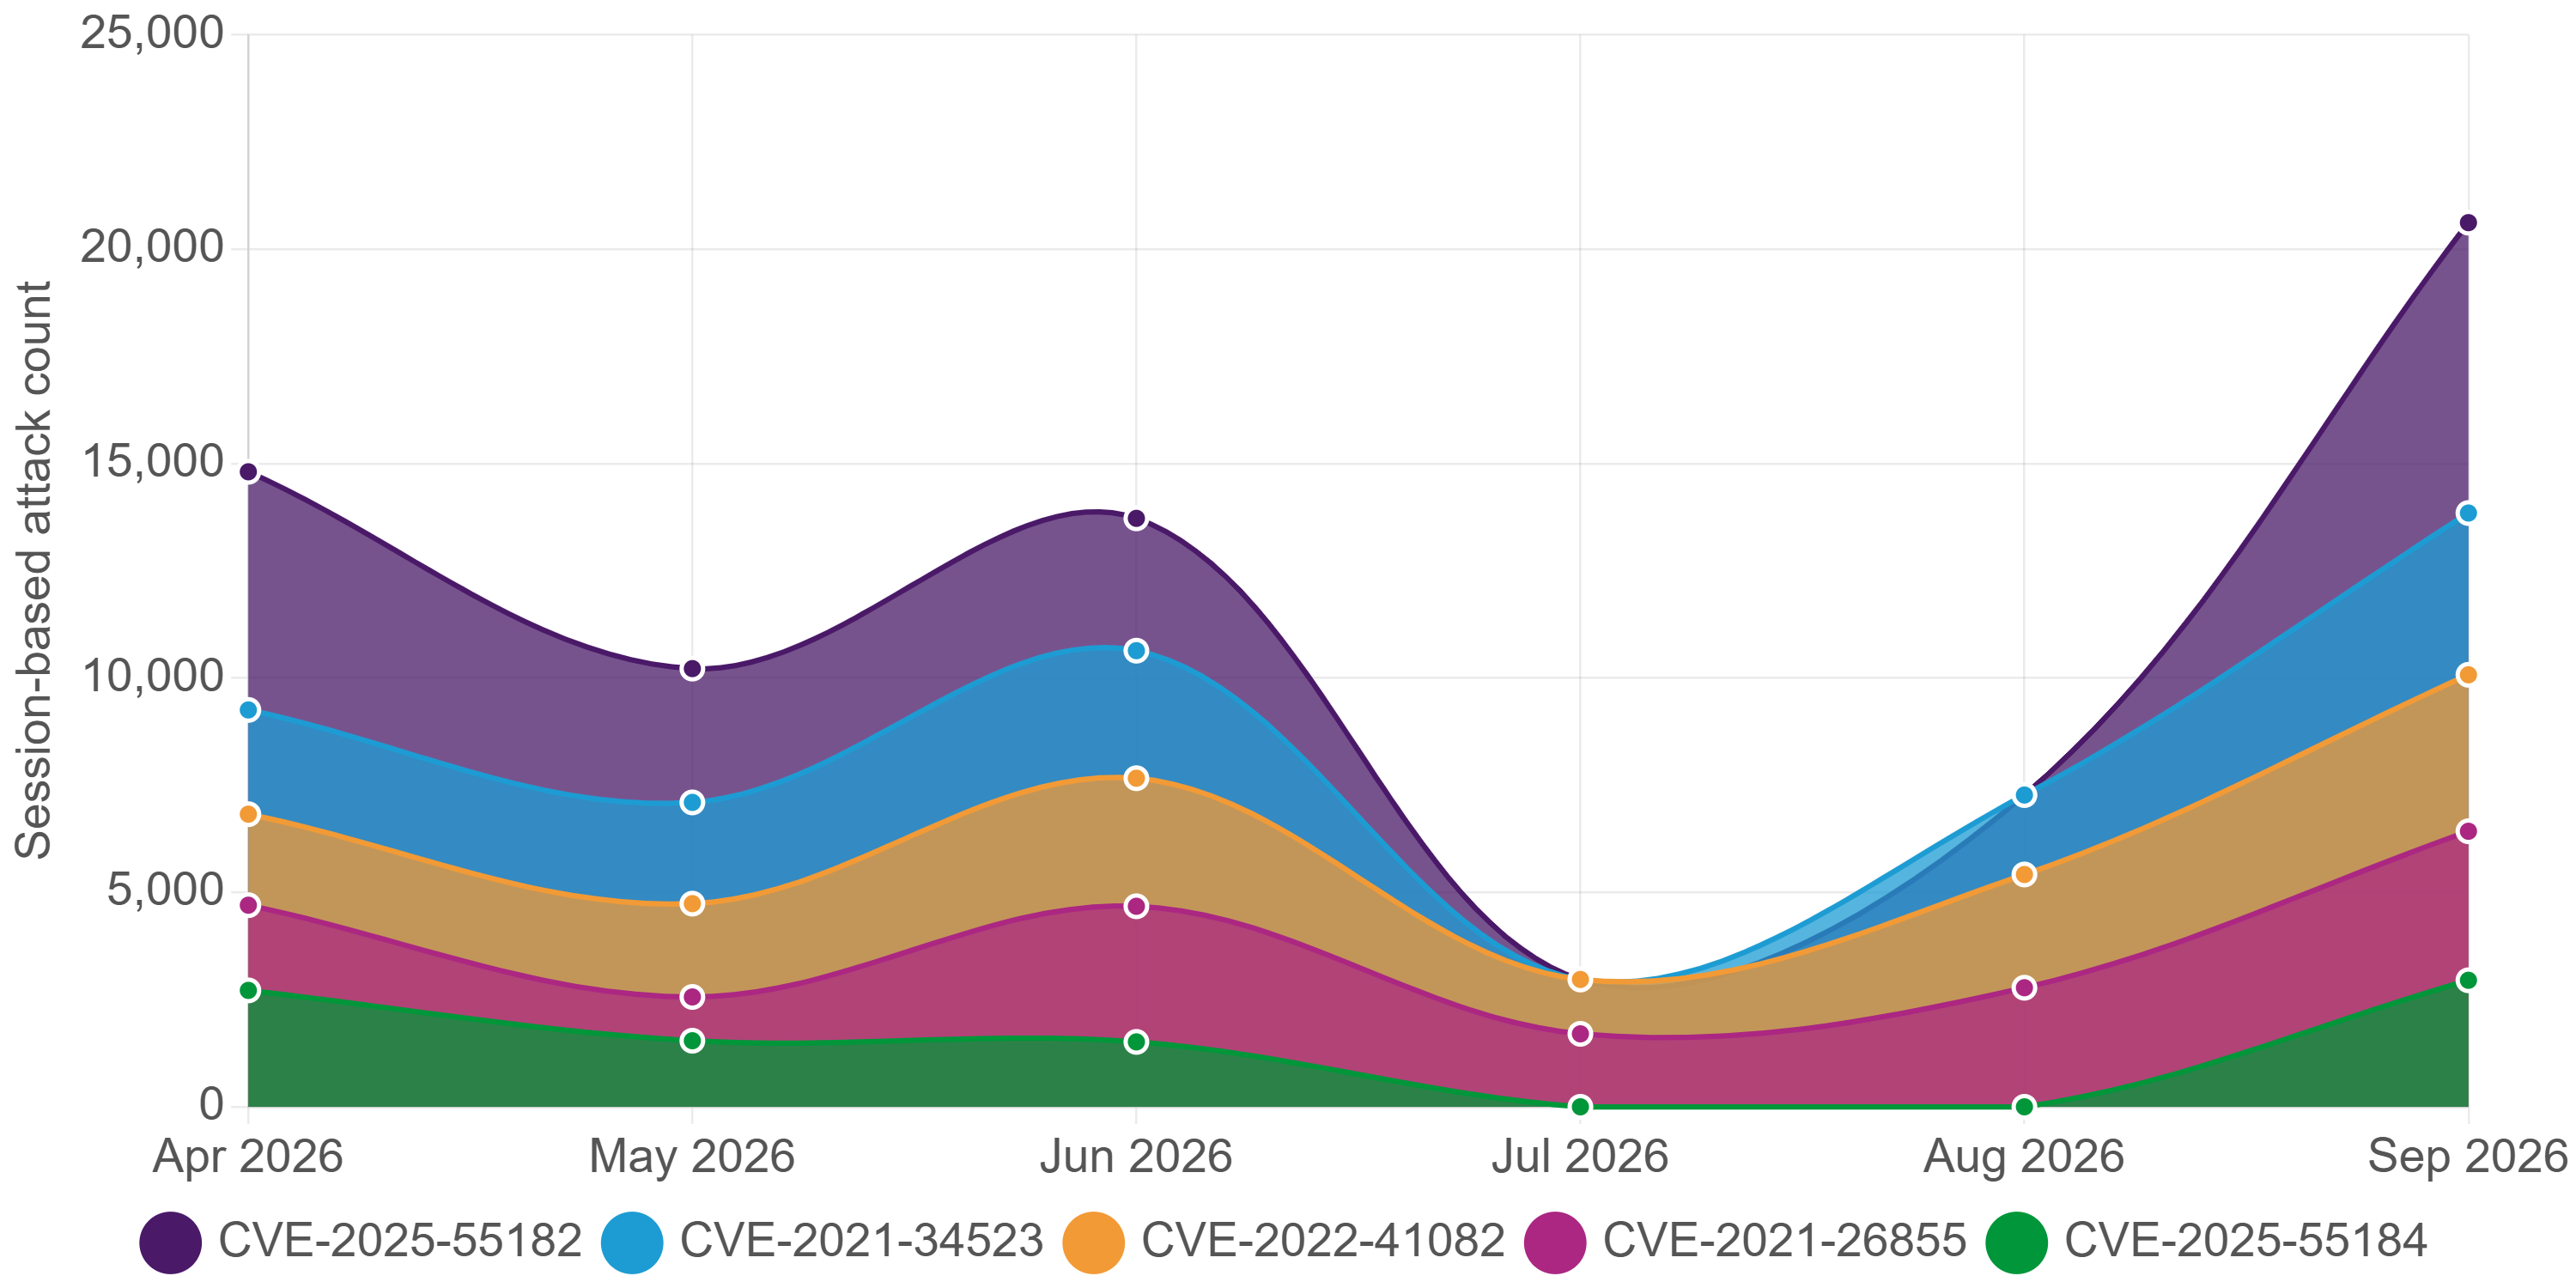 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…