 Indiagazette
India's Government Targets Username Impersonation to Combat Cyber Fraud
Article Content

- •The Indian government is addressing username-related impersonation risks with Meta.
- •Current username claims are on a first-come, first-served basis, increasing fraud risks.
- •Cybersecurity is evolving to include mobile threats, necessitating enhanced security measures.
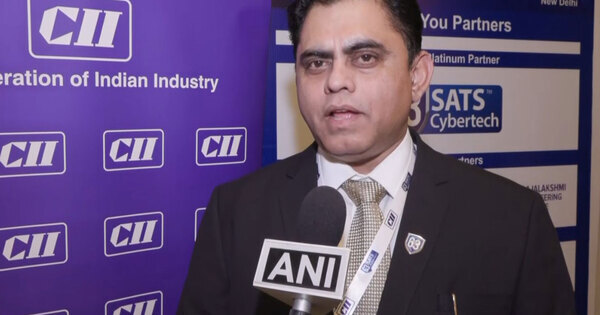
The Indian government has issued a notice to Meta regarding username-related risks that could facilitate cyber fraud and impersonation. Neehar Pathare, CEO of 63SATS Cybertech, emphasized that the current first-come, first-served username system allows impersonators to claim high-profile usernames easily. This poses a significant risk as threat actors could exploit these usernames for financial gain or fraudulent activities. The notice comes amid discussions at the Cyber 360 Degrees Summit about protecting critical infrastructure from evolving cyber threats, particularly those enhanced by artificial intelligence. Pathare noted that cybersecurity must be recognized as a balance sheet issue, not just an IT concern. He also highlighted the increasing shift of cyber threats towards mobile devices, stressing the need for improved mobile security solutions. The situation is still developing, with stakeholders awaiting further government actions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Meta in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…