 Batimes.Ar
Growing Threat of Foreign Information Manipulation and Interference Highlighted at Conference
Article Content

- •The conference addressed the threat of Foreign Information Manipulation and Interference (FIMI).
- •Experts highlighted the use of disinformation as part of hybrid warfare strategies.
- •Concerns were raised about a potential Russian-linked influence operation targeting Argentine media.
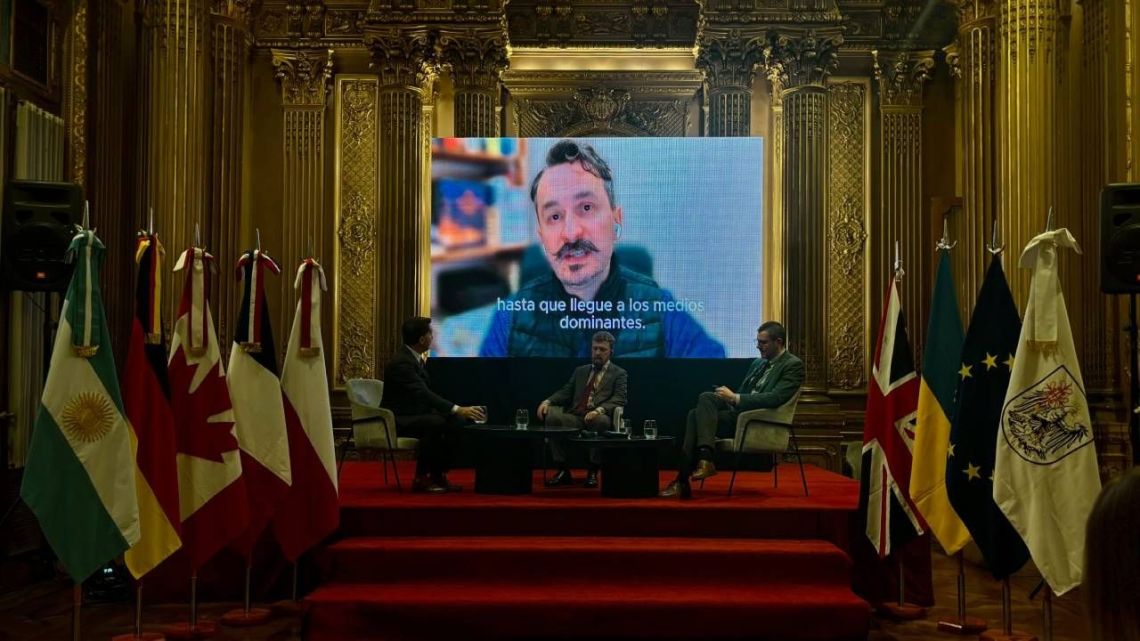
On April 17, 2026, a conference in Buenos Aires focused on the rising threat of Foreign Information Manipulation and Interference (FIMI) orchestrated by foreign actors. Experts discussed how disinformation is part of hybrid warfare strategies that combine cyber operations and political influence to manipulate public discourse. The event was organized by Western-aligned diplomatic missions, including the EU and several European countries. Key discussions included tactics such as the use of proxy media outlets and coordinated social media amplification. The conference featured prominent speakers, including EU Ambassador Erik Høeg and German Ambassador Dieter Lamlé, who emphasized the need for democracies to defend their values against disinformation. The event also addressed a potential Russian-linked effort to influence Argentine media, with a reported budget of approximately $283,000. The conference aimed to enhance awareness and resilience against these tactics in Latin America's fragmented media landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…