 Techafricanews
Guinea Joins Medusa Africa Submarine Cable Project for Enhanced Connectivity
Article Content

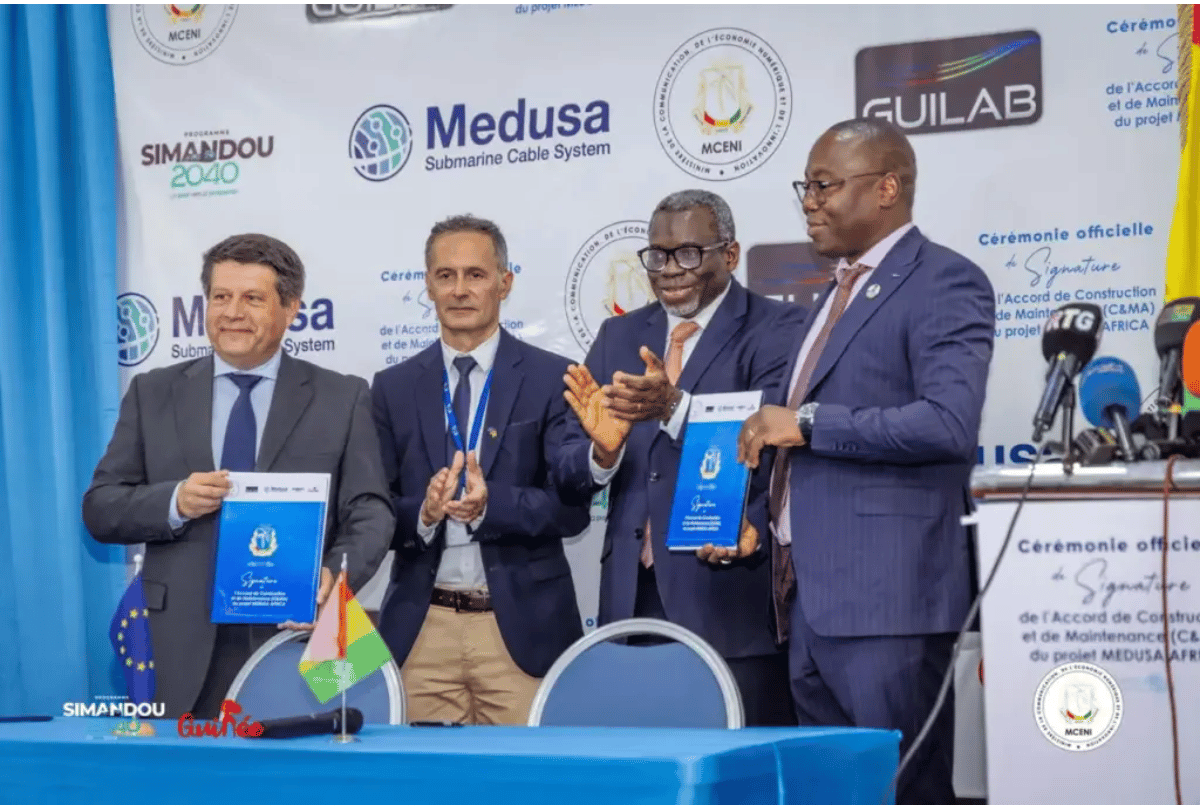
- •Guinea signed a C&MA for the Medusa Africa submarine cable on May 11, 2026.
- •The project aims to enhance digital infrastructure and reduce reliance on single connectivity routes.
- •The Medusa cable will connect multiple regions, improving internet capacity and stability.
On May 11, 2026, Guinea signed a Construction and Maintenance Agreement (C&MA) for the Medusa Africa submarine cable, marking its second international subsea link. This agreement, signed by Prime Minister Amadou Oury Bah and GUILAB's CEO Ahmed Karifa Diawara, aims to enhance Guinea's digital infrastructure and reduce reliance on a single cable. The Medusa cable will connect Europe, North Africa, West Africa, and the Middle East, improving internet capacity and stability. The project is part of Guinea's vision to become a digital hub in West Africa, ensuring better connectivity for citizens and businesses. The agreement also initiates marine surveys and operational preparations for the cable's landing in Conakry. This strategic investment is expected to bolster the national economy and cybersecurity efforts. The project aligns with the Simandou 2040 vision, emphasizing the importance of critical digital infrastructure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…