 Scworld
High-Severity Vulnerability in Open WebUI Exposes Users to Account Takeover
Article Content
Browse articles 
A high-severity security vulnerability, tracked as CVE-2025-64496, has been identified in Open WebUI, affecting versions 0.6.34 and older when the Direct Connections feature is enabled. Discovered by Cato Networks researchers, the flaw allows for account takeover and, under certain conditions, remote code execution on backend servers due to unsafe handling of server-sent events.
Ask AI about this cluster
Answers cite the sources they use
Updated 218d ago How this analysis works
More articles in this cluster (4)
Following this threat?
Track CVE-2025-55182 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
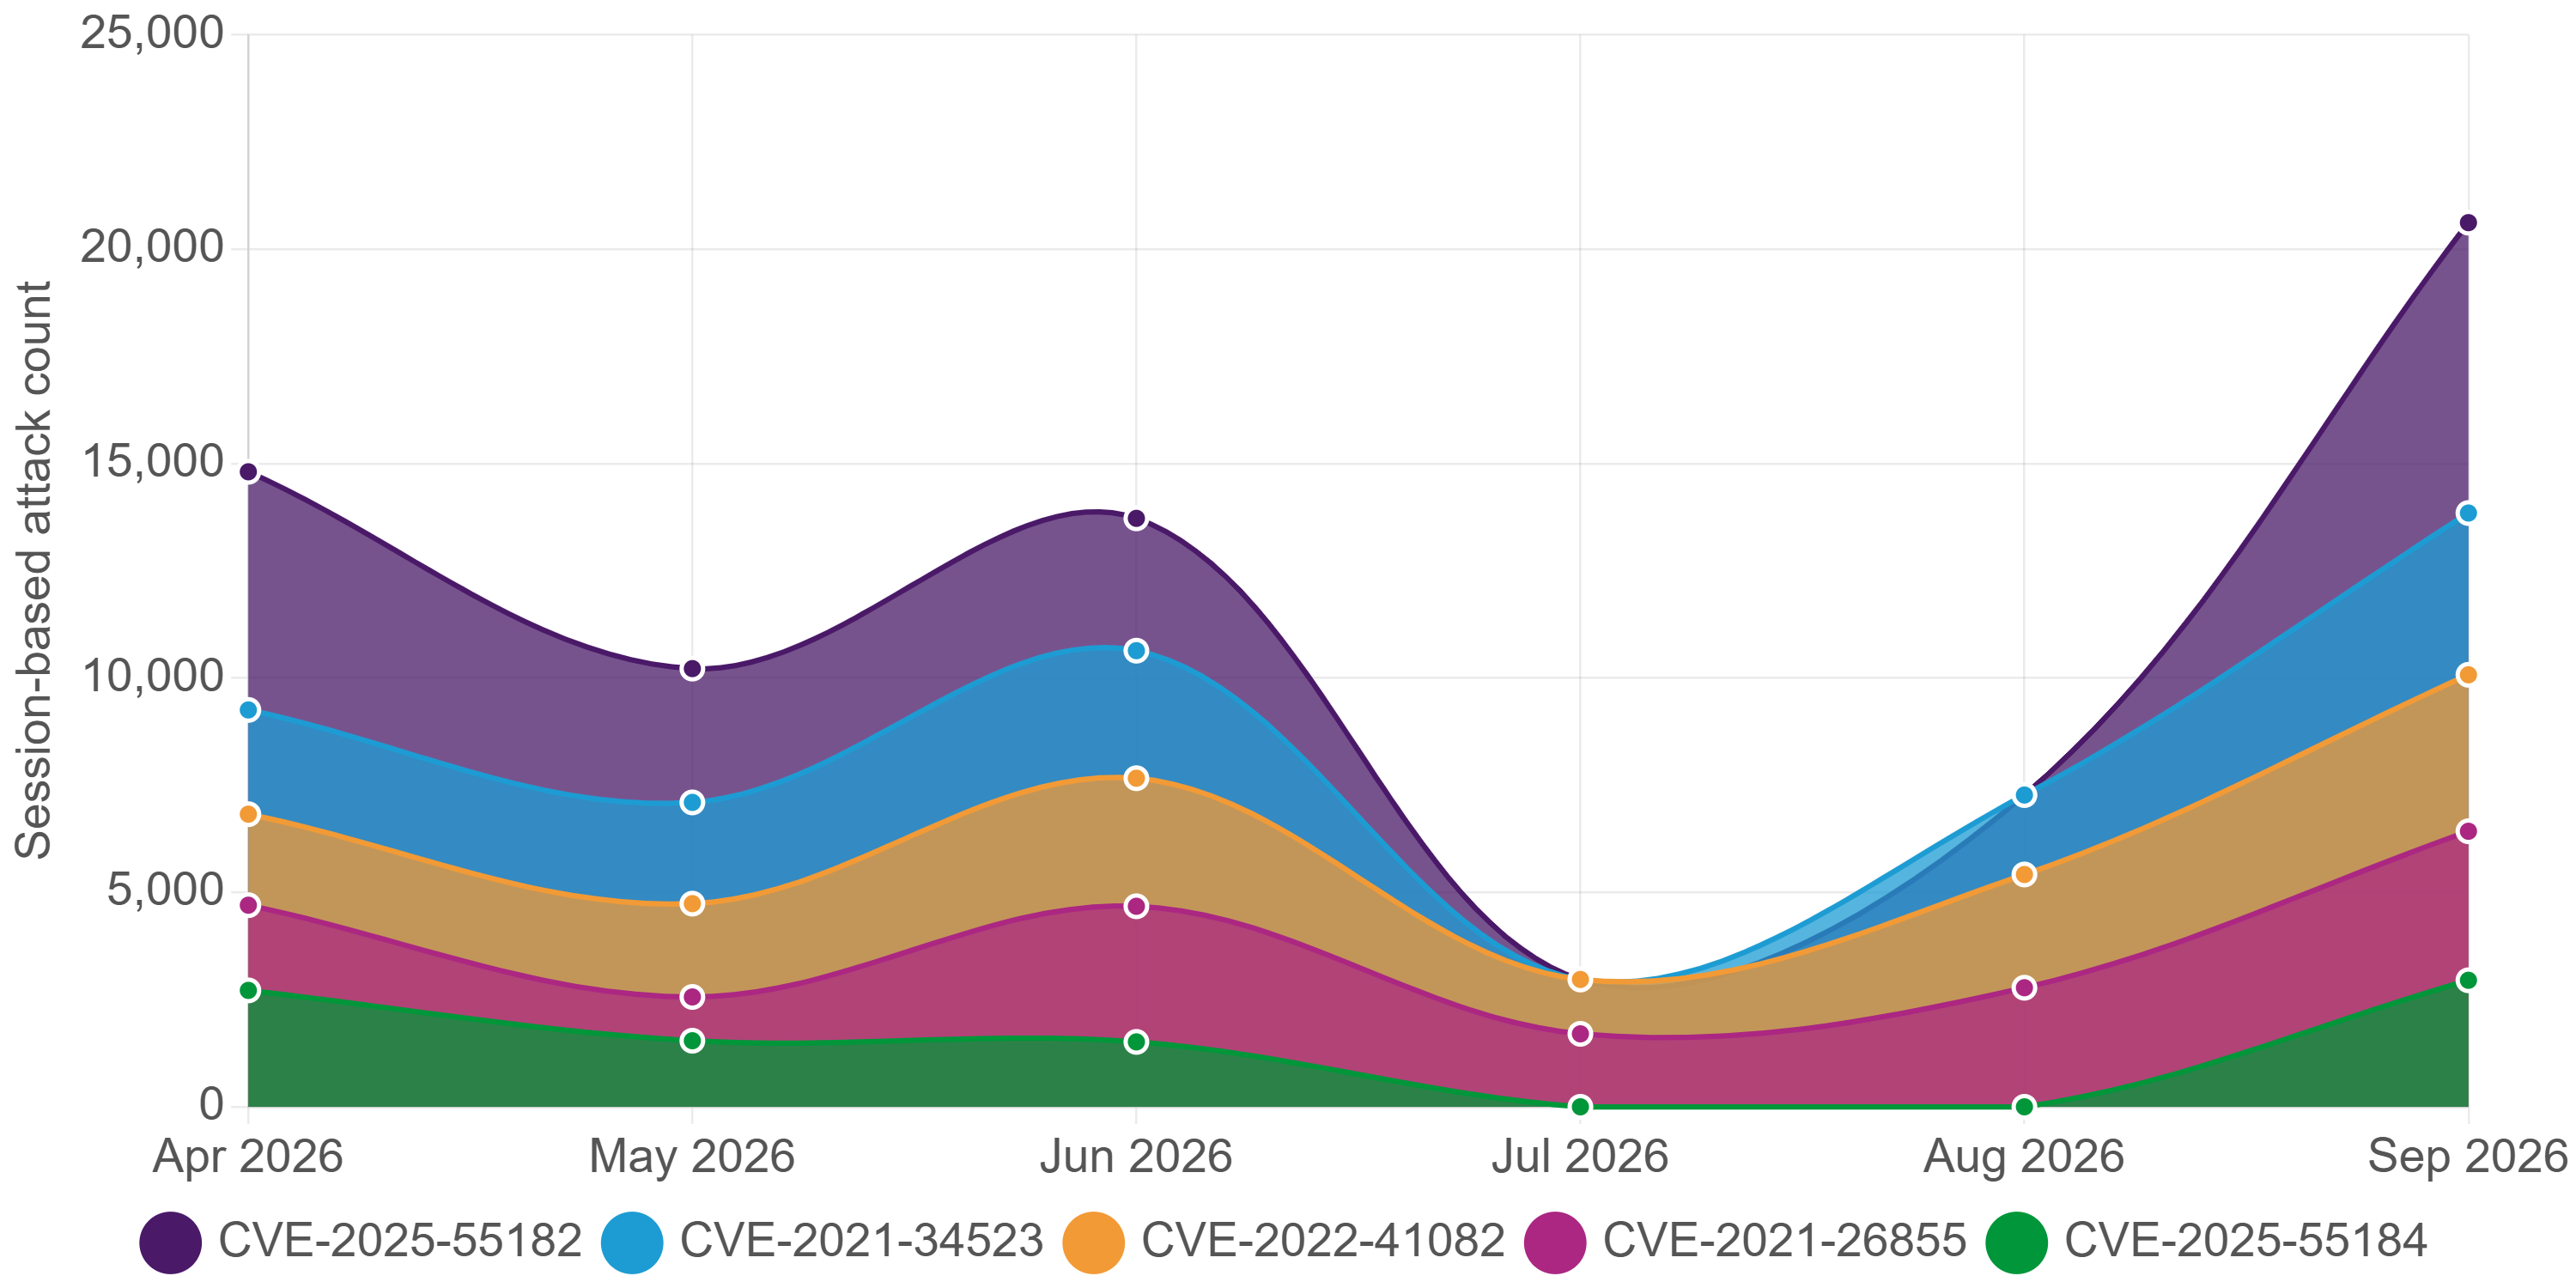 Langflow AI Platform Targeted by RCE Exploitation In September 2026, the Langflow AI application-building platform faced significant exploitation attempts targeting CVE-2026-0768, an unauthenticated remote code execution vulnerability. F5 Labs reported 405 requests from 55 distinct source IPs, indicating a coordinated effort to exploit this flaw. The vulnerability…
 Wiz Launches AI-Accelerated Security for FedRAMP High Environments Wiz has introduced AI Agents within its FedRAMP High authorized environment, Wiz for U.S. Government, to enhance security in public sector organizations managing sensitive data. The AI Agents provide machine-speed risk remediation and actionable insights across the application lifecycle. This initiative comes as…