 Thenewregion
Iranian Missile Strikes Target Kurdish Forces in Iraq
Article Content

- •Six Iranian ballistic missiles struck Kurdish Peshmerga bases, killing six and injuring thirty.
- •The Kurdistan Region has faced over four hundred strikes since late February, impacting regional stability.
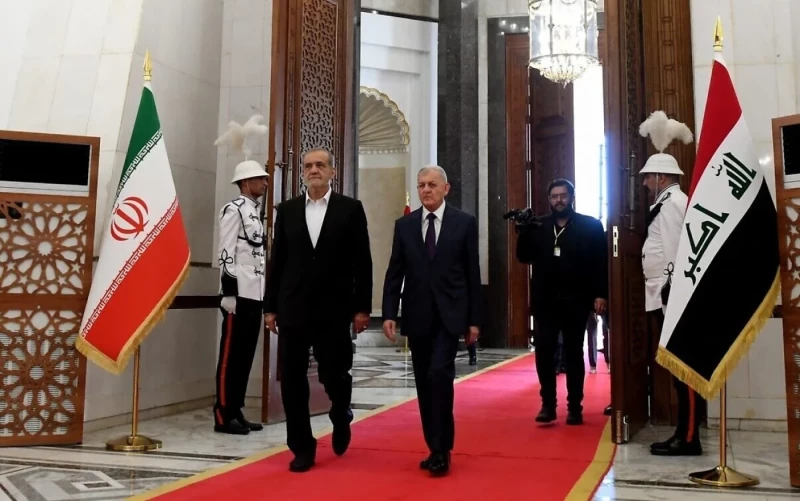
- •Iraqi President condemned the attacks, calling for dialogue and emphasizing Iraq's sovereignty.
On March 24, 2026, six Iranian ballistic missiles struck Peshmerga bases in the Soran highlands, resulting in six fatalities and thirty injuries among Kurdish security forces. This attack marks the deadliest incident since the onset of the war in Iran and is part of a broader campaign of aggression against the Kurdistan Region, which has experienced over four hundred missile and drone strikes since late February. Iraqi President Abdul Latif Rashid condemned the attacks during a call with Iranian President Masoud Pezeshkian, emphasizing the need for dialogue and regional stability. The Kurdistan Region has faced systematic targeting of its energy infrastructure, with significant damage reported. The ongoing conflict has raised concerns over Iraq's sovereignty and the effectiveness of its government in protecting its territory from Iranian aggression. The situation remains tense as both Iranian and US interests are actively engaged in the region.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Following this threat?
Track Peshmerga in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…