 Socprime
Malware-as-a-Service Campaign Targets Users with ClickFix and Cruciferra
Article Content

- •The campaign combines ErrTraffic and Cruciferra to distribute malware and evade security.
- •Attackers use compromised WordPress sites and social engineering tactics to deliver payloads.
- •The vulnerable DCRCVDrv.sys driver allows attackers to disable security processes at the kernel level.
A new Malware-as-a-Service (MaaS) campaign has emerged, utilizing ErrTraffic and Cruciferra to distribute malware while evading endpoint security. The campaign, identified by eSentire's Threat Response Unit, began in late July 2026 and involved compromised WordPress sites delivering obfuscated JavaScript that resolved command-and-control addresses via the Ethereum blockchain. Attackers employed social engineering tactics, including fake Google reCAPTCHA and BSOD lures, to trick users into executing malicious PowerShell commands. The Cruciferra loader, marketed on underground forums, is designed to disable antivirus and EDR processes by exploiting a vulnerable driver, DCRCVDrv.sys. This driver is not recognized by Microsoft’s blocklist, making it particularly dangerous. Organizations are advised to block the vulnerable driver directly and implement security awareness training to mitigate risks. The campaign highlights the increasing sophistication of MaaS offerings in cybercrime.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ClickFix and Polygon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
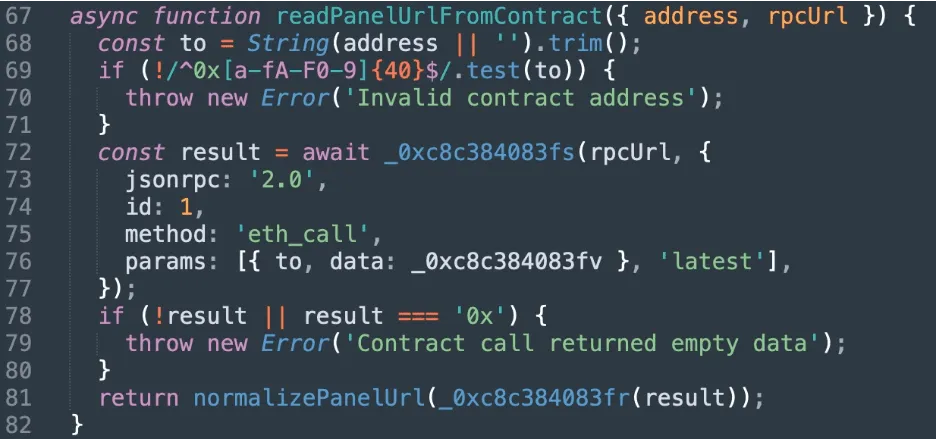 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…