 Securityaffairs.Co
Massive Stripe API Breach Exposes 20,000 Compromised Keys and Customer Data
Article Content

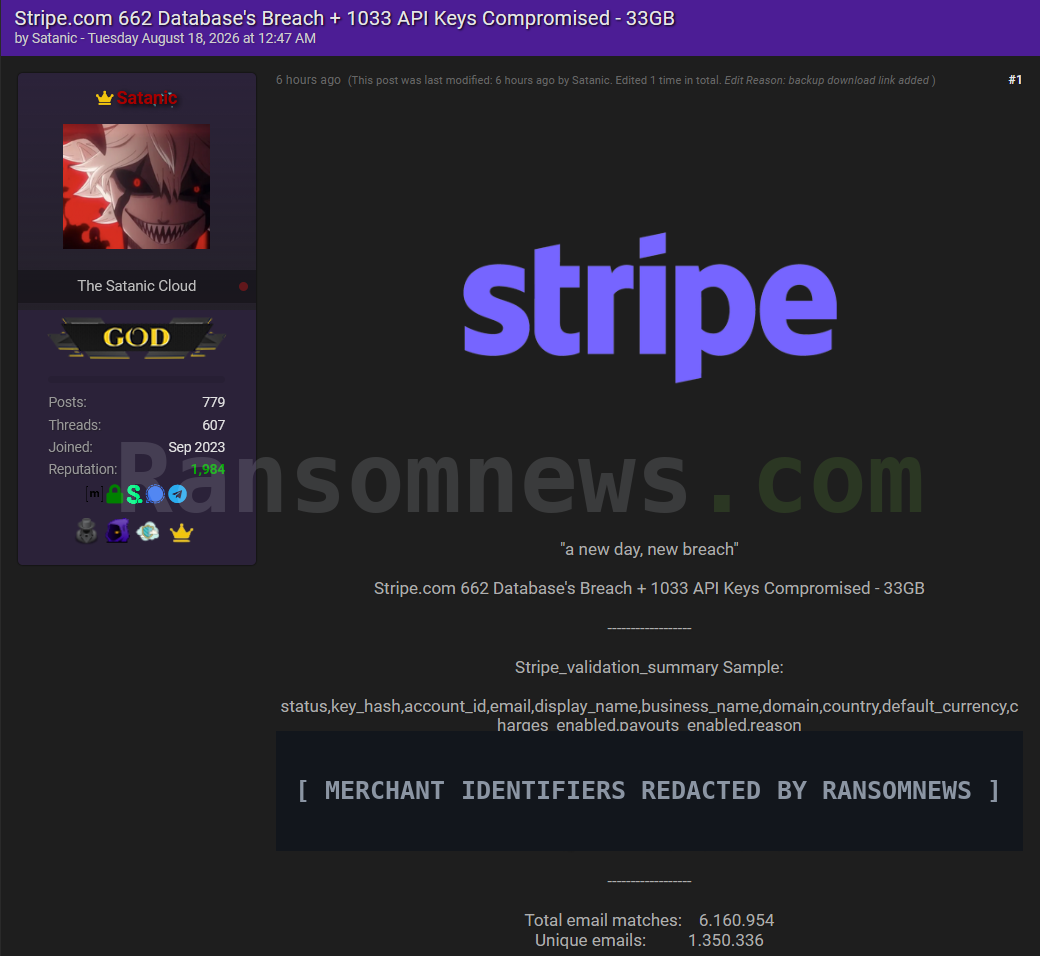
- •Satanic released sensitive data from 669 vendors using Stripe, claiming 20,000 compromised APIs.
- •The initial data dump contained 1,033 API keys and affected approximately 688,363 customer records.
- •Over 50,000 Stripe API keys were also leaked through public code repositories, increasing risks.
On August 18, 2026, a threat actor named Satanic released sensitive data from 669 vendors using Stripe, claiming to possess 20,000 compromised APIs. The initial dump included 1,033 API keys and 33GB of data, affecting approximately 688,363 customer records. The data leak, advertised as a staggered release, contains detailed transaction information, including personal identifiable information (PII) and financial metadata. Other reports indicate that over 50,000 Stripe API keys were also leaked through public code repositories. The breach did not involve a compromise of Stripe's infrastructure but poses significant risks to affected vendors and their customers. Security researchers are currently analyzing the data to assess the full impact and potential for exploitation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…