 carnegieendowment.org
Mexico's Cybersecurity Strategy Faces Challenges Amid Rising Threats
Article Content

- •Mexico's cybersecurity strategy has stalled under President AMLO, with inadequate federal response.
- •A new National Cybersecurity Plan was introduced in December 2025 to address rising threats.
- •Cyber incidents have increasingly targeted key sectors, including government and healthcare.
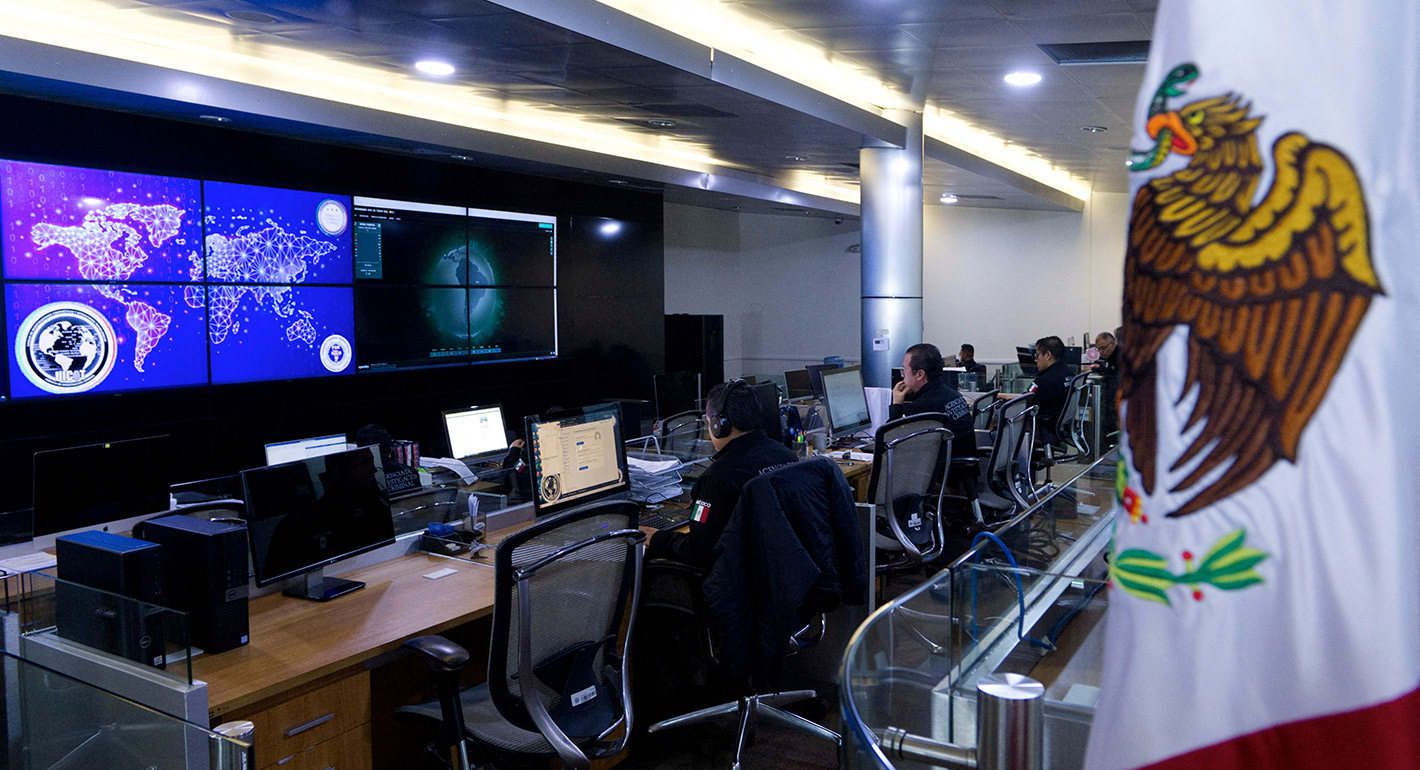
Mexico's National Cybersecurity Strategy, initiated in 2017, has seen stalled progress under President Andrés Manuel López Obrador (AMLO). The country faces significant cybersecurity threats, including ransomware, organized crime, and geopolitical risks, exacerbated by inadequate federal response and funding cuts. A new National Cybersecurity Plan was unveiled in December 2025, aiming to address these issues and enhance national resilience. However, the effectiveness of this plan remains uncertain without strong presidential support and coordination. Cyber incidents have increasingly targeted government, healthcare, and financial sectors, highlighting the urgent need for improved defenses. The 2026 FIFA World Cup poses an additional challenge, testing Mexico's cybersecurity capabilities amid heightened scrutiny. The ongoing rise in cybercrime, particularly from hacktivist groups and organized crime, underscores the critical state of Mexico's cybersecurity landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Blackbyte, RedLima and Legal Counsel’s Office Of The Presidency in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CDK Global Suffers Multiple Ransomware Attacks in June CDK Global, a software vendor for car dealerships, experienced a ransomware attack on June 18, 2026, which forced the company to shut down its systems to contain the breach. As CDK began to restore its services, it was hit by a second attack on June 19, disrupting operations for numerous dealerships reliant on its…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…