 Infosecurity-Magazine
NCSC Launches SilentGlass to Secure Monitor Connections Against Cyber Threats
Article Content

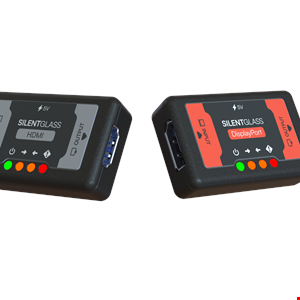
- •SilentGlass is a new device that secures HDMI and DisplayPort connections from cyber threats.
- •The device is designed for high-threat environments and is now available for global use.
- •NCSC emphasizes the importance of securing monitor connections to protect sensitive data.
On April 22, 2026, the UK National Cyber Security Centre (NCSC) introduced SilentGlass, a plug-and-play device designed to protect video connections from cyber-attacks. This device actively blocks unexpected or malicious HDMI and DisplayPort connections, addressing a significant vulnerability in monitor security. SilentGlass has been successfully deployed in high-threat environments, including government estates, and is now available for global purchase. The NCSC, in collaboration with Goldilock Labs and Sony UK, aims to enhance cybersecurity for organizations handling sensitive data. The device is expected to see rapid adoption among governments and businesses concerned about cybersecurity risks. The NCSC highlights that monitors are attractive targets for cyber threat actors due to the sensitive information they display. SilentGlass represents a shift towards treating hardware interfaces as critical security boundaries, previously overlooked in cybersecurity measures. The launch was announced during the CYBERUK 2026 conference in Glasgow, Scotland.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (12)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…