 Securityaffairs.Co
New Zero-Day Exploit FalconFlank Targets CrowdStrike Falcon Platform
Article Content

- •FalconFlank exploits a privilege escalation flaw in CrowdStrike Falcon.
- •The exploit works on Windows 11 25H2 and Windows Server 2025 with specific configurations.
- •Chaotic Eclipse has a history of releasing exploits for multiple cybersecurity platforms.
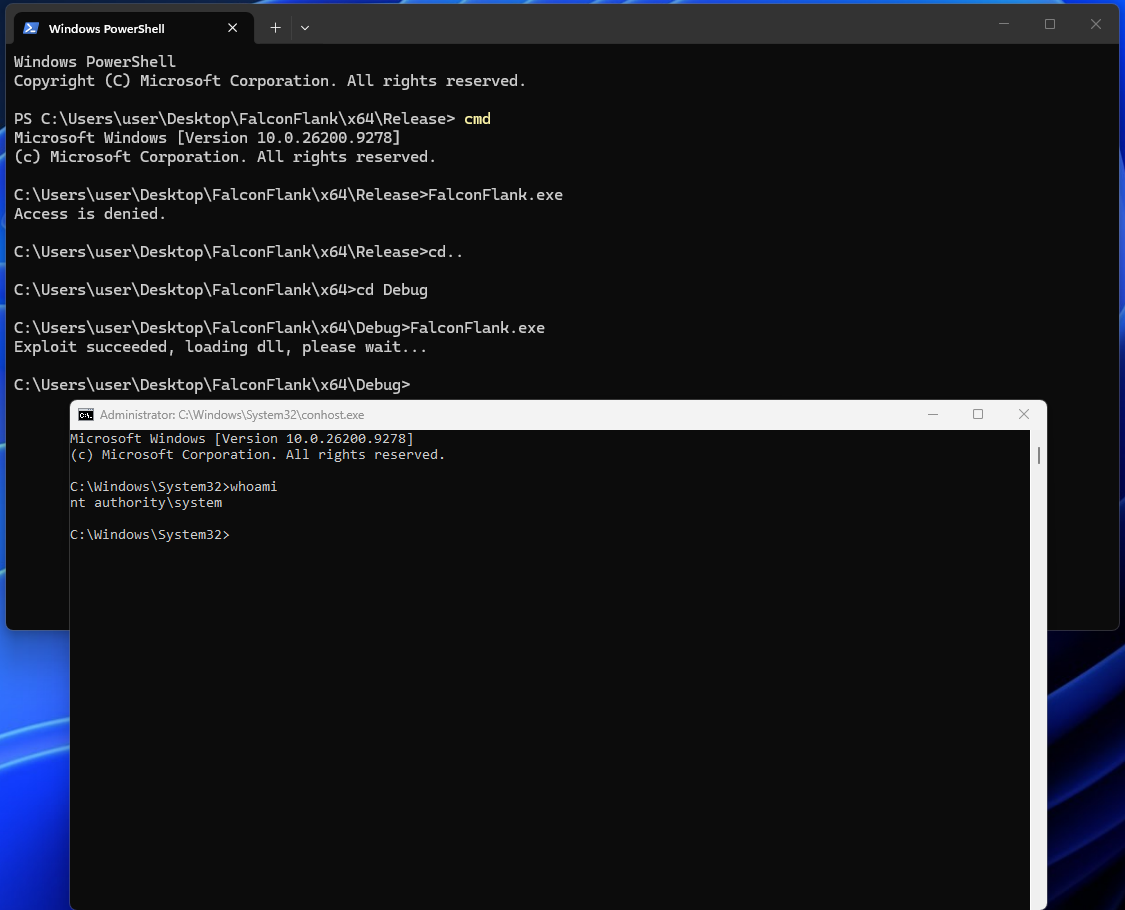
Chaotic Eclipse released FalconFlank, a proof-of-concept exploit for a zero-day privilege escalation vulnerability in the CrowdStrike Falcon cybersecurity platform. The exploit leverages the platform's 'Microsoft Office file malicious macro removal' feature to escalate privileges from a low-privileged user to a higher context. It is confirmed to work on fully updated Windows 11 25H2 and Windows Server 2025 systems running CrowdStrike Falcon with Phase 3 - Optimal Protection. The researcher warns that CrowdStrike may already have detections for this exploit, indicating that while the vulnerability exists, it may be mitigated by the software. This release follows other exploits targeting Kaspersky and Microsoft Defender, showcasing a pattern of targeting major cybersecurity solutions. The researcher has previously noted issues with the stability of their exploits, indicating that repeated attempts may be necessary for successful execution.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (10)
Following this threat?
Track CrowdStrike and CVE-2026-50656 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Tanium Enhances Security Operations for AI-Driven Threats Tanium has relaunched its Security Operations platform to address new AI-driven attack methods that mimic legitimate administrative behavior. The updated platform focuses on detecting abnormal endpoint behavior rather than relying solely on known malware signatures. This shift is crucial as attackers can now use…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…