 Technadu
Nihon Kotsu Cyberattack Disrupts Taxi Services in Japan
Article Content

- •Nihon Kotsu's systems were compromised via malware, disrupting taxi services.
- •The company has engaged external cybersecurity specialists for investigation and recovery.
- •No confirmed data leaks have been reported, but the investigation is ongoing.
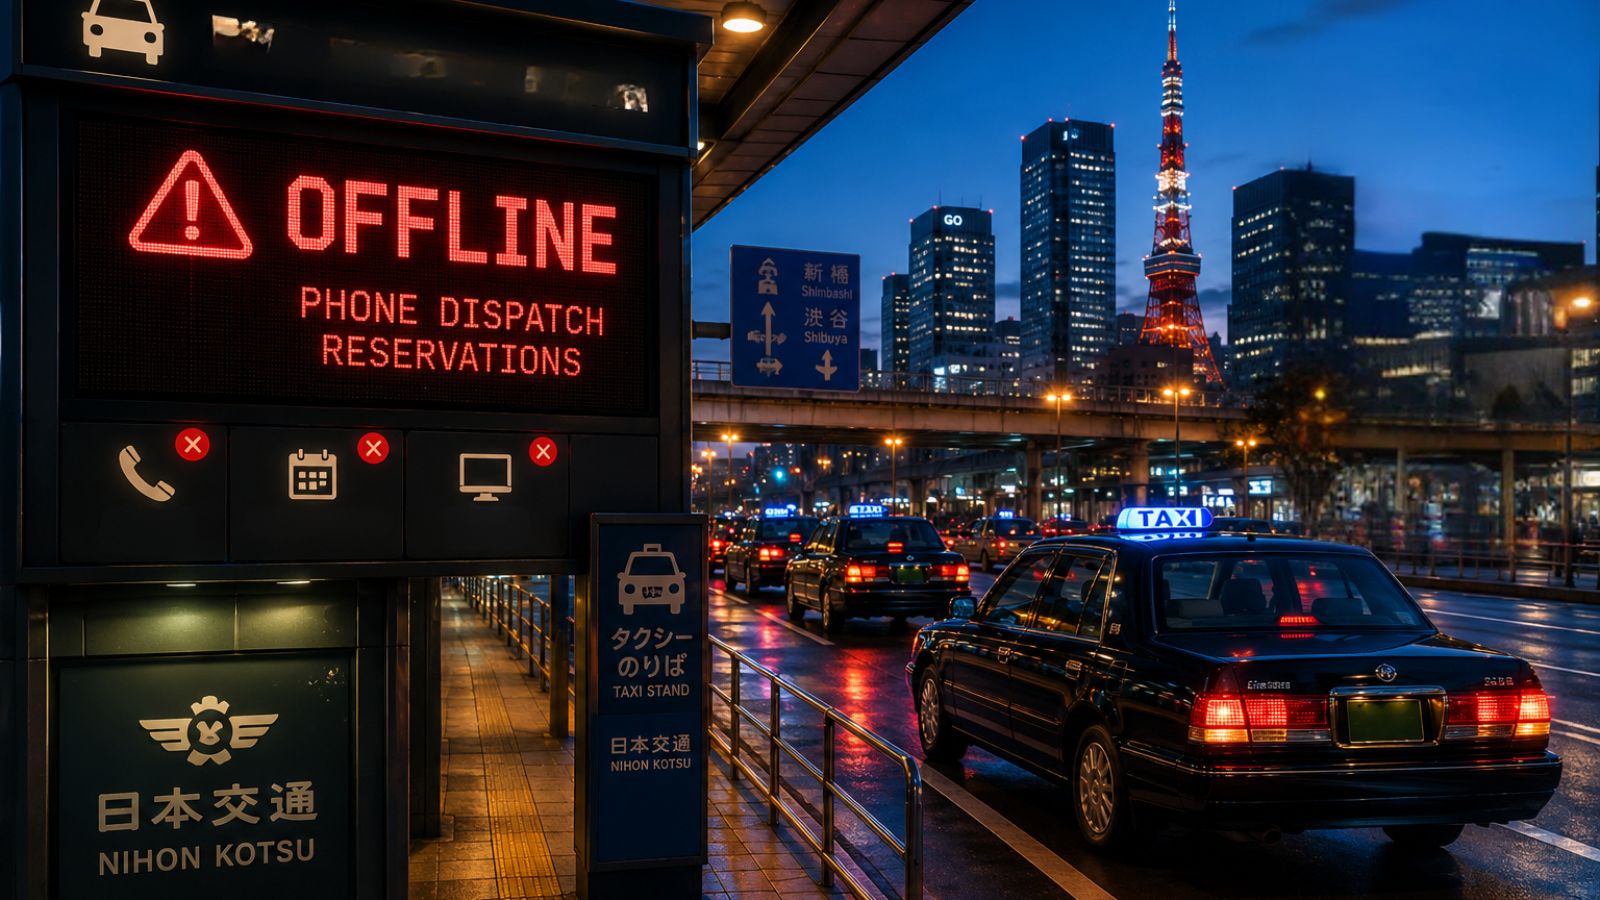
On July 11, 2026, Nihon Kotsu, Japan's largest taxi operator, experienced a cyberattack that compromised its internal systems through malware infection. This incident forced the company to shut down its taxi dispatch system and other critical services, impacting operations for its fleet of 8,558 taxis and over 2,000 chauffeur vehicles. The company, which generates approximately ¥155 billion annually, has advised customers to use the GO taxi app or hail taxis directly while the systems remain offline. Nihon Kotsu is collaborating with external cybersecurity experts to investigate the breach and assess potential data exposure. As of now, no data leaks have been confirmed, but the investigation is ongoing. The company has also warned customers against opening suspicious communications claiming to be from Nihon Kotsu.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (13)
Following this threat?
Track Nihon Kotsu in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…