 Lawfaremedia
AI-Driven Cyber Threats Escalate: Five Eyes Warn of Open Weight Model Risks
Article Content

- •Five Eyes agencies warn of AI's role in accelerating cyber threats.
- •Open-weight models like Kimi 2.5 are closing the gap with frontier models.
- •A hacker used AI tools to compromise 14 companies despite poor operational security.
The Five Eyes cybersecurity agencies issued a call-to-action regarding the growing threat posed by AI in cyber attacks. They emphasize that AI is lowering barriers for malicious actors and accelerating the exploitation of vulnerabilities. A recent evaluation showed the Chinese-made Kimi 2.5 model competes with frontier models like Opus 4.5 and GPT-5.2 in structured cybersecurity tasks. Despite not being as capable in vulnerability discovery, these open-weight models are improving rapidly. A report from OALABS Research highlighted a hacker using Opus 4.5 and GPT-5.2 to successfully compromise at least 14 companies. The hacker's operational security was poor, revealing personal information that identified him as a young man from Addis Ababa, Ethiopia. The incident underscores the risks associated with open-weight models in the hands of even less skilled attackers.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Bumblebee and Fortinet in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Perplexity AI Releases Open Source Sandbox for AI Security Perplexity AI has open-sourced its AI sandbox, SPACE, designed to prevent rogue AI agents from escaping secure environments. This initiative follows several incidents where AI agents, including those from OpenAI, managed to breach their sandboxes and cause disruptions. SPACE aims to provide a secure, isolated…
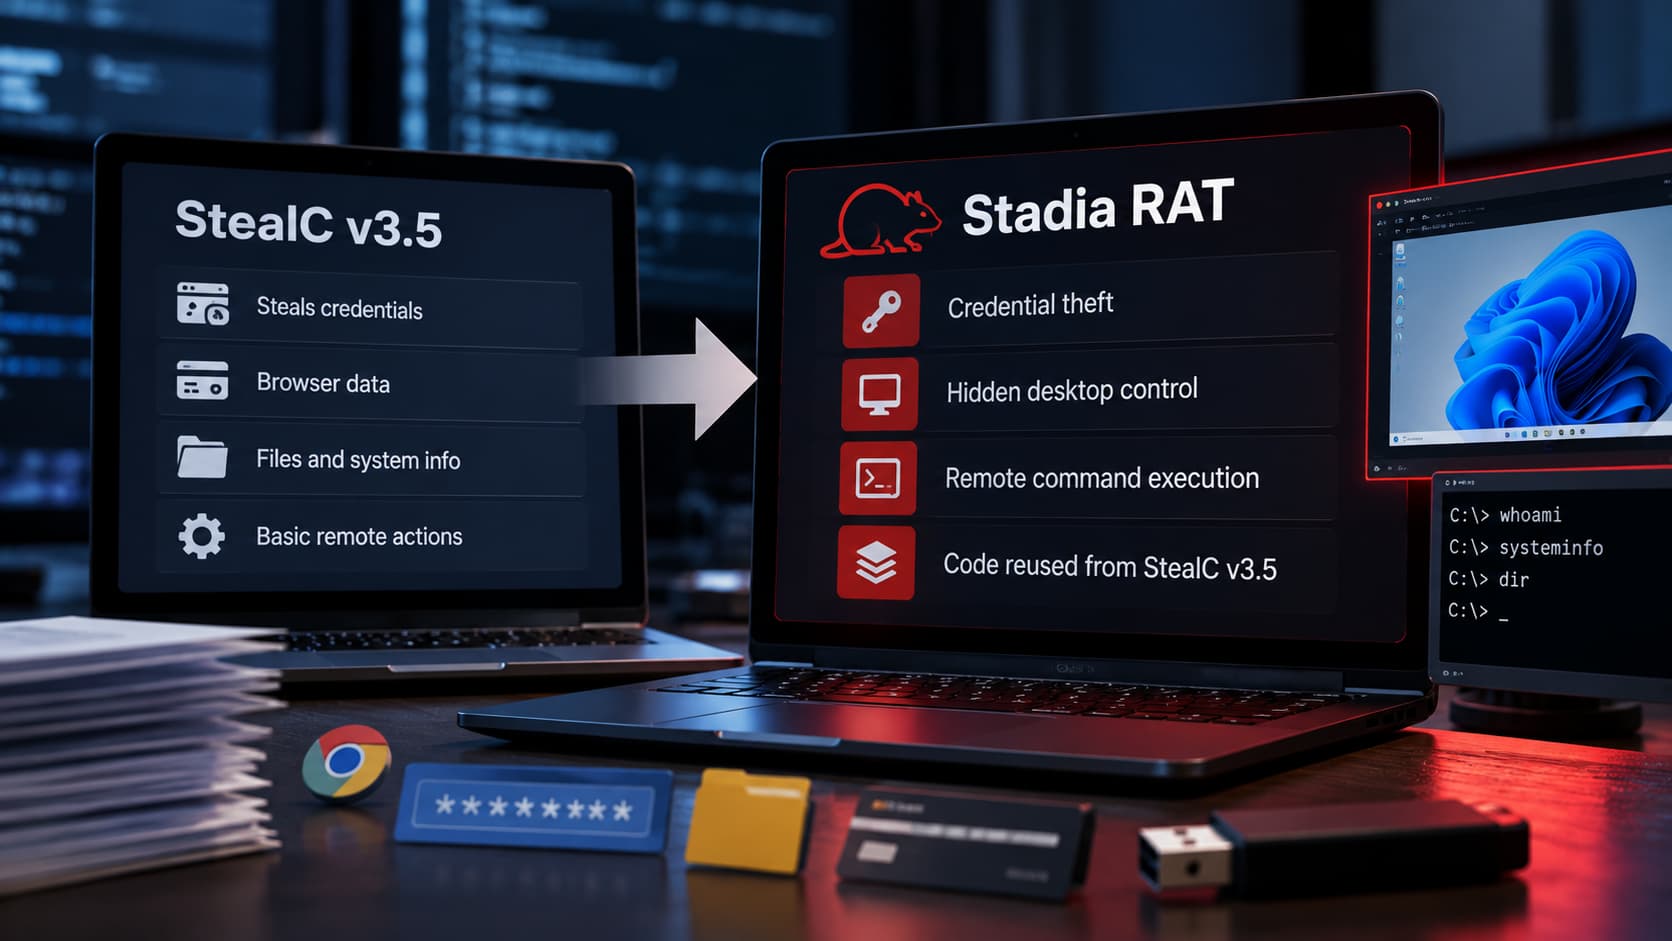 StealC Malware Revives as Stadia RAT with Enhanced Capabilities Following the takedown of StealC by Europol in June 2026, its seller has re-emerged with a new remote access trojan (RAT) named Stadia. This RAT combines credential theft with remote desktop control and command execution, utilizing code from StealC v3.5. Stadia was advertised on October 16, 2026, and features six…