 Securityaffairs.Co
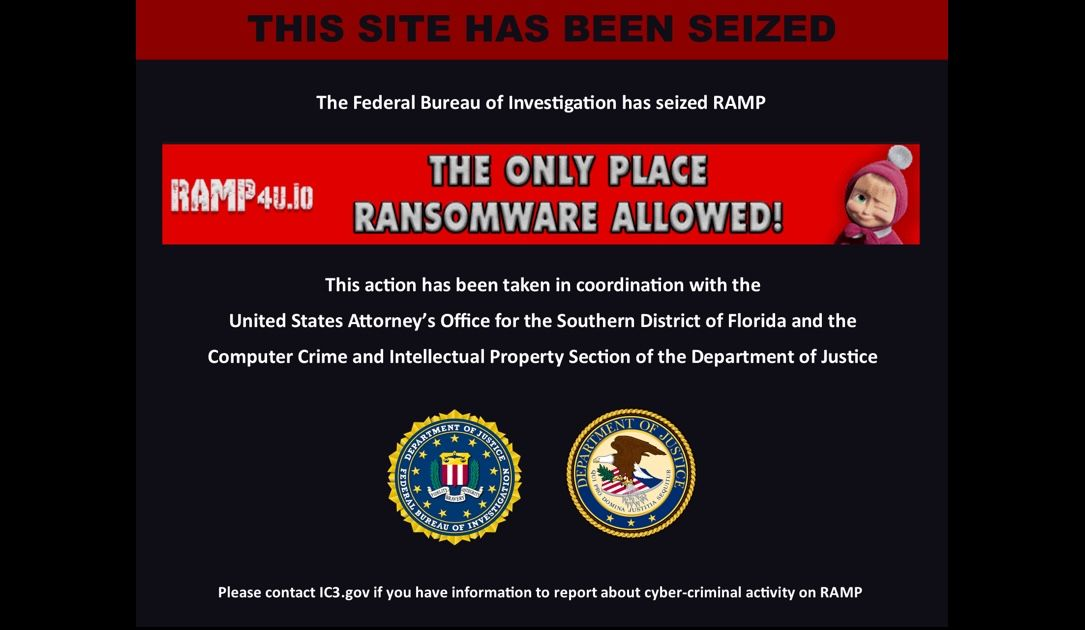
RAMP Ransomware Marketplace Exposed: Insights into Organized Cybercrime
Article Content

- •RAMP's leaked data reveals a structured ransomware marketplace with over 7,700 users.
- •The marketplace facilitated organized cybercrime, including recruitment and deal negotiations.
- •The exposure of RAMP may prompt increased law enforcement actions against cybercriminal networks.
A leaked database from RAMP, a Russian ransomware marketplace, reveals detailed insights into its operations. The data includes analysis of 1,732 threads, 7,707 users, and 340,000 IP records, showcasing a structured ecosystem where cybercriminals engage in buying, selling, and recruiting. RAMP operated like a business platform, allowing for the negotiation of ransomware deals and the advertisement of services. This organized approach marks a significant evolution in cybercrime, moving away from isolated attacks to a more commercialized model. The implications of this leak highlight the growing sophistication of ransomware operations and the potential for increased attacks on various sectors. Current status indicates that the information is being analyzed for further insights into the threat landscape. The exposure of RAMP may lead to increased law enforcement scrutiny and potential takedowns of similar platforms.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…