 Itnews.Au
ACSC Issues Critical Alert on Exploited CMS Vulnerabilities
Article Content

- •ACSC warns of a critical alert on CMS vulnerabilities exploited in a large-scale campaign.
- •17 vulnerabilities are targeted, including CVE-2025-32432 affecting Craft CMS.
- •Administrators are urged to apply patches and check for indicators of compromise.
The Australian Cyber Security Centre (ACSC) has issued a second alert in two months regarding a large-scale hacking campaign exploiting unpatched vulnerabilities in content management systems (CMS). The campaign targets 17 specific vulnerabilities, affecting websites globally, particularly those of small- to medium-sized businesses in Australia. Notably, CVE-2025-32432, a zero-day vulnerability in Craft CMS, was exploited for two months before a patch was released in April 2025. Other affected systems include various WordPress plugins like GutenKit and Hunk Companion, which were patched in 2024 but continue to see exploitation attempts. The ACSC advises administrators to check for indicators of compromise and apply available security updates immediately. The alert follows a previous warning about the ClickFix campaign, which delivered malware to compromised WordPress sites. The situation has escalated to a critical alert status due to the ongoing exploitation of these vulnerabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (10)
Following this threat?
Track ClickFix and CVE-2025-32432 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
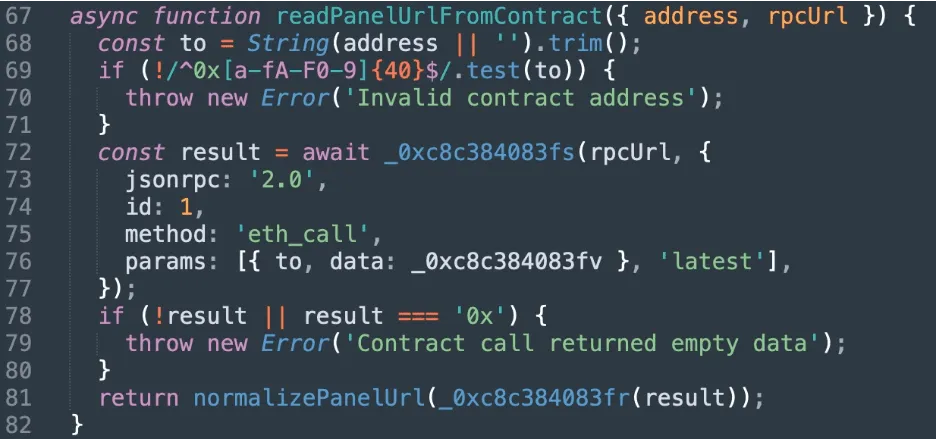 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…