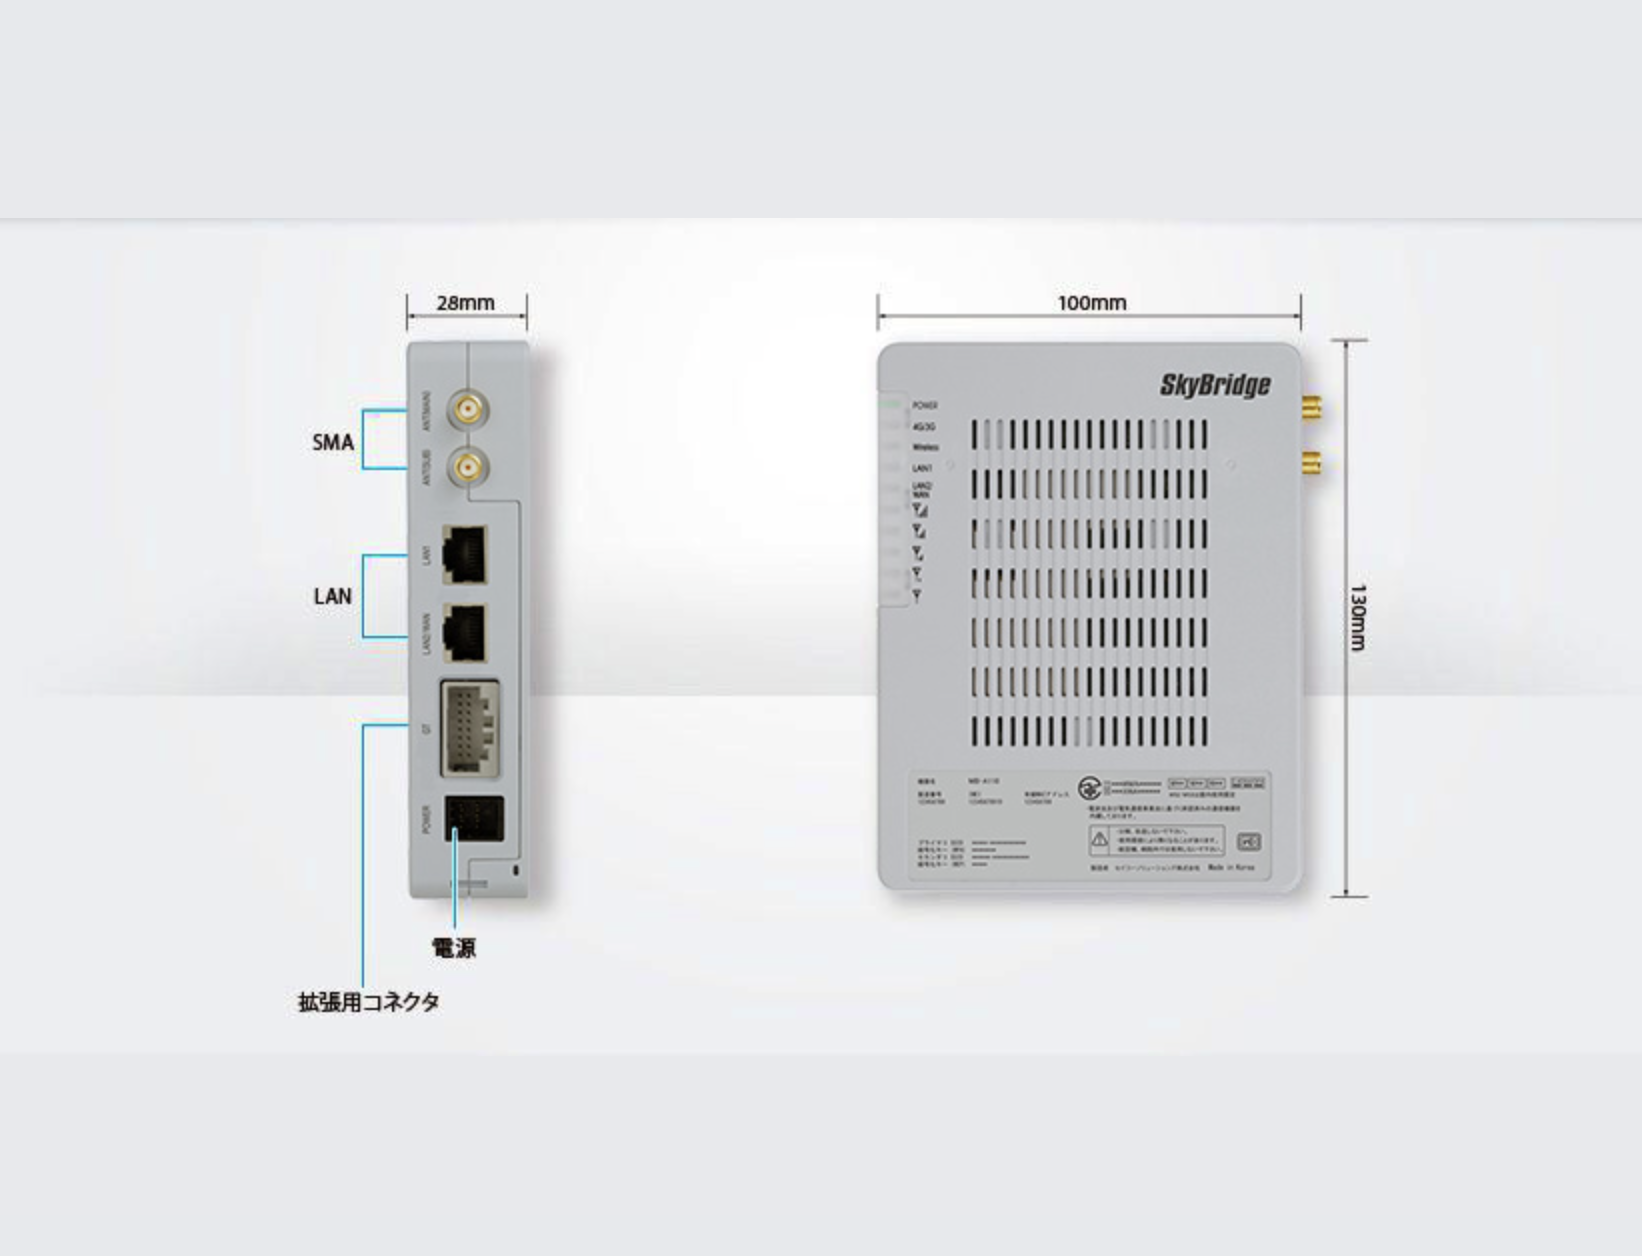
 Techtimes
Seiko SkyBridge IoT Routers Face Permanent OS Injection Vulnerability
Article Content

- •SkyBridge MB-A100 and MB-A110 routers have a critical OS command injection vulnerability.
- •No firmware patch will be released, leaving devices permanently vulnerable.
- •Organizations are urged to change default credentials and limit access to mitigate risks.
Seiko Solutions' SkyBridge MB-A100 and MB-A110 routers are affected by a high-severity OS command injection vulnerability (CVE-2026-50043) disclosed on July 1, 2026. The flaw allows authenticated attackers to execute arbitrary OS commands via the web administration interface. Seiko has confirmed that no firmware patch will be released, leaving these devices permanently vulnerable. This is the third significant OS command injection vulnerability discovered in this product line, following CVE-2022-36556 and CVE-2025-29635. Organizations using these routers are advised to take immediate action to mitigate risks, as the devices may still retain default credentials or weak passwords. The vulnerability has a CVSS base score of 8.6, indicating a high severity level. The advisory was coordinated by JPCERT/CC and Japan's Information-Technology Promotion Agency.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Mirai, Information-Technology Promotion Agency and CVE-2022-36556 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical cPanel Vulnerability Exploited for Hosting Server Compromise Threat actors exploited CVE-2026-41940, a critical authentication bypass in cPanel and WHM, allowing remote, unauthenticated access to hosting servers. The vulnerability, with a CVSS score of 9.8, affects cPanel versions released after 11.40. Following the public disclosure on April 29, 2026, exploitation activity…
 Cling Botnet Exploits Realtek SDK Flaw Using STUN Traffic for C2 The Cling botnet has been identified as exploiting a critical vulnerability (CVE-2021-35394) in the Realtek Jungle SDK, allowing attackers to deploy malware that disguises command-and-control (C2) traffic as legitimate STUN protocol exchanges. This vulnerability, which has a CVSS score of 9.8, was first exploited…