 Bitbo
Senator Warren Demands Probe into Bitmain's Security Risks Amid National Concerns
Article Content

- •Senator Warren demands an investigation into Bitmain's security risks.
- •Concerns include potential espionage and power grid vulnerabilities.
- •Bitmain is set to open a U.S. ASIC manufacturing facility amid scrutiny.
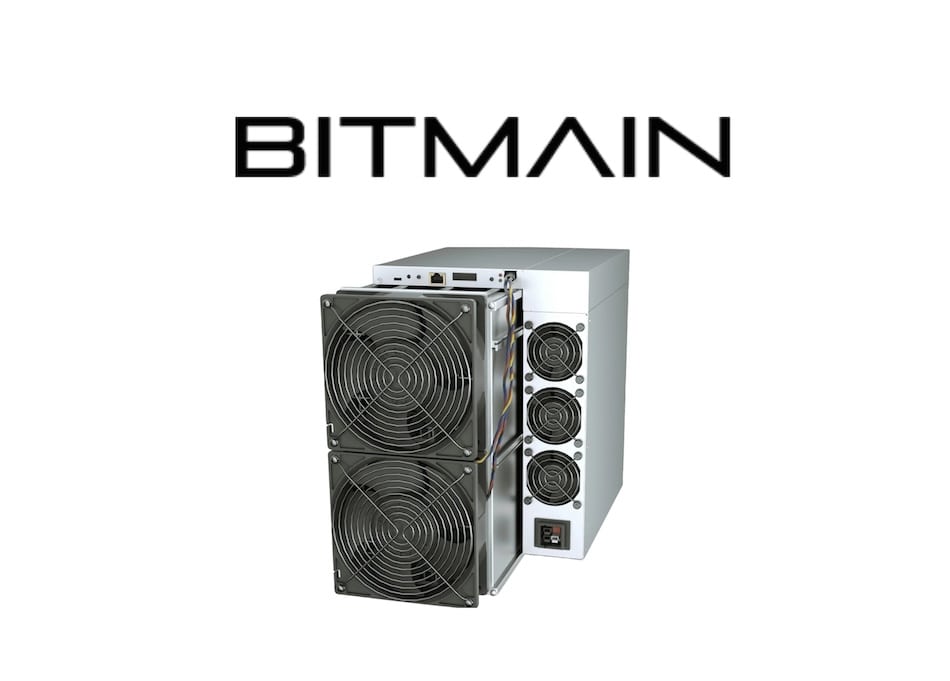
U.S. Senator Elizabeth Warren has formally requested an investigation into Bitmain, a Chinese manufacturer of cryptocurrency mining equipment, citing national security risks. Her letter to Commerce Secretary Howard Lutnick highlights concerns over potential espionage capabilities and vulnerabilities to the U.S. power grid. This follows the classified 'Operation Red Sunset' launched in November 2025 by the Department of Homeland Security, which aims to assess whether Bitmain's ASIC machines could be exploited for remote access. The investigation remains unresolved, with previous reviews indicating significant risks associated with Bitmain's equipment near military installations. Despite ongoing scrutiny, Bitmain is reportedly preparing to open its first U.S.-based ASIC production facility in early 2026. Warren's inquiry also seeks details on communications between Bitmain and U.S. officials, emphasizing the need for transparency in national security decisions. The situation reflects broader concerns about foreign technology in critical infrastructure, reminiscent of past issues with Huawei and ZTE.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Bitmain Technologies in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…