 Straitstimes
Singapore CASE Warns Public of Phishing Email Scams
Article Content

- •CASE warns of phishing emails impersonating its officers.
- •Scammers claim recipients are eligible for compensation, prompting personal info requests.
- •Public advised to verify email authenticity before taking action.
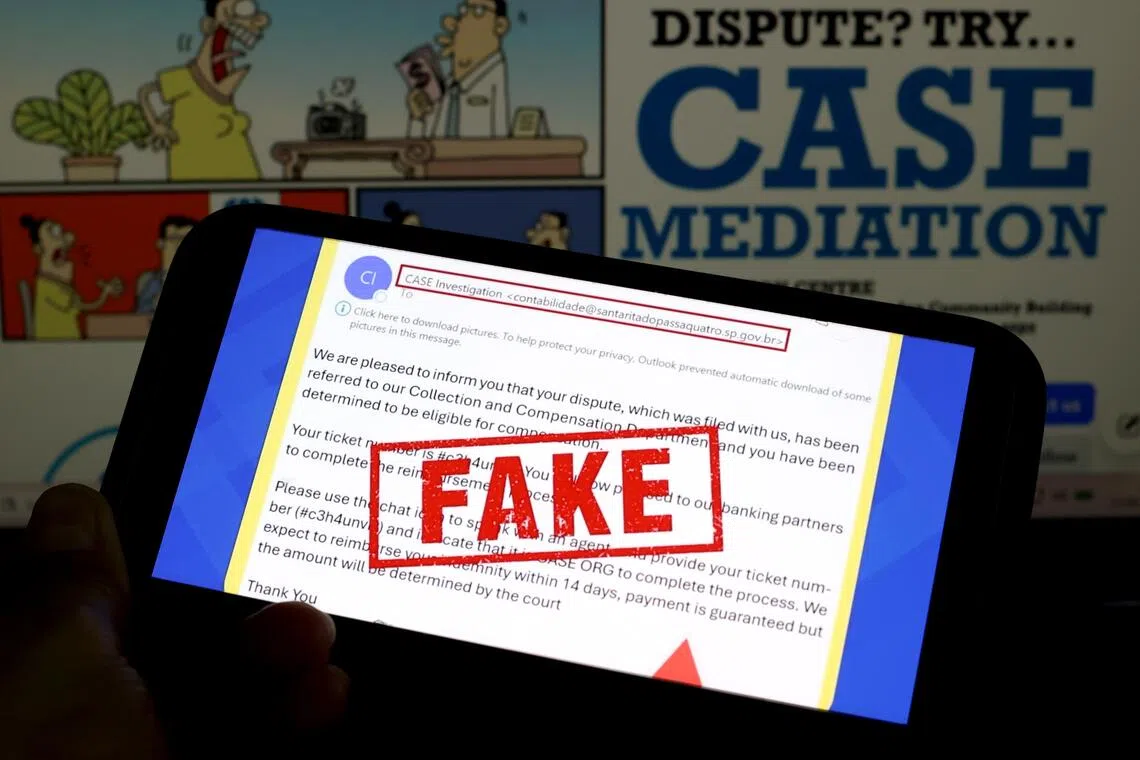
On August 21, 2026, the Consumers Association of Singapore (CASE) issued a warning about phishing emails impersonating its officers. These emails claim recipients are eligible for compensation related to disputes with CASE, urging them to click links and provide personal information. CASE highlighted that the sender's email addresses often do not originate from its official domain, indicating potential fraud. The organization advised the public to verify any suspicious emails by checking the sender's address and to avoid clicking on unknown links. CASE also provided a helpline number for verification. The warning aims to protect consumers from falling victim to these scams, which exploit trust in official communications.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…