 Trendmicro
Phishing Campaign Targets Japan's Hotels Using TONResolver RAT
Article Content

- •Phishing emails targeted Booking.com partners in Japan with guest complaint lures.
- •The TONResolver RAT uses the TON blockchain for command-and-control evasion.
- •Traditional email security measures failed to prevent these sophisticated attacks.
In late May 2026, a phishing campaign targeting Japan's hotel industry was identified, utilizing emails that impersonated guest complaints to deliver the TONResolver RAT. The emails, sent to Booking.com partner accommodations, contained malicious links leading to a ZIP file with a disguised shortcut file (LNK) that installed the TrojanSpy.JS.TONRESOLVER.A malware. This malware exploits the TON blockchain as a dead drop resolver, complicating detection and takedown efforts. Japanese hotels were primarily targeted, although other countries were also affected. The attack method bypassed traditional email security measures like SPF, DKIM, and DMARC. The persistent nature of the malware poses ongoing risks for credential theft and further compromises. Trend Micro's TrendAI Research confirmed the attack's details and scope, emphasizing the sophistication of the phishing tactics employed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track TONResolver and Cloudflare in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
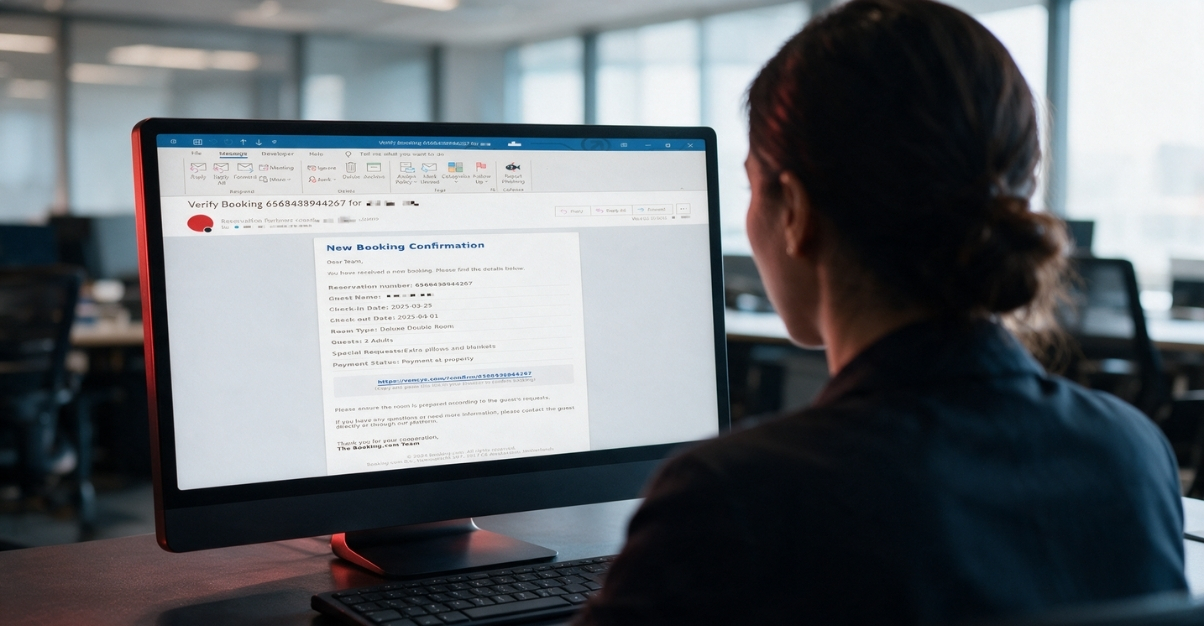 Hotels Targeted by Phishing Campaigns Using Fake Guest Complaints Hackers are targeting the hotel industry with phishing emails containing fabricated guest complaints to deliver EtherRAT and TONResolver malware. These emails, which appear to be a continuation of previous Booking.com-themed attacks, exploit hotel employees' responsibilities to investigate guest issues. The emails…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…