 Cyberscoop
Trump's Executive Order Threatens Voter Rights with New Database Initiative
Article Content

- •Trump's executive order mandates federal voter lists, raising concerns of voter suppression.
- •The initiative relies on controversial databases, potentially misusing sensitive personal data.
- •State officials and Democrats are preparing legal challenges against the executive order.
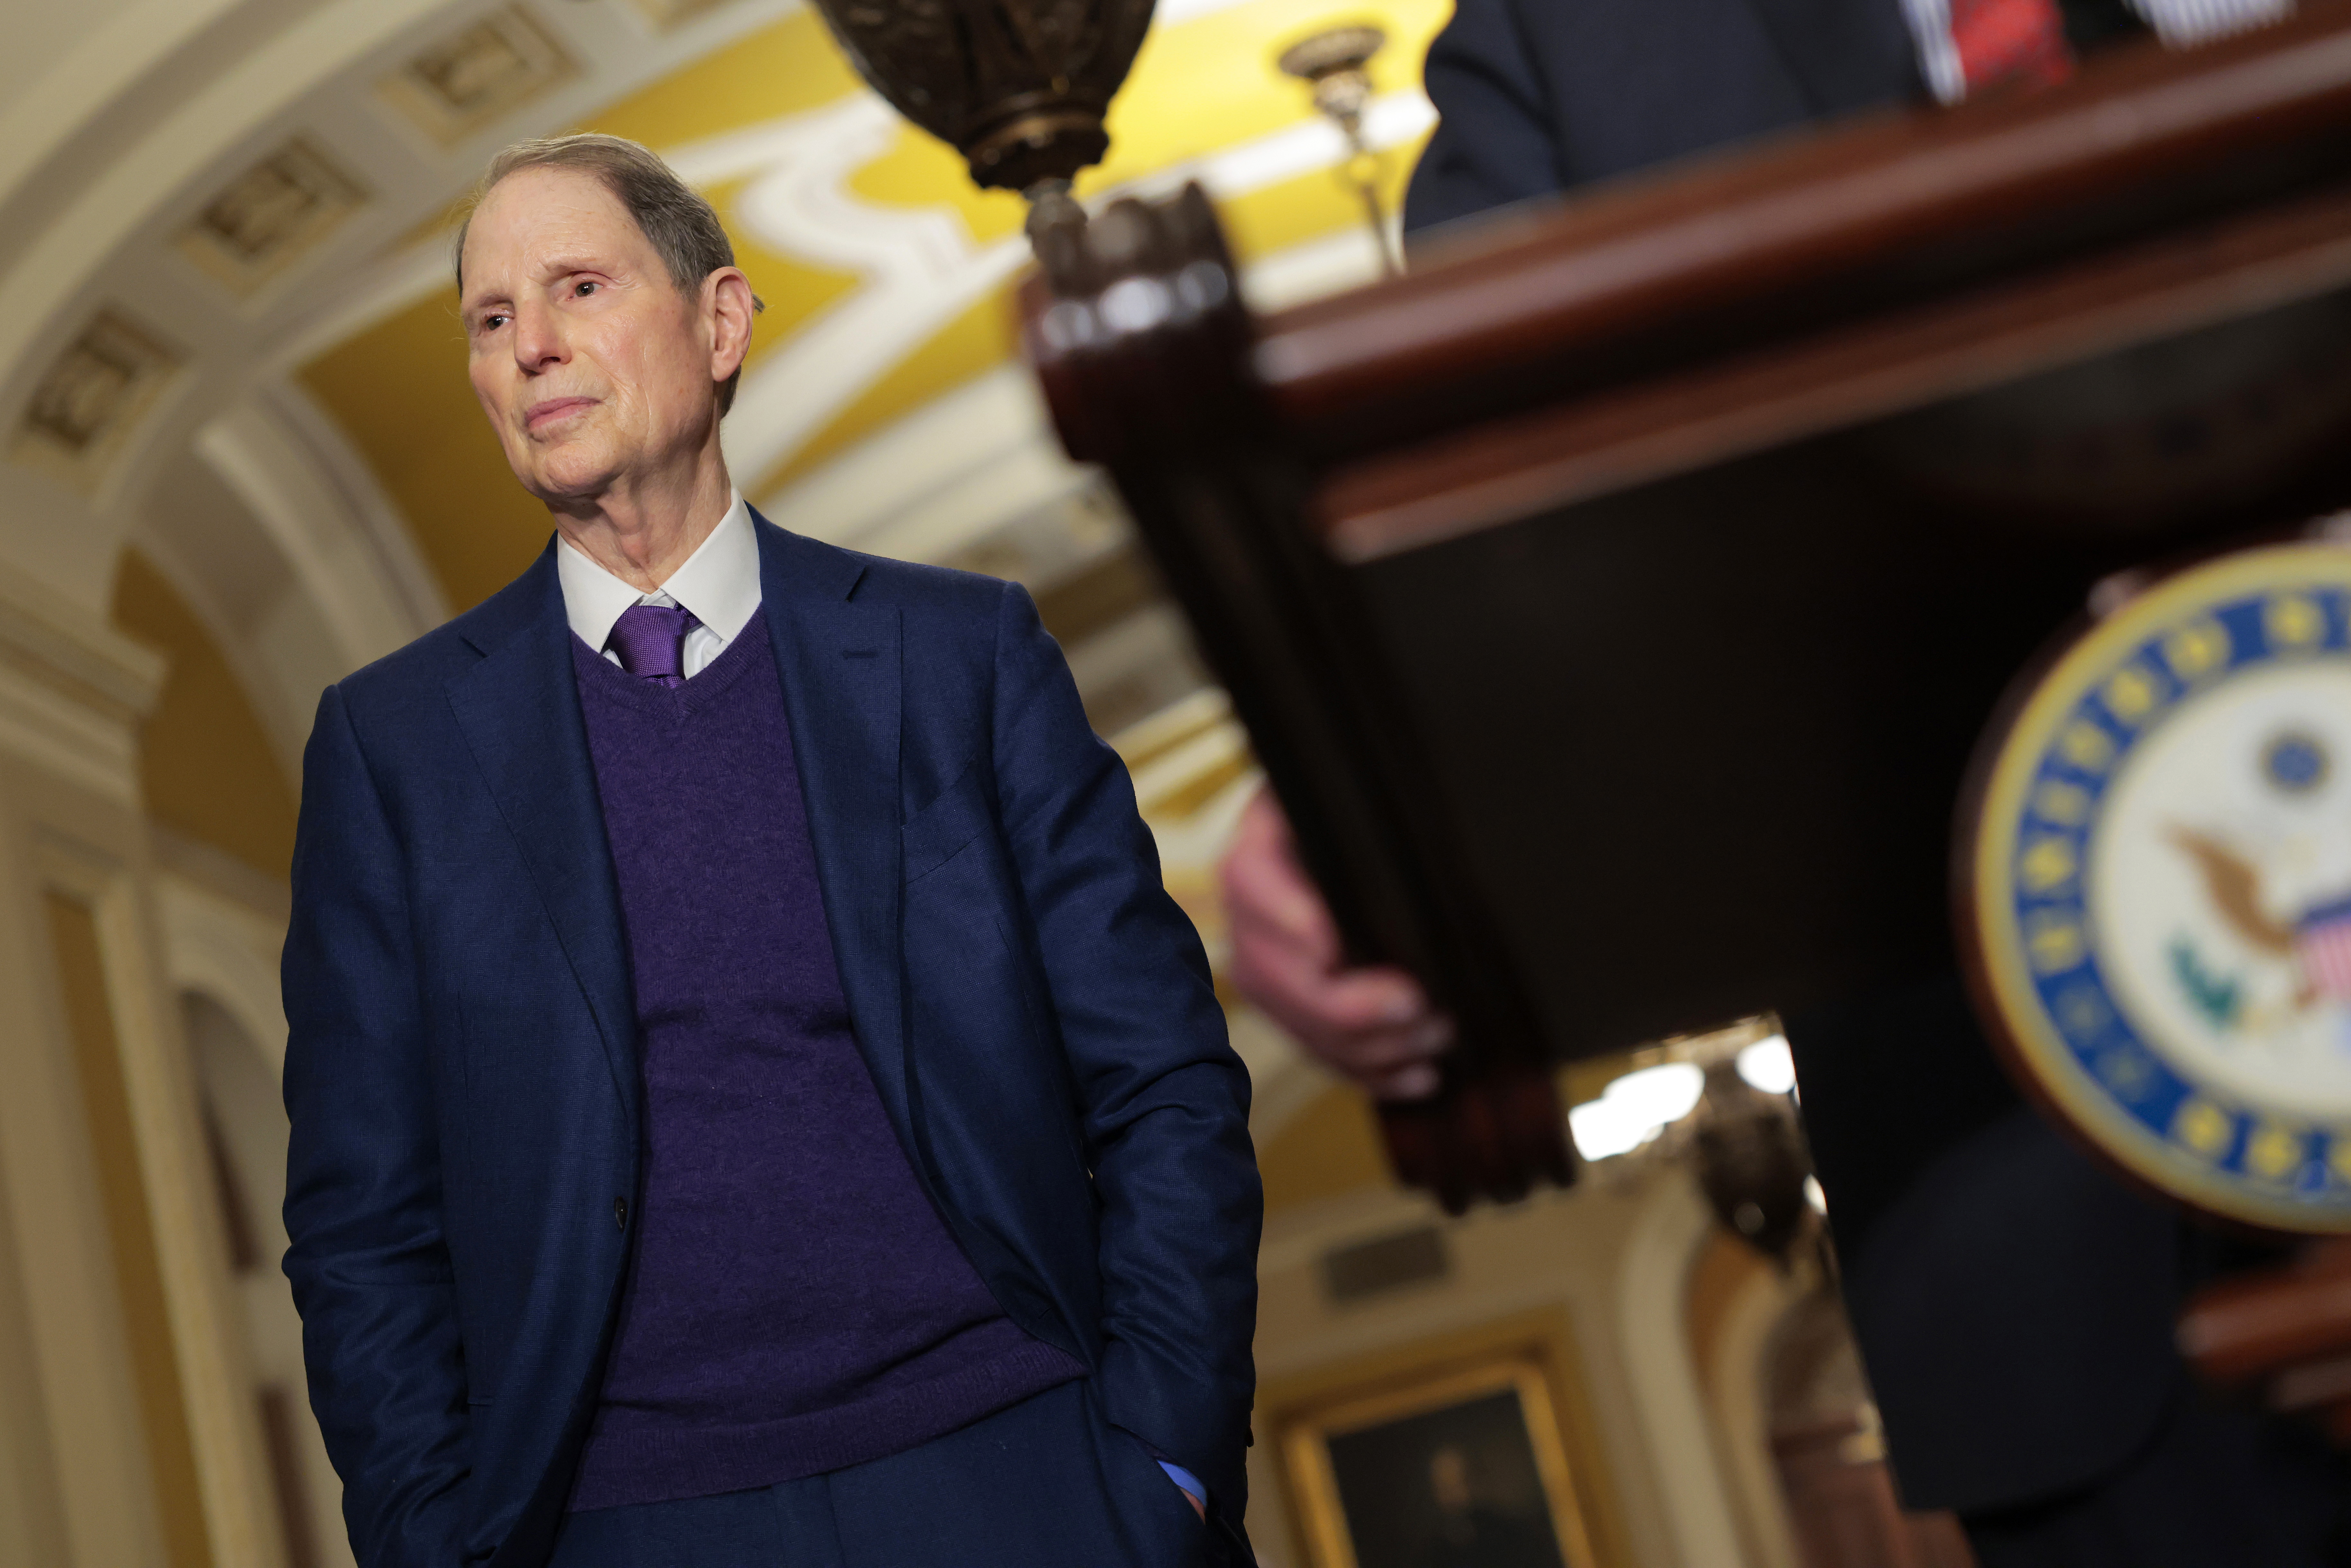
On April 1, 2026, President Donald Trump signed an executive order aimed at limiting mail-in voting and mandating the creation of federal voter lists. The order instructs various federal agencies, including the Social Security Administration, to compile lists of voters based on citizenship status using the Systematic Alien Verification for Entitlements database. Critics, including Senator Ron Wyden, argue that this initiative constitutes voter suppression and violates constitutional provisions regarding election management. The order has faced immediate backlash from state officials and voting rights advocates, with many predicting legal challenges. The directive also empowers the Department of Justice to investigate and prosecute officials who issue ballots to ineligible voters. The executive order's implementation could disenfranchise eligible voters, particularly affecting those reliant on mail-in voting. Legal experts and state officials have indicated that they are exploring options to challenge the order in court, citing its unconstitutional nature. As of now, the order is set to be contested in lawsuits from various stakeholders.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…