 uk.investing.com
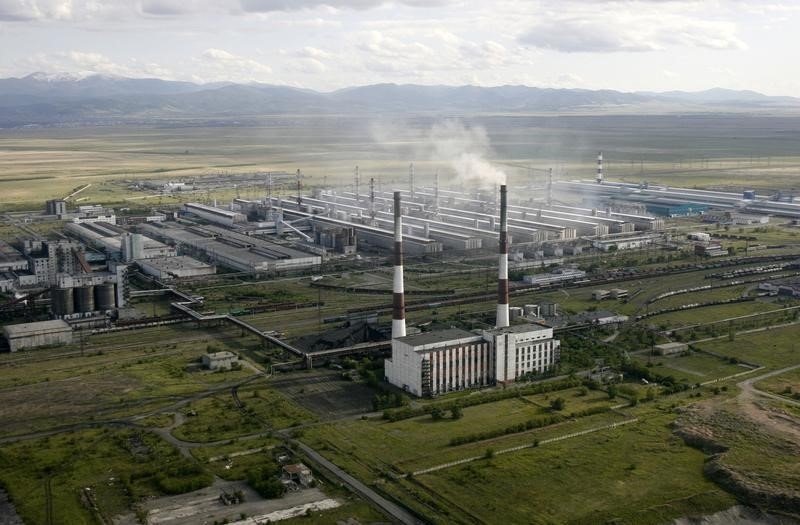
Ukrainian Drone Strike Targets Russian Fertilizer Facility
Article Content

- •Ukrainian forces targeted the Apatit fertilizer plant in Vologda, Russia.
- •Five workers were injured, but no hazardous chemicals were released.
- •This strike is part of Ukraine's strategy to disrupt Russian economic infrastructure.
On April 26, 2026, Ukraine executed a drone strike on the Apatit JSC fertilizer complex in Russia's Vologda region, marking the second attack on this site within the month. The strike caused damage to a high-pressure sulfuric acid pipeline, resulting in five workers being injured and hospitalized. Local governor Georgy Filimonov confirmed that hazardous chemicals were contained and did not leak. This attack is part of Ukraine's broader strategy to disrupt Russian production infrastructure, particularly in light of soaring global fertilizer prices due to geopolitical tensions. The ongoing conflict has heightened risks to global food security as both Russia and China maintain export restrictions. The General Staff of Ukraine reported extensive drone engagements, indicating an escalation in military operations. The attack emphasizes the vulnerability of critical industrial facilities amid the ongoing conflict.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Apatit in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…