 Turkiyetoday
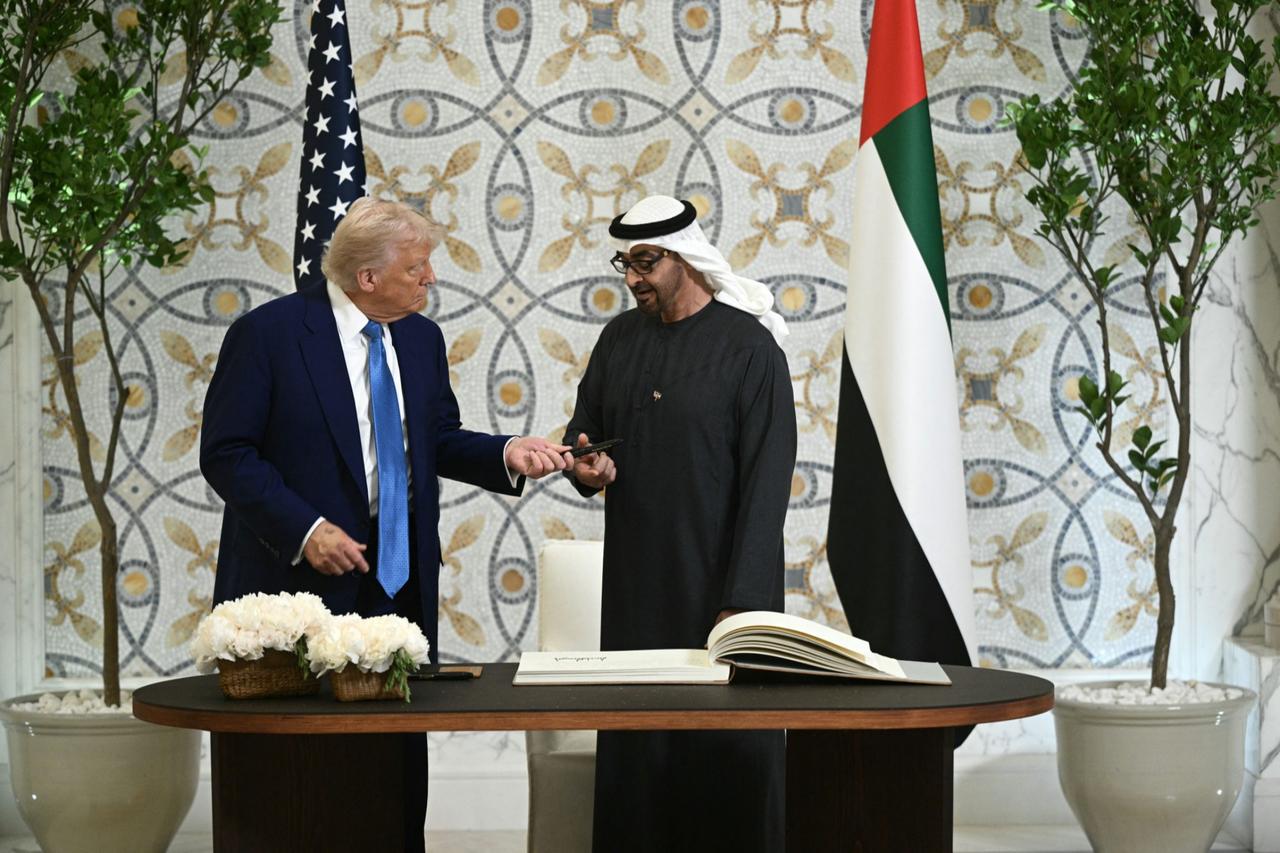
US Eases Export Restrictions on UAE, Enhancing Defense and AI Cooperation
Article Content

- •The U.S. has upgraded the UAE's export status, allowing license-free access to advanced technologies.
- •Restrictions on UAE's drone programs have been lifted, enhancing military collaboration.
- •The UAE is committed to investing in U.S. AI infrastructure as part of the cooperation framework.
On July 11, 2026, the U.S. Department of Commerce announced significant easing of export restrictions on the UAE, reclassifying it as a Major Defense Partner. This change allows the UAE broader access to advanced AI chips, military equipment, and other controlled technologies without export licenses. The updated regulations will support the UAE's unmanned aerial vehicle programs and facilitate license-free exports of dual-use items for oil, gas, and civil nuclear power. The UAE's upgraded status is linked to its commitment to U.S. national security interests, particularly in the context of Operation Epic Fury. The move follows a framework agreement signed in May 2025, which includes substantial investments in AI infrastructure. The UAE is expected to invest in U.S. AI projects, further solidifying the partnership. This policy shift has drawn criticism from some U.S. lawmakers concerned about potential technology diversion to adversaries.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…