 Gbhackers
Malware Spreads via Verified Ads on X Targeting Mac Users
Article Content

- •Malware spread via a verified ad on X, posing as a legitimate Mac app.
- •Victims were misled into executing Terminal commands to install malware.
- •The incident exposes flaws in X's ad approval process and impacts Mac users.
A ClickFix-style malware campaign was detected spreading through a sponsored ad on X, originating from a verified account. The ad masqueraded as the legitimate Mac app DynamicLake, leading users to a malicious domain, dynamicmacisland[.]com. Victims were instructed to execute Terminal commands to install malware, identified as a variant of Atomic Stealer, tracked as MacSync. The incident highlights vulnerabilities in X's ad approval process, allowing malware to bypass automated scans. The developer of DynamicLake expressed concern over the misuse of their brand and urged users to download only from their official site. Jamf Threat Labs and Malwarebytes are investigating the incident, marking it as a significant security breach for Mac users. This is the first known case of malware spread through ads on X, raising alarms about the platform's ad vetting procedures.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track ClickFix and X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
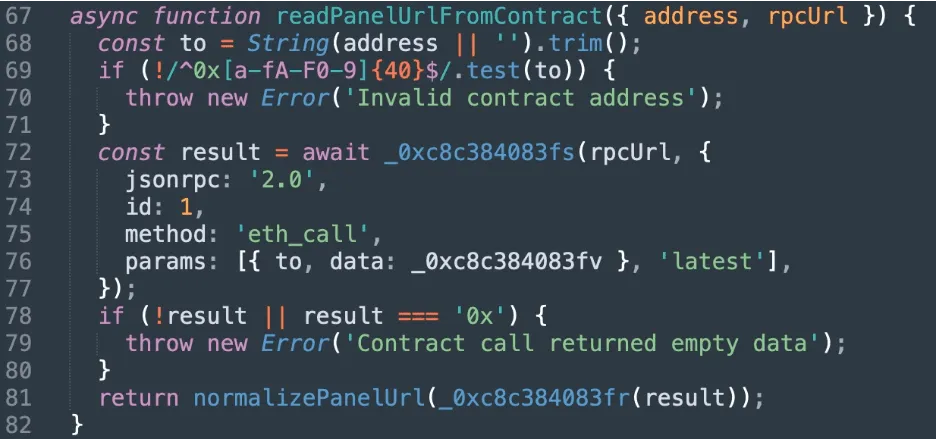 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…
 Cybercriminals Exploit ChatGPT Custom GPTs for ClickFix RAT Attacks A new ClickFix campaign has been discovered that exploits ChatGPT Custom GPTs to impersonate legitimate products, luring users into executing malicious code. Cybersecurity firm Huntress reported that at least 40 users have been infected, with two confirmed incidents linked to Custom GPT instances. The attackers…